How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- SentinelOne is the best direct CrowdStrike alternative, with autonomous AI response and ransomware rollback from $69.99 per endpoint per year, plus strong negotiation flexibility.
- Microsoft Defender suits Microsoft 365 organizations, with enterprise-grade EDR included in E5 or $5.20 per user per month for Plan 2, plus native Azure integration.
- Palo Alto Cortex XDR suits Palo Alto network customers, with deep analytics plus network and cloud visibility in one platform and Unit 42 managed support.
- Sophos Intercept X suits SMBs and mid-market teams, with deep learning plus anti-ransomware at a lower price point and Sophos MDR available.
- Huntress suits SMBs and MSPs that want managed EDR included, while Bitdefender suits cost-conscious teams that want top-rated detection from $22.75 per device per year.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best crowdstrike alternatives
#1SentinelOne Singularity
Best for: Autonomous response4.7/5 on
G2 (213 reviews, checked Oct 2026)
Visit sentinelone.com
Starting price$69.99/endpoint/yr
Free planNo
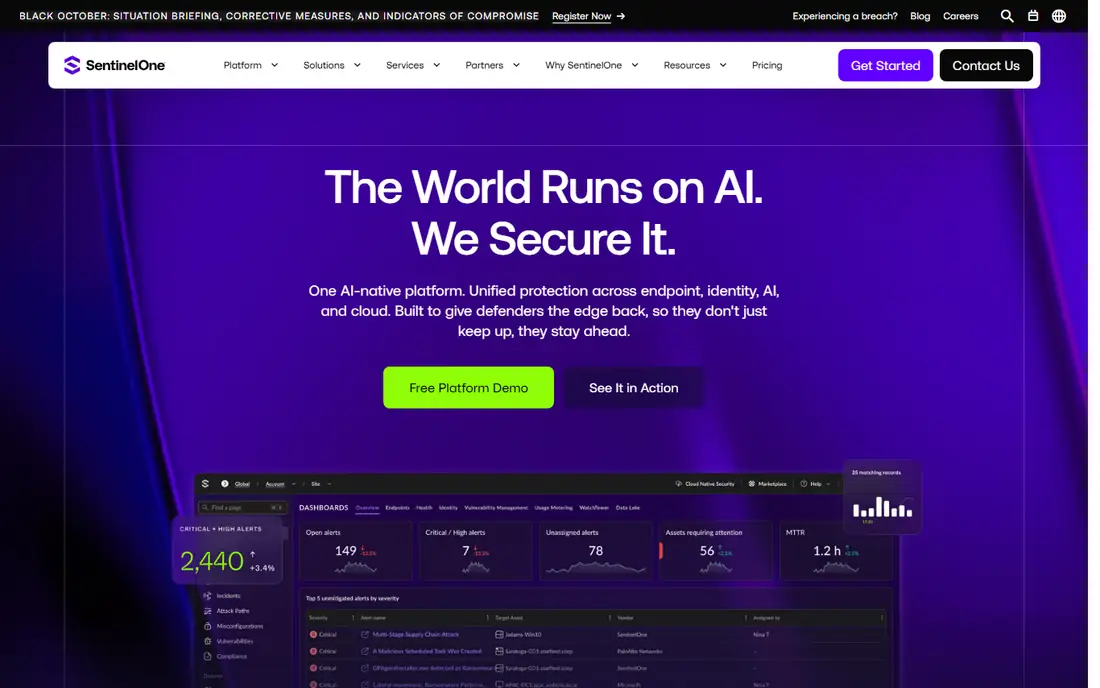
SentinelOne is the best direct CrowdStrike alternative, with autonomous AI response and ransomware rollback that set it apart from simpler antivirus tools. Core starts at $69.99 per endpoint per year by guides, with Control at $6.67 per month and WatchTower managed detection as an add-on, and enterprise volume discounts of 20 to 40 percent apply at annual contracts.
There is no free plan, only demos and trials, and managed detection costs extra. For a team that wants CrowdStrike-class detection with autonomous response and a lower list price, SentinelOne is the closest replacement, and guides note strong negotiation flexibility.
What we like- Autonomous AI response
- Ransomware rollback
- Strong negotiation flexibility
- Full Linux and macOS support
Watch out for- No free plan
- Enterprise volume pricing varies
- MDR is an add-on, not included
#2Microsoft Defender for Endpoint
Best for: Microsoft 365 environments4.4/5 on
G2 (312 reviews, checked Oct 2026)
Visit microsoft.com
Starting price$5.20/user/mo
Free plan30-day trial
Microsoft Defender suits Microsoft 365 organizations, with enterprise-grade EDR that competes directly with CrowdStrike and SentinelOne in MITRE ATT&CK evaluations. Plan 2 costs $5.20 per user per month, while E5 customers get it included, and one guide argues Defender is sufficient for 75 percent of organizations.
Linux and macOS support rates good rather than full, telemetry retention runs 30 days on advanced hunting, and managed detection comes via partners rather than built in. For a team already on Microsoft 365 E5, Defender is the obvious CrowdStrike alternative, since you may already own it.
What we like- Included in Microsoft 365 E5
- Native M365 and Azure integration
- Enterprise-grade EDR by MITRE evaluations
- Per-user pricing
Watch out for- Linux and macOS support rated good, not full
- Telemetry retention 30 days on advanced hunting
- Managed option via partners
Starting priceSee website
Free plan30-day trial
Palo Alto Cortex XDR suits Palo Alto network customers, with behavioral analytics plus network and cloud visibility that fuse endpoint, network, and cloud data in one platform. Unit 42 provides a managed option, and native data fusion suits teams already running Palo Alto firewalls and cloud security.
Pricing is quote-only, with one guide citing around $14 per month entry and $18 per month full EDR, plus ingest charges that make quotes diverge. For a team already on the Palo Alto stack, Cortex XDR integration justifies the quote process. For others, SentinelOne or Defender cost less.
What we like- Behavioral analytics
- Network plus cloud visibility
- Native data fusion
- Unit 42 managed option
Watch out for- Quote-only pricing, around $14 to $18 per month by one guide
- Per-endpoint plus ingest pricing
- Best value only for Palo Alto shops
#4Sophos Intercept X
Best for: SMBs and mid-market4.7/5 on
G2 (837 reviews, checked Oct 2026)
Visit sophos.com
Starting priceSee website
Free plan30-day trial
Sophos Intercept X suits SMBs and mid-market teams, with deep learning plus anti-ransomware and a reputation for best SMB value among EDR guides. Sophos MDR adds managed detection, and the platform covers endpoints, servers, and mobile with full support.
Pricing is quote-only on current pages, with guides citing from around $28 per user per year to $2.33 per month entry, so confirm before budgeting. For a non-specialist IT team that wants strong protection without a security specialist on staff, Sophos is the most accessible CrowdStrike alternative.
What we like- Deep learning plus anti-ransomware
- Best SMB value by guides
- Sophos MDR option
- Full platform support
Watch out for- Quote-only on current pages
- Price guides conflict ($28 per user per year vs $2.33 per month entry)
- Tiered telemetry retention
#5Trend Micro Vision One
Best for: Broad multi-layer protection4.7/5 on
G2 (251 reviews, checked Oct 2026)
Visit trendmicro.com
Starting priceSee website
Free plan30-day trial
Trend Micro Vision One suits teams that want broad multi-layer protection across endpoints, email, servers, and cloud in one platform. Server workload strength suits data center teams, Service One adds a managed option, and guides rate it best for junior teams that need clear workflows.
Pricing is quote-only, with per-endpoint and credit models that vary by deployment, and telemetry retention tiers by plan. For a team with mixed server and endpoint estates, Trend Micro breadth beats narrower EDR-only tools.
What we like- Broad multi-layer protection
- Server workload strength
- Service One managed option
- Junior-team friendly
Watch out for- Quote-only pricing
- Per-endpoint and credit pricing
- Tiered telemetry retention
Starting price$22.75/device/yr
Free plan30-day trial
Bitdefender GravityZone suits cost-conscious teams that want top-rated detection without enterprise pricing, starting from $22.75 per device per year on the small business plan for 10 devices. Bitdefender MDR adds managed detection, and detection ratings consistently rank near the top in independent tests.
The small business plan requires 10 devices minimum, and telemetry retention tiers by plan. For a mid-market team that wants strong detection at a lower price than CrowdStrike or SentinelOne, Bitdefender is the best value pick.
What we like- Top-rated detection
- Great value
- Bitdefender MDR option
- Published pricing on some pages
Watch out for- Small business plan starts at 10 devices
- Mid-market focus
- Tiered telemetry retention
#7Huntress
Best for: Managed EDR for SMBs and MSPs4.8/5 on
G2 (908 reviews, checked Oct 2026)
Visit huntress.com
Starting priceSee website
Free planNo
Huntress suits SMBs and MSPs that want managed EDR included, with human-led threat hunting that catches what automated tools miss. The SMB and MSP focus shows in simple deployment and pricing built for smaller teams, and managed detection comes included rather than as an add-on.
Price guides conflict, citing $8.99 per endpoint per month by one guide and around $39 per month all-in by another, so confirm before budgeting. For a small team without a security analyst, Huntress managed model beats buying a powerful tool nobody monitors.
What we like- Managed EDR included
- SMB and MSP focus
- Human-led threat hunting
- Simple deployment
Watch out for- Price guides conflict ($8.99 per endpoint per month vs around $39 per month all-in)
- No free plan
- Enterprise depth below XDR suites
#8Cynet
Best for: Lean teams wanting XDR plus MDR4.7/5 on
G2 (261 reviews, checked Oct 2026)
Visit cynet.com
Starting priceSee website
Free planFree trial
Cynet suits lean teams that want XDR plus MDR in one tool, with 24/7 managed detection included rather than sold separately. All-in per-endpoint pricing simplifies budgeting, and the lean-team focus shows in deployment and alert handling built for small security teams.
Pricing is quote-only, and the vendor is smaller than CrowdStrike or Palo Alto, which matters for teams that need global support depth. For a lean team that wants one tool plus a managed SOC, Cynet is the most complete small-team package here.
What we like- XDR plus MDR included 24/7
- All-in per-endpoint pricing
- Lean-team focus
- Full platform support
Watch out for- Quote-only pricing
- Smaller vendor than CrowdStrike or Palo Alto
- Telemetry retention included but tiers vary
How we chose
We compared CrowdStrike alternatives on detection quality, response automation, platform coverage, managed options, telemetry retention, and price, using vendor pages and October 2026 EDR and XDR guides, and we flagged price conflicts. We favored tools with published pricing or clear guide ranges, and we flagged where guides conflict, since enterprise pricing varies by contract term and scale, and a single figure can mislead.
How to pick a CrowdStrike alternative
Start with your stack, then your team size. Microsoft 365 E5 teams should shortlist Defender first, since you may already own it. Palo Alto shops should shortlist Cortex XDR. Mid-market and SMB teams should shortlist SentinelOne, Sophos, and Bitdefender. Small teams without analysts should shortlist Huntress and Cynet for managed detection.
Check telemetry retention before you sign
Telemetry retention is where quotes diverge by multiples, and it decides how far back you can investigate an incident. Base tiers often retain only a short window, with extended retention costing more, so confirm retention on your quoted tier, not on the vendor marketing page. A cheap endpoint price with short retention can cost more than a pricier tier with a year of history.
Run a trial on your own endpoints
Detection claims vary by environment, so trial each shortlisted tool on your own endpoints for at least two weeks before committing. Measure false positives, agent performance impact, and alert quality, since a tool that scores well in lab tests may flood your team with noise in production. A trial on your real fleet beats any comparison chart.
Plan your migration before you switch
Switching endpoint agents across a fleet takes planning, since old agents must be removed cleanly and new agents deployed without leaving gaps. Pilot on a small group first, confirm detection and performance, then roll out in waves with rollback ready. A rushed migration leaves endpoints unprotected, which defeats the purpose of switching.
Frequently asked questions
What is the best CrowdStrike alternative?
SentinelOne, for direct replacement with autonomous response and ransomware rollback. Microsoft Defender suits Microsoft 365 teams, Palo Alto Cortex suits Palo Alto shops, and Sophos suits SMBs, so the best pick depends on your stack, team size, and whether you need managed detection.
Is Microsoft Defender good enough to replace CrowdStrike?
For most organizations, yes, especially on Microsoft 365 E5, where Defender is included and competes directly in MITRE evaluations. High-value targets such as financial services, defense contractors, and large healthcare providers may still justify CrowdStrike or SentinelOne detection depth, since attackers target them specifically.
How much do CrowdStrike alternatives cost?
From $22.75 per device per year for Bitdefender small business, through $5.20 per user per month for Defender Plan 2 and $69.99 per endpoint per year for SentinelOne, up to quote-only enterprise pricing for Palo Alto Cortex and Trend Micro. Enterprise volume discounts of 20 to 40 percent apply at annual contracts, so negotiate before accepting list prices.
Do CrowdStrike alternatives include managed detection?
Some do, some do not. Huntress and Cynet include managed detection, while SentinelOne WatchTower, Sophos MDR, and Bitdefender MDR sell it as an add-on. Budget managed detection separately if your team has no security analyst, since an unmonitored tool misses attacks.
Should small businesses use CrowdStrike alternatives?
Yes, and Huntress, Sophos, and Bitdefender suit small teams better than CrowdStrike itself, with simpler deployment and lower prices. Small teams should prefer a managed option over a powerful tool nobody monitors, since detection without response leaves attacks running.
Sources we checked (8)
- https://www.sentinelone.com
- https://www.microsoft.com/en-us/security/business/endpoint-security/microsoft-defender-endpoint
- https://www.paloaltonetworks.com/cortex
- https://www.sophos.com
- https://www.trendmicro.com
- https://www.bitdefender.com
- https://huntress.com
- https://www.cynet.com
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 Palo Alto Cortex XDR
 Bitdefender GravityZone