How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Network detection and response, or NDR, watches network traffic for attacker behaviour that endpoint tools and firewalls miss, such as lateral movement and data exfiltration.
- Darktrace is the best overall pick, with self-learning AI that models normal behaviour for every device and flags deviations without signatures.
- Every vendor in this list sells by quote only, so expect an enterprise sales process and a five figure annual contract.
- A third-party SOC cost guide puts NDR in the $30,000 to $250,000 per year range, with mid-market deployments near $50,000 to $120,000 per year.
- Corelight and Stamus Networks are built on open source detection engines, Zeek and Suricata, which suits teams that want transparency and control.
What is network detection and response software?
Network detection and response software, or NDR, monitors the traffic flowing across your network and looks for the behaviour of an active attacker. It records network metadata and, in many cases, full packets, then uses machine learning, behavioural analysis and threat intelligence to spot lateral movement, command and control traffic, data exfiltration and other activity that a firewall or an endpoint agent misses. When it finds something, it raises an alert with the full context, the devices involved, the traffic that triggered it, and the timeline, so an analyst can investigate and respond. It is the network layer of modern detection, alongside endpoint detection and response.
How much does network detection and response software cost?
Every vendor in this list sells by quote only, and none publishes a list price. A third-party SOC cost guide puts NDR in the $30,000 to $250,000 per year range, with mid-market deployments near $50,000 to $120,000 per year, though your price depends on traffic volume, sensor count and retention. Stamus Networks has an open source core, SELKS, which costs nothing to run yourself, but its commercial support and enterprise features are quoted. Corelight is also built on open source, Zeek and Suricata, with commercial licensing quoted. Budget for an annual contract, not a monthly subscription.
Should you buy NDR or rely on your firewall and EDR?
Buy NDR when you need to see what happens between your devices, not just on them. A firewall sees traffic at the perimeter and an endpoint agent sees what happens on one device, but neither sees an attacker moving laterally from a compromised laptop to a server, or quietly exfiltrating data over an encrypted channel. NDR sees the network as a whole, so it catches the behaviour that spans devices. It does not replace your firewall or your EDR, and the best deployments feed NDR alerts into the same SIEM or SOAR your analysts already use, so one investigation covers all three layers.
How do you deploy NDR without drowning in alerts?
Start with one sensor, a small network segment, and a two week tuning period. The first days will produce a flood of alerts as the platform learns what normal looks like on your network, and most of them will be false positives from backup jobs, scanners and unusual but legitimate traffic. Tune them out with the vendor, build the baseline, and only then expand to more segments. Set a clear rule for what gets an alert, what gets logged silently, and who investigates, or the tool will become another queue nobody reads. A good vendor will run this tuning with you, so ask for it in the trial.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Darktrace | Teams that want self-learning AI that models normal behaviour without signatures | Quote only, Darktrace publishes no list price | No free tier, but a trial is available |
 ExtraHop RevealX | Teams that want full packet visibility with decryption and cloud coverage | Quote only, ExtraHop publishes no list price | No free tier, but a demo is available |
 Vectra AI | Teams that want attack detection built around identities and privileges | Quote only, Vectra AI publishes no list price | No free tier, but a demo is available |
 Corelight | Teams that want open source detection engines, Zeek and Suricata, with commercial support | Quote only, Corelight publishes no list price | No free tier, but a demo is available |
 Cisco Secure Network Analytics | Enterprises that already run Cisco networking and want NDR on the same platform | Quote only, Cisco publishes no list price | No free tier, but a trial is available |
 Arista NDR | Teams that want AI driven NDR with strong cloud and SaaS visibility | Quote only, Arista publishes no list price | No free tier, but a demo is available |
 MixMode | Teams that want AI that learns in real time and scales to very large networks | Quote only, MixMode publishes no list price | No free tier, but a demo is available |
 Stamus Networks | Teams that want an open source core, SELKS, with commercial support on top | Quote only for commercial support and enterprise features; the open source SELKS core is free to run yourself | Yes, the SELKS open source core is free |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
#1
Darktrace
Best for: Teams that want self-learning AI that models normal behaviour without signatures
Visit darktrace.com
Starting priceQuote only, Darktrace publishes no list price
Free planNo free tier, but a trial is available
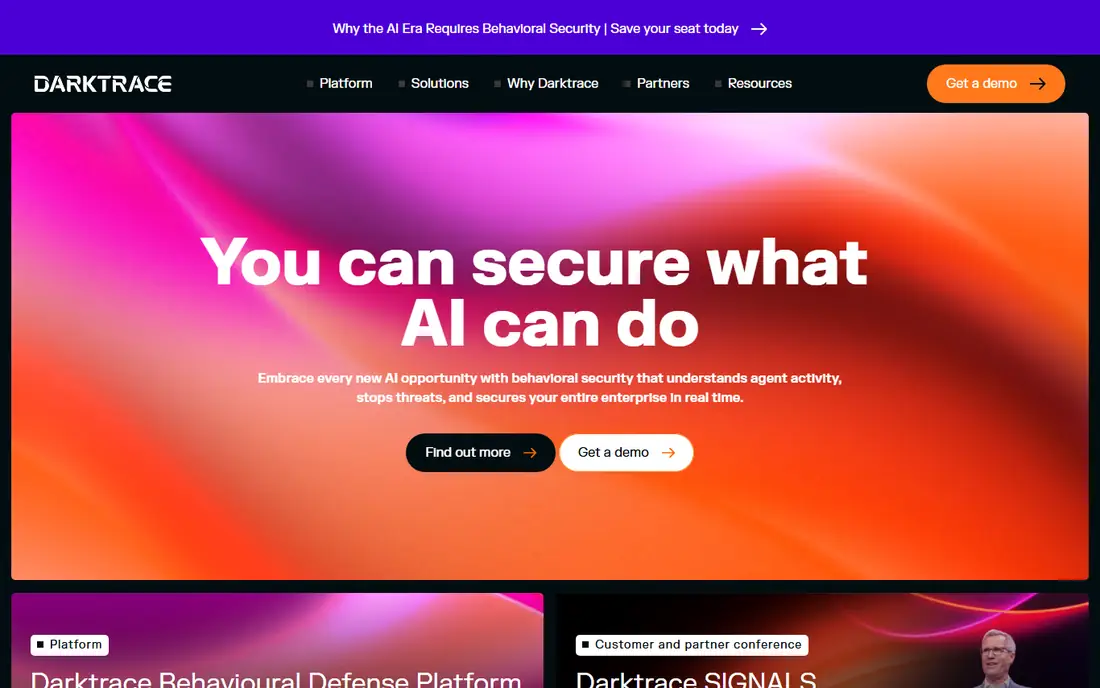
Darktrace is the best known NDR platform and the best overall pick for a team that wants detection without signatures. Its Cyber AI Analyst learns what normal looks like for every device, user and connection on your network, then flags the deviations that look like an attack, including novel techniques that no signature would catch. When it finds a serious threat, its autonomous response can isolate a device or block a connection while your team investigates, which limits damage in the minutes before an analyst responds. Pricing is quote only, and the platform is aimed at mid-market and enterprise buyers.
What we like- Self-learning AI builds a baseline for every device, detects novel attacks without signatures, strong autonomous response that can isolate a device, mature platform with a large customer base
Watch out for- No public price, the AI needs a learning period before alerts are reliable, autonomous response needs careful tuning to avoid disrupting legitimate work
#3
Vectra AI
Best for: Teams that want attack detection built around identities and privileges
Visit vectra.ai
Starting priceQuote only, Vectra AI publishes no list price
Free planNo free tier, but a demo is available
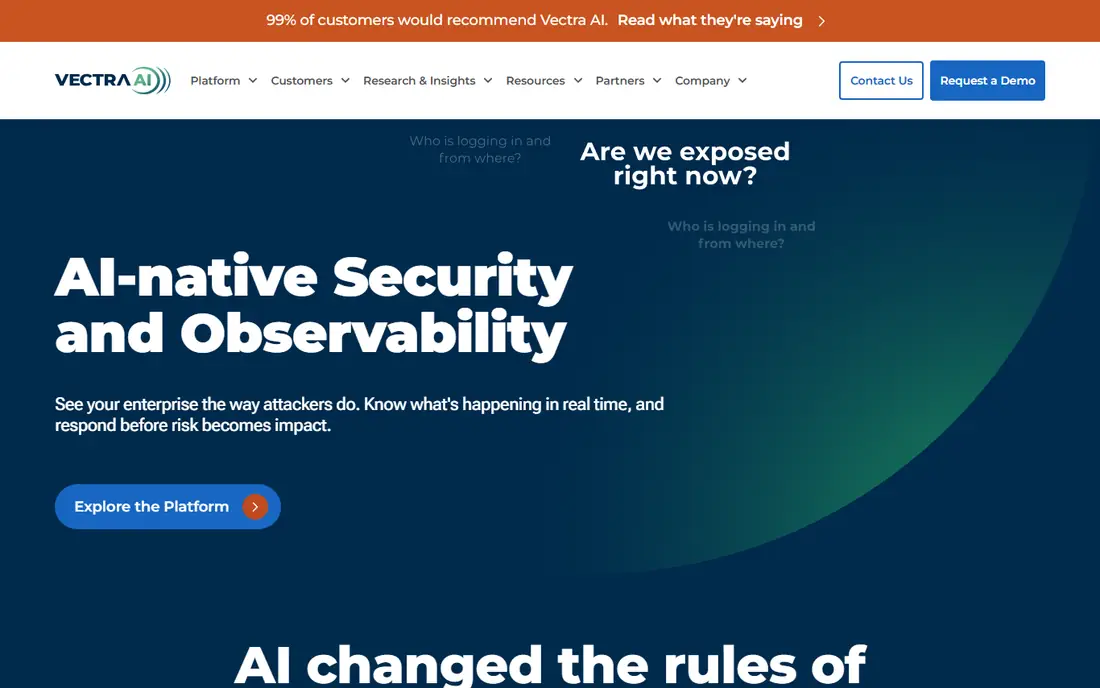
Vectra AI is the strongest choice for identity based attack detection, because it watches how accounts and privileges are used across your network and cloud, and flags the behaviour that looks like an attacker abusing a stolen credential. That matters because most modern attacks start with a compromised identity, not a malware infection, and a tool that watches identities catches the lateral movement and privilege escalation that follow. Its Attack Signal Intelligence scores and prioritises the detections, which cuts the alert noise that buries small teams. Pricing is quote only, and the platform is aimed at mid-market and enterprise buyers.
What we like- Strong focus on identity based attacks and privilege abuse, clear attack signal that cuts alert noise, good coverage of cloud and SaaS, integrates with EDR and SIEM
Watch out for- No public price, the identity focus means it complements rather than replaces packet level NDR, enterprise pricing
#4
Corelight
Best for: Teams that want open source detection engines, Zeek and Suricata, with commercial support
Visit corelight.com
Starting priceQuote only, Corelight publishes no list price
Free planNo free tier, but a demo is available
Corelight is the best choice for a team that wants transparency in its detection, because it is built on the open source Zeek network security monitor and Suricata intrusion detection engine, with commercial support, sensors and a management platform on top. That means your analysts can see exactly what the detection logic does, write their own Zeek scripts, and feed the rich network logs into a SIEM or a threat hunting workflow. It covers on premises, cloud and container networks, and it is widely respected by security practitioners. Pricing is quote only, and the platform expects a skilled team, so a team without network security expertise should compare Darktrace first.
What we like- Built on open source Zeek and Suricata, so the detection logic is transparent, rich network logs that feed SIEM and threat hunting, strong cloud and container coverage, respected by security practitioners
Watch out for- No public price, the open source heritage means it expects a skilled team, enterprise pricing
#5
Cisco Secure Network Analytics
Best for: Enterprises that already run Cisco networking and want NDR on the same platform
Visit cisco.com
Starting priceQuote only, Cisco publishes no list price
Free planNo free tier, but a trial is available
Cisco Secure Network Analytics, formerly Stealthwatch, is the NDR platform for an enterprise that already runs Cisco networking, and it is the best pick in that situation because it uses the telemetry your switches, routers and firewalls already collect. That means you can get network visibility without deploying new sensors, and its encrypted traffic analytics can spot malicious behaviour inside encrypted flows without decrypting them. It integrates with Cisco SecureX and with the major SIEM platforms, so alerts flow into your existing workflow. Pricing is quote only, and the best value is inside a Cisco estate, so a team on another network vendor should compare Darktrace or ExtraHop first.
What we like- Deep integration with Cisco switches, routers and firewalls, uses network telemetry you already collect, strong encrypted traffic analytics, fits a Cisco estate with no new sensors
Watch out for- No public price, best value is inside a Cisco network, the platform is enterprise focused with enterprise pricing
#6
Arista NDR
Best for: Teams that want AI driven NDR with strong cloud and SaaS visibility
Visit arista.com
Starting priceQuote only, Arista publishes no list price
Free planNo free tier, but a demo is available
Arista NDR, built on the Awake Security platform that Arista acquired, is the best pick for a team that wants AI driven detection with strong cloud and SaaS visibility. It builds an entity model of every device, user and application on your network, then uses machine learning to spot the behaviour that does not fit, from a compromised laptop to an unusual SaaS login. That entity focus makes it good at catching the lateral movement and data access that follow an initial compromise. It integrates with Arista networking and with the major SIEM platforms. Pricing is quote only, and the platform is aimed at enterprise buyers, so a mid-market team should compare Vectra AI first.
What we like- AI driven detection built on the Awake Security platform, strong visibility into cloud and SaaS, entity modelling that tracks devices and users, integrates with Arista networking
Watch out for- No public price, the platform is enterprise focused, smaller NDR customer base than Darktrace or ExtraHop
#7
MixMode
Best for: Teams that want AI that learns in real time and scales to very large networks
Visit mixmode.ai
Starting priceQuote only, MixMode publishes no list price
Free planNo free tier, but a demo is available
MixMode is the best pick for a team with a very large network that needs AI that learns in real time, because its third-wave AI updates its model continuously as traffic flows, without the retraining cycles that other machine learning platforms need. That lets it scale to the traffic volumes of a large enterprise or a service provider, and detect novel attacks without signatures. It also supports threat hunting, with analysts able to query the platform for the behaviour they are looking for. Pricing is quote only, and the vendor is smaller than Darktrace or ExtraHop, so a team that wants the largest support organisation should compare those first.
What we like- Third-wave AI that learns continuously without retraining, scales to very large traffic volumes, detects novel attacks without signatures, strong threat hunting support
Watch out for- No public price, the AI approach needs a learning period, smaller vendor than the established NDR platforms
#8
Stamus Networks
Best for: Teams that want an open source core, SELKS, with commercial support on top
Visit stamus-networks.com
Starting priceQuote only for commercial support and enterprise features; the open source SELKS core is free to run yourself
Free planYes, the SELKS open source core is free
Stamus Networks is the best pick for a team that wants to start free and buy support later, because its open source core, SELKS, is free to run yourself, and its commercial support and enterprise features are quoted separately. SELKS is built on Suricata, with a clear detection model, a web interface, and the network logs your analysts need for investigation and threat hunting. That transparency suits a skilled team that wants to understand and control its detection, rather than trusting a black box. The free core needs a team that can run and tune it, so a team without that skill should compare Corelight or Darktrace first.
What we like- Open source SELKS core costs nothing to run, built on Suricata with a clear detection model, commercial support and enterprise features available, transparent pricing for support
Watch out for- The free core needs a skilled team to run and tune, enterprise features are quoted, smaller vendor than the established platforms
Network detection and response software compared
| Tool |
Starting price |
Free plan |
Best for |
| Darktrace |
Quote only |
Trial only |
Self-learning AI |
| ExtraHop RevealX |
Quote only |
No |
Full packet visibility |
| Vectra AI |
Quote only |
No |
Identity based detection |
| Corelight |
Quote only |
No |
Open source engines |
| Cisco Secure Network Analytics |
Quote only |
Trial only |
Cisco estates |
| Arista NDR |
Quote only |
No |
Cloud and SaaS visibility |
| MixMode |
Quote only |
No |
Real time AI at scale |
| Stamus Networks |
Quote only, SELKS free |
Yes, SELKS |
Open source core |
Frequently asked questions
What is the difference between NDR and EDR?
Network detection and response watches the traffic between devices, while endpoint detection and response watches what happens on one device. NDR catches lateral movement, command and control traffic and data exfiltration that spans devices, which an endpoint agent cannot see. EDR catches malware execution, process injection and file changes on a single host, which NDR cannot see. Most teams need both, with the alerts feeding into the same SIEM or SOAR so one investigation covers both layers.
How much does NDR software cost?
Every vendor in this list sells by quote only, and none publishes a list price. A third-party SOC cost guide puts NDR in the $30,000 to $250,000 per year range, with mid-market deployments near $50,000 to $120,000 per year, though your price depends on traffic volume, sensor count, retention and whether you buy a managed service. Stamus Networks is the exception, with its open source SELKS core free to run yourself and commercial support quoted separately.
Do I need full packet capture or is metadata enough?
Full packet capture gives you the deepest investigations, because you can replay the exact packets and see what data left the network. Metadata is cheaper to store and faster to search, and it is enough for most detections. ExtraHop RevealX is the best pick if you want full packets, while Darktrace and Vectra AI work from metadata and behavioural models. Choose full packets if you investigate serious incidents often, and metadata if you need broad coverage on a smaller budget.
How long does NDR take to learn my network?
Most platforms need one to two weeks to build a reliable baseline, and the first days will produce a flood of alerts as the system learns what normal looks like. Backup jobs, scanners and unusual but legitimate traffic will all trigger false positives at first, and your team should tune them out with the vendor before expanding to more segments. A platform that promises instant accuracy is overselling: a baseline needs real traffic over time, so plan for a tuning period in the trial.
Can NDR see inside encrypted traffic?
Most NDR platforms cannot read the content of encrypted traffic without decrypting it, but they can still detect malicious behaviour from the metadata, the timing, the destination and the certificate. Cisco Secure Network Analytics uses encrypted traffic analytics to spot threats without decryption, and ExtraHop RevealX decrypts traffic where you have the keys. For most teams, metadata based detection is enough, and decryption is only needed when you must inspect the content itself.
How we picked
We compared eight network detection and response tools that cover the main ways to buy in this category: self-learning AI, full packet visibility, identity based detection, open source engines, Cisco integration, cloud visibility, real time AI at scale, and a free open source core. Prices were checked against vendor pricing pages and current third-party reads on 20 November 2026. Where a vendor publishes no price, we say so and give the third-party range as a range, never as a vendor price. Prices are search-verified; homepages were not individually opened, so confirm the price on the vendor pricing page before you buy.
Last verified: 20 November 2026
Sources we checked (8)
- https://www.darktrace.com
- https://www.extrahop.com
- https://www.vectra.ai
- https://www.corelight.com
- https://www.cisco.com
- https://www.arista.com
- https://www.mixmode.ai
- https://www.stamus-networks.com
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.