How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Snyk Code at $25 per developer per month is the best developer-first replacement, with fast scans inside the tools developers already use.
- SonarQube pairs security with code quality gates, and its free self-hosted Community Build has no contributor limits.
- Semgrep at $35 per contributor per month is the best pick for teams that write custom security rules and want fast CI scans.
- Checkmarx One suits enterprise compliance programs, but its enterprise pricing only makes sense above roughly 30 to 50 developers.
- Veracode itself is not listed here, since this article covers alternatives to it, not the product itself.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best Veracode alternatives
Starting price$25 per developer per month
Free planYes
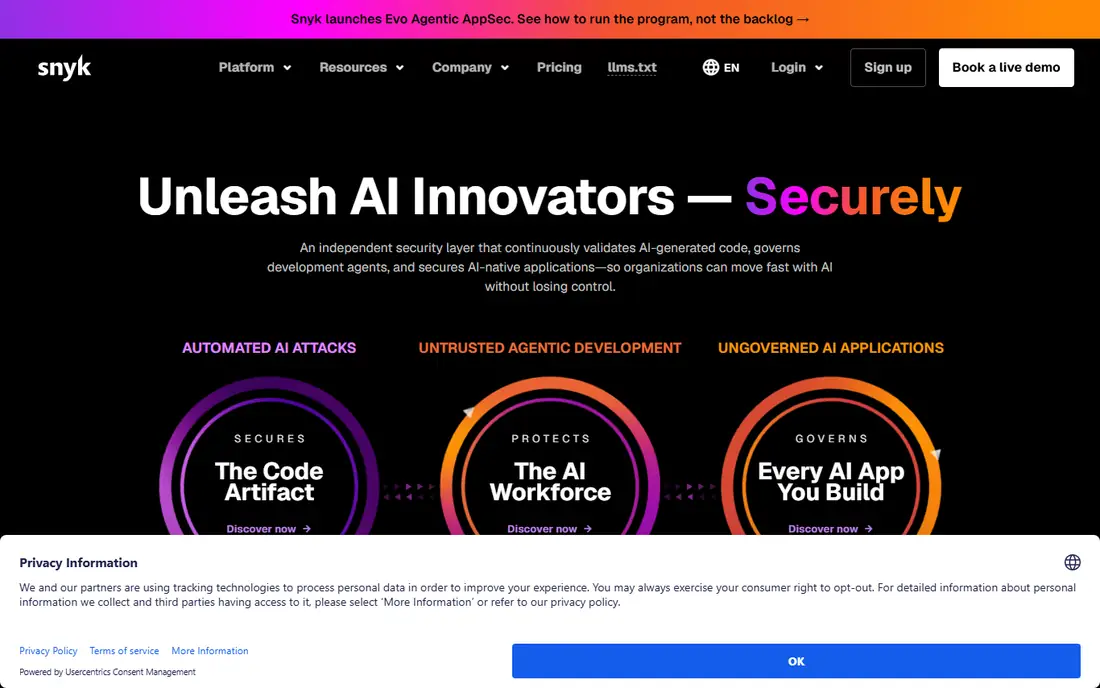
Snyk Code is the developer-first replacement for Veracode. It scans code fast, reports low false positives, and integrates natively into pull requests, so developers fix issues where they work rather than in a separate security portal. Its software composition analysis adds reachability, which shows whether a vulnerable dependency is actually called, cutting noise further.
The Team plan costs $25 per contributing developer per month in guides, with roughly 1,000 tests per month and 100 projects, and enterprise pricing jumps sharply at larger scales. For developer experience and fast feedback, Snyk Code is the best Veracode alternative for most teams.
What we like- Very fast scans with low false positives
- Native pull request integration
- Deep software composition analysis with reachability
Watch out for- Team plan caps tests near 1,000 per month in guides
- Enterprise pricing jumps sharply at scale
- Full platform needs higher tiers
Starting priceFree
Free planYes
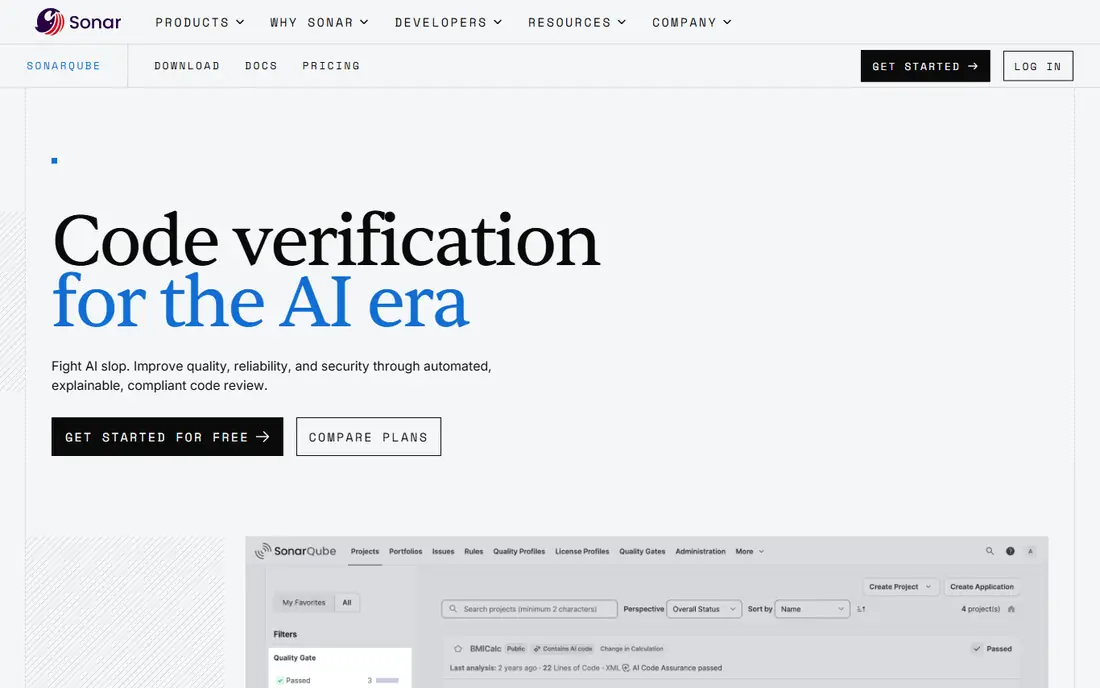
SonarQube is the industry standard for combining code quality with security, and its Community Build is the most generous free option in this category: a full-featured, self-hosted edition with no contributor limits. Quality gates give teams a clear, enforceable definition of done at the pull request level, which both developers and auditors can read.
Paid cloud plans start near $30 per month for the Developer plan in guides, with deeper security analysis and an Advanced Security module on higher tiers. Self-hosting means maintaining servers and tuning rules, and scans can run slower than newer engines. For quality gates plus security at any budget, SonarQube is the first name on the shortlist.
What we like- Free self-hosted Community Build with no contributor limits
- Quality gates give an enforceable definition of done
- 35-plus languages
Watch out for- Self-hosting needs real admin effort
- Scans can be slower than newer engines
- Interface feels dated next to rivals
#3Semgrep
Best for: Custom rules, fast scans4.6/5 on
G2 (56 reviews, checked Oct 2026)
Visit semgrep.dev
Starting priceFree
Free planYes
Semgrep suits teams that want to write their own security rules and scan fast. Its open source engine and community rules cover 30-plus languages, scans run in seconds inside CI, and custom rules let teams encode their own policies, such as banning a dangerous API pattern across the codebase.
The Team plan costs near $35 per contributor per month in guides, and rule writing needs security knowledge to do well. Compliance reporting is thinner than Checkmarx or Veracode. For custom rules and fast developer feedback, Semgrep is the best pick.
What we like- Open source engine with community rules
- Custom rules in minutes
- Scans in seconds inside CI
Watch out for- Team plan near $35 per contributor per month in guides
- Rule writing needs security knowledge
- Smaller compliance reporting than Checkmarx
Starting priceSee website
Free planNo
Checkmarx One is the enterprise platform for teams that need the deepest compliance coverage. It combines static and dynamic testing, software composition analysis, API security, container security, and infrastructure-as-code scanning in one platform, with reporting built for regulated industries.
There is no free tier and no self-service signup, and guides place enterprise pricing from roughly $40,000 per year, with add-ons such as API security and training sold separately. For teams under roughly 30 to 50 developers, that pricing rarely makes sense unless compliance reporting justifies it. For enterprise AppSec programs, Checkmarx is the strongest Veracode replacement.
What we like- Full platform with SAST, DAST, SCA, API security, and container security
- Deep compliance reporting
- 35-plus languages
Watch out for- No free tier and no self-service signup
- Enterprise pricing from roughly $40,000 per year in guides
- Add-ons sold separately
Starting priceSee website
Free planYes
GitHub Advanced Security suits teams already hosting code on GitHub. CodeQL scanning, secret scanning, and Dependabot run inside the repository, with findings appearing in pull requests where developers already work, so there is no separate security portal to learn.
Guides place pricing near $5,880 per year for 10 developers, and value drops sharply for teams on other hosts, while language coverage is narrower than Checkmarx. For GitHub-native teams, it is the most convenient Veracode alternative, since security lives where the code lives.
What we like- CodeQL scanning, secret scanning, and Dependabot inside GitHub
- Native pull request integration
- No separate portal
Watch out for- Pricing sits behind GitHub plans, near $5,880 per year for 10 developers in guides
- Best value only for GitHub teams
- Language coverage narrower than rivals
#6DeepSource
Best for: Automated review with autofixes4.6/5 on
G2 (22 reviews, checked Oct 2026)
Visit deepsource.com
Starting price$30 per user per month
Free planYes
DeepSource automates code review with verified autofixes, so developers approve fixes rather than writing them from scratch. It reports low false positives, scans fast, and integrates natively into pull requests, which suits startups and small teams that want security without a dedicated AppSec engineer.
The Business plan costs near $30 per user per month in guides, language coverage runs to 12-plus languages, narrower than SonarQube or Checkmarx, and the free tier covers only 5 users in guides. For automated review on a budget, DeepSource is a strong pick.
What we like- Automated code review with verified autofixes
- Low false positives
- Fast scans with native pull request integration
Watch out for- Business plan near $30 per user per month in guides
- 12-plus languages, narrower than rivals
- Free tier limited to 5 users in guides
#7Codacy
Best for: Affordable all-in-one4.6/5 on
G2 (31 reviews, checked Oct 2026)
Visit codacy.com
Starting price$15 per user per month
Free planYes
Codacy offers an affordable all-in-one for code quality and security, covering 40-plus languages with fast scans and native pull request integration. It suits teams that want one tool for both quality and security without enterprise pricing or enterprise setup.
The Pro plan costs near $15 per user per month in guides, and depth trails Checkmarx for enterprise compliance programs. For small and mid-size teams that want affordable coverage, Codacy is the best value all-in-one here.
What we like- Affordable all-in-one quality and security
- 40-plus languages
- Fast scans with native pull request integration
Watch out for- Pro plan near $15 per user per month in guides
- Depth trails Checkmarx for enterprise compliance
- Free tier limited to open source repos in guides
Starting priceSee website
Free planYes
Aikido Security focuses on low-noise dependency security, using reachability-based prioritization to show which vulnerabilities actually matter, plus AutoFix pull requests, malware detection, SBOM support, secrets scanning, and cloud and runtime security. That breadth in one platform suits teams tired of alert floods.
Guides place pricing near $3,600 per year for 10 developers, so the starting price here is "See website" until confirmed. It is a newer vendor than Snyk or Checkmarx, and enterprise depth is still growing. For teams that want fewer, better alerts, Aikido is the most promising newer option.
What we like- Reachability-based prioritization cuts noise
- AutoFix pull requests
- Malware detection, SBOM support, secrets scanning, and cloud security
Watch out for- Guide pricing near $3,600 per year for 10 developers, so confirm it
- Newer vendor than Snyk or Checkmarx
- Enterprise depth still growing
How we chose
We started from what Veracode alternatives must do well: find real vulnerabilities in code and dependencies, report few false positives, and fit developer workflows. We compared vendor pages and current 2026 guides, and we favored tools with clear pricing, native pull request integration, and honest limits. We left out dead tools, single-language scanners, and tools whose pricing could not be traced. Prices here come from 2026 guides and vendor pages, and enterprise pricing varies by contract, scan volume, and negotiation, so treat figures as starting points. Veracode itself is excluded, since this article covers alternatives to it. No tool in this list guarantees secure code, and all findings need human review.
How to pick a Veracode alternative
Start with your team size and your compliance needs, not the feature list. A 10-developer startup and a regulated enterprise buy different tools for different reasons.
Match the tool to team size
Under 30 developers, SonarQube Community, Semgrep open source, Snyk Team, or Codacy Pro cover the job at low cost. Above 50 developers with compliance duties, Checkmarx One or a full Snyk platform makes sense, and the per-developer math changes entirely. Checkmarx pricing typically does not make financial sense under 30 to 50 developers unless compliance reporting justifies it.
Pair a scanner with a reviewer
Most teams benefit from combining tools across categories rather than choosing a single replacement. A common pattern pairs a SAST scanner for comprehensive rule coverage with an AI code review tool for contextual analysis that rules cannot capture. SonarQube plus Snyk is a popular combination that covers quality gates, technical debt, deep composition analysis, container scanning, and infrastructure scanning for far less than an enterprise platform pair.
Pilot on false positives, not features
Run each finalist on your own codebase for two weeks and count false positives per real finding. The tool with the lowest noise wins developer trust, and developer trust decides whether findings get fixed. A scanner developers ignore is worse than no scanner, since it creates a false sense of coverage.
Frequently asked questions
What is the best Veracode alternative overall?
Snyk Code for developer experience, SonarQube for quality gates plus security at any budget, and Checkmarx One for enterprise compliance programs. Most teams land on one of those three.
How much do Veracode alternatives cost?
Free tiers exist for SonarQube Community, Semgrep open source, and Snyk limited plans. Paid plans run $15 to $35 per developer per month for developer tools, while enterprise platforms such as Checkmarx start near $40,000 per year in guides.
Can I replace Veracode with a free tool?
Yes, for smaller teams. SonarQube Community plus Semgrep open source covers static analysis and custom rules at zero license cost, though self-hosting and tuning take admin time. Regulated enterprises usually still need a paid platform for compliance reporting.
What is the difference between SAST, DAST, and SCA?
SAST scans source code for vulnerabilities, DAST tests a running application from the outside, and SCA checks third-party dependencies for known vulnerabilities. Veracode and Checkmarx bundle all three, while Snyk Code and Semgrep focus mainly on SAST and SCA.
Why do teams leave Veracode?
Cost is the most common reason in guides, with full platform pricing near $40,000 to $200,000 per year depending on team size. Developer experience is the second reason, since newer tools scan faster and integrate directly into pull requests.
Sources we checked (8)
- https://snyk.io
- https://www.sonarsource.com/products/sonarqube
- https://semgrep.dev
- https://checkmarx.com
- https://github.com
- https://deepsource.com
- https://www.codacy.com
- https://www.aikido.dev
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 Snyk Code
 SonarQube
 Checkmarx One
 GitHub Advanced Security
 Aikido Security