How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- MetricStream itself runs from roughly $75,000 to $1,000,000 per year, so most alternatives here cost less for similar coverage.
- LogicGate Risk Cloud is the only per-user priced option near $12 to $30 per user per month, making it the mid-market value pick.
- Drata and Hyperproof suit fast-growing companies chasing SOC 2 and ISO 27001, with automation that cuts audit prep time.
- Archer and IBM OpenPages serve large enterprises with complex, multi-domain risk programs and module-based pricing.
- No GRC tool replaces judgment: frameworks, evidence quality, and ownership decide audit outcomes more than software choice.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 AuditBoard | All-in-one audit and compliance | $30,000 per year | No |
 LogicGate Risk Cloud | No-code flexible workflows | $12 per user/month | No |
 IBM OpenPages | AI-driven enterprise GRC | $3,300 per year | No |
 Archer | Large enterprise risk programs | $150,000 per year | No |
 ServiceNow GRC | Teams already on ServiceNow | $50,000 per year | No |
 Drata | Automated compliance monitoring | $15,000 per year | No |
 OneTrust | Privacy compliance | $10,000 per year | No |
 Hyperproof | Streamlined risk and compliance | $12,000 per year | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best MetricStream alternatives
#1AuditBoard
Best for: All-in-one audit and compliance4.6/5 on
G2 (1,618 reviews, checked Oct 2026)
Visit auditboard.com
Starting price$30,000 per year
Free planNo
AuditBoard transforms how audit, risk, and compliance teams manage their work, with a modern, connected platform that links controls, risks, audits, and evidence in one place. Mid-to-large companies managing multiple frameworks, such as SOX, SOC 2, and ISO 27001, get a single system instead of spreadsheets and point tools.
The platform's strength is connection: a control tested once feeds every framework that needs it, and audit workflows track evidence, findings, and remediation without manual handoffs. That connected model cuts duplicate work, which is where multi-framework programs usually waste time.
Pricing runs from roughly $30,000 to over $100,000 per year, so AuditBoard is not a small-business tool, and implementation needs planning around existing audit processes. Pick AuditBoard when audit and compliance share one program and connected workflows matter. Pick a compliance automation tool when SOC 2 alone is the goal.
What we like- Audit, risk, and compliance in one platform
- Modern connected workflows
- Strong mid-to-large company fit
Watch out for- Annual cost starts near $30,000
- Implementation takes planning
- Less AI depth than IBM OpenPages
#2LogicGate Risk Cloud
Best for: No-code flexible workflows4.6/5 on
G2 (191 reviews, checked Oct 2026)
Visit logicgate.com
Starting price$12 per user/month
Free planNo
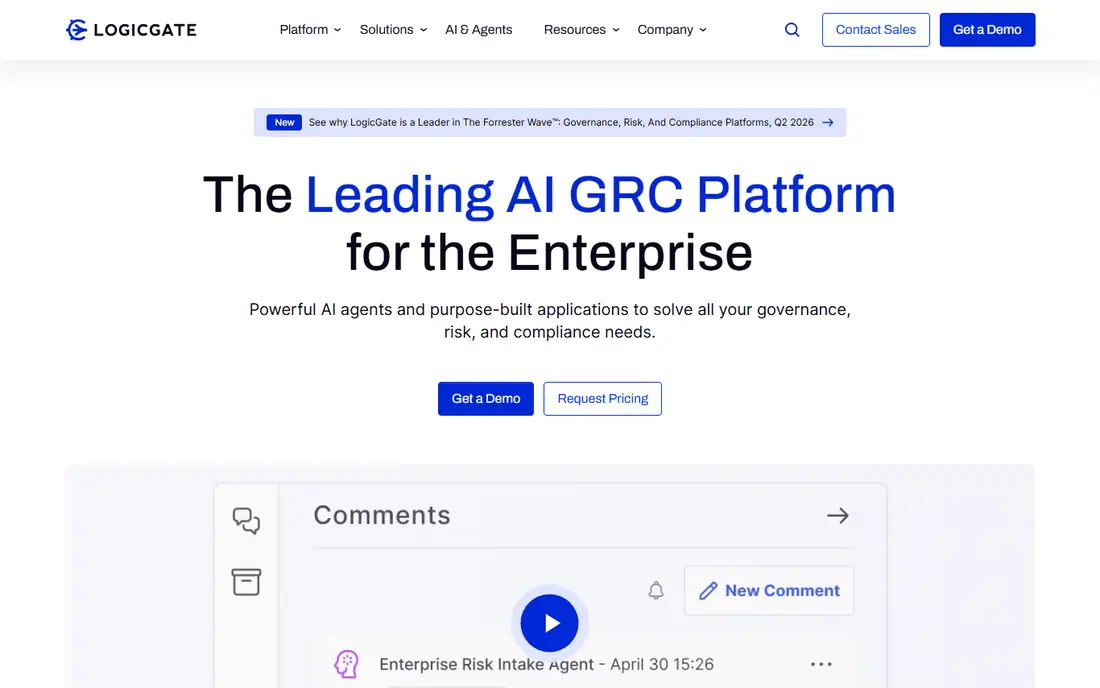
LogicGate Risk Cloud is a no-code GRC platform that lets mid-sized teams build risk and compliance workflows without developers. Drag-and-drop builders create applications for risk assessments, control testing, incident tracking, and third-party reviews, all in one centralized platform.
Pricing near $12 to $30 per user per month makes LogicGate the most accessible enterprise-grade GRC option here. A team that cannot justify five-figure annual contracts can start small and expand workflows as the program matures.
The trade is depth. LogicGate lacks some out-of-box enterprise content and analytics that Archer and IBM OpenPages provide, and reporting needs configuration to match those platforms. Pick LogicGate when flexibility and price matter most. Pick an enterprise suite when prebuilt regulatory content is required.
What we like- No-code workflow builder
- Flexible customization
- Lowest per-user entry here
Watch out for- Less out-of-box enterprise depth
- Reporting needs configuration
- Smaller ecosystem than Archer
Starting price$3,300 per year
Free planNo
IBM OpenPages delivers AI-driven, scalable, centralized GRC across risk, compliance, audit, and third-party domains. Its AI features surface risk patterns across large data sets, and the platform handles multi-domain programs that smaller tools cannot, from operational risk to regulatory compliance.
Pricing spans a wide range, from roughly $3,300 to over $162,000 per year depending on modules and scale, so the entry figure misleads without a scoped quote. That range reflects module-based licensing: a single-domain deployment costs far less than a full enterprise program.
Implementation effort is enterprise-grade, and teams deep in the IBM ecosystem benefit most. Pick OpenPages when AI-driven, multi-domain GRC justifies enterprise investment. Pick LogicGate or Drata when a narrower program needs faster deployment.
What we like- AI-driven insights across domains
- Scalable multi-domain GRC
- Strong regulatory coverage
Watch out for- Wide price range up to $162,000 plus
- Enterprise implementation effort
- IBM ecosystem lock-in
Starting price$150,000 per year
Free planNo
Archer is the long-standing enterprise GRC standard, with more than two decades of deployment history in large enterprises and government agencies. Its platform covers IT risk, cyber risk, third-party risk, and policy management, with AI-driven analytics that correlate control data with regulatory changes and threat feeds.
Module-based pricing means teams pay for what they activate, but enterprise licensing typically starts near $150,000 per year, with $500,000-plus common for large, multi-module implementations. No public self-serve pricing exists, and buying requires a formal RFP and demo cycle.
The legacy is both strength and constraint: Archer's depth and regulatory coverage are unmatched, but some workflows feel dated next to modern platforms. Pick Archer when a large enterprise needs audit-grade, multi-framework risk management. Pick a modern platform when speed and usability matter more.
What we like- Deep risk analytics and broad regulatory coverage
- Module-based pricing
- Decades of enterprise history
Watch out for- Very high cost
- Long RFP and demo cycle
- Legacy complexity in places
#5ServiceNow GRC
Best for: Teams already on ServiceNow4.2/5 on
G2 (119 reviews, checked Oct 2026)
Visit servicenow.com
Starting price$50,000 per year
Free planNo
ServiceNow GRC brings governance, risk, and compliance into the ServiceNow platform, with centralized automated workflows and an AI assistant that maps policies and surfaces risk intelligence. For organizations already running ServiceNow for IT service management, GRC data flows into the same operational picture as incidents, changes, and assets.
That integration is the reason to choose it. Risk intelligence connects to operations rather than living in a separate GRC silo, and workflows reuse ServiceNow's automation engine. Pricing starts near $50,000 per year, with per-user licensing on top for larger teams.
ServiceNow GRC makes little sense for organizations not already on ServiceNow, since the platform cost and implementation assume that base. Pick it when ServiceNow is already the operational core. Pick a standalone GRC tool when it is not.
What we like- Centralized automated workflows
- AI assistant
- Integrates with ServiceNow operations
Watch out for- Best only for existing ServiceNow customers
- Annual cost from $50,000
- Per-user licensing adds up
#6Drata
Best for: Automated compliance monitoring4.7/5 on
G2 (1,392 reviews, checked Oct 2026)
Visit drata.com
Starting price$15,000 per year
Free planNo
Drata automates compliance monitoring for fast-growing companies, with real-time control monitoring and more than 90 integrations that pull evidence automatically. Instead of manual screenshots and spreadsheets, Drata tests controls continuously and flags gaps before an audit.
Pricing runs from roughly $15,000 to over $100,000 per year depending on size and frameworks, which places Drata below enterprise GRC suites but above budget tools. AI-assisted features help teams map controls across frameworks and prepare audit evidence faster.
The framework focus leans toward SOC 2, ISO 27001, and similar security standards, with less depth in broad enterprise risk management than Archer or MetricStream. Pick Drata when continuous compliance automation is the goal. Pick an enterprise GRC suite when operational risk and third-party risk dominate.
What we like- Automation-heavy with real-time monitoring
- 90 plus integrations
- AI-assisted compliance
Watch out for- Annual cost from $15,000
- Less enterprise GRC depth than Archer
- Framework focus leans to SOC 2 and ISO
#7OneTrust
Best for: Privacy compliance4.3/5 on
G2 (155 reviews, checked Oct 2026)
Visit onetrust.com
Starting price$10,000 per year
Free planNo
OneTrust leads on privacy compliance, with AI consent management, privacy automation, and coverage for GDPR, CCPA, and other privacy regulations. For a company whose main GRC burden is privacy, OneTrust's depth in data mapping, consent, and subject-request workflows is unmatched on this list.
Starter pricing near $10,000 per year makes OneTrust accessible to mid-market teams, though enterprise tiers climb past $50,000 per year. The platform also covers broader GRC, but privacy remains its center of gravity.
Operational risk and audit depth are thinner than Archer or AuditBoard, so a team whose program centers on enterprise risk should look elsewhere. Pick OneTrust when privacy compliance drives the purchase. Pick a general GRC platform when risk management leads.
What we like- Privacy automation and consent management
- Mid-market starter pricing
- Broad privacy regulation coverage
Watch out for- Privacy-first focus means thinner operational risk depth
- Enterprise tiers climb past $50,000
- Implementation varies by module
#8Hyperproof
Best for: Streamlined risk and compliance4.5/5 on
G2 (223 reviews, checked Oct 2026)
Visit hyperproof.io
Starting price$12,000 per year
Free planNo
Hyperproof streamlines and centralizes risk management so teams can focus on staying secure and growing, with workflows that link risks, controls, and evidence in one place. It suits fast-growing companies that outgrew spreadsheets but do not need an enterprise GRC suite yet.
Pricing starts near $12,000 per year, placing Hyperproof below AuditBoard and Drata's upper range while offering a fuller GRC workflow than a pure compliance automation tool. The interface favors clarity, which helps small compliance teams adopt it quickly.
The ecosystem is smaller than AuditBoard's, and AI depth trails IBM OpenPages. Pick Hyperproof when streamlined, centralized GRC fits a growing team. Pick a larger platform when enterprise scale or AI analytics dominate the requirements.
What we like- Streamlined risk and compliance workflows
- Centralized evidence
- Fast-growing company fit
Watch out for- Smaller ecosystem than AuditBoard
- Less AI depth than IBM OpenPages
- Pricing from $12,000 per year
How we chose
We compared tools that replace MetricStream's core jobs, risk management, compliance, audit, and policy, using vendor pages and 2026 comparison data. We favored published or widely reported price ranges and marked them as ranges, since GRC pricing is almost always quote-based at enterprise scale. We also split the list by buyer type, enterprise suites versus mid-market and automation tools, because a tool that fits a global bank rarely fits a 200-person SaaS company.
Enterprise suites versus compliance automation
The GRC market splits into two philosophies. Enterprise suites such as Archer, IBM OpenPages, and ServiceNow GRC treat risk as a company-wide program, covering operational risk, third-party risk, policy, and audit in one system. They cost five to six figures, take months to implement, and suit organizations with dedicated GRC teams.
Compliance automation tools such as Drata, Hyperproof, and OneTrust treat a specific outcome, usually SOC 2, ISO 27001, or privacy compliance, as the goal. They automate evidence collection and control testing, deploy in weeks, and suit fast-growing companies with small compliance teams.
LogicGate sits between the two, offering enterprise-style workflows at per-user pricing. AuditBoard bridges audit and compliance for mid-to-large companies. Before buying, name the outcome: a clean audit, a managed risk register, or a privacy program. The outcome picks the category, and the category picks the tool. Buying an enterprise suite for a SOC 2 audit wastes money, and buying an automation tool for enterprise risk leaves gaps auditors will find.
Frequently asked questions
How much does MetricStream cost?
MetricStream pricing is quote-based, with comparisons placing it from roughly $75,000 to $1,000,000 per year depending on modules and scale. Request a scoped quote, since the range reflects very different deployments.
What is the cheapest MetricStream alternative?
LogicGate Risk Cloud near $12 to $30 per user per month is the cheapest per-user option, and OneTrust near $10,000 per year is the cheapest annual starter. Hyperproof near $12,000 per year is close behind. Compare totals at your user count, not just entry prices.
Which alternative is best for SOC 2 compliance?
Drata is the strongest SOC 2 pick, with automated control monitoring and 90-plus integrations. Hyperproof and OneTrust also cover SOC 2, while AuditBoard suits teams managing SOC 2 alongside SOX and ISO frameworks.
Do I need an enterprise GRC suite or a compliance tool?
An enterprise suite fits organizations with dedicated GRC teams, multiple risk domains, and regulatory complexity. A compliance automation tool fits fast-growing companies chasing a specific framework. LogicGate bridges the gap for mid-sized teams that need workflows without enterprise cost.
What frameworks do these tools cover?
Coverage varies, but common frameworks include SOC 2, ISO 27001, NIST, GDPR, CCPA, and SOX. Confirm your exact frameworks on each vendor's page, since depth differs: OneTrust leads on privacy, Drata on security frameworks, and Archer on broad regulatory coverage.
How long does GRC implementation take?
Compliance automation tools deploy in weeks, while enterprise suites take months. Archer and IBM OpenPages implementations often run several months with consulting help, while Drata and Hyperproof teams typically go live far faster. Factor implementation time into the first-year cost.
Sources we checked (5)
- https://www.uprootsecurity.com/blog/governance-risk-and-compliance-tools
- https://www.techno-pulse.com/2026/07/best-ai-grc-software-in-2026-archer-vs.html
- https://www.capterra.ca/alternatives/107345/metricstream-risk-management
- https://auditboard.com
- https://logicgate.com
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.