How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Tufin offers the broadest multi-vendor coverage across heterogeneous estates, strengthened by its acquisition of Skybox technology assets.
- AlgoSec leads on application-centric change automation, with changes requested in business terms rather than IP-and-port tickets.
- FireMon itself leads on real-time change detection, so alternatives compete on automation, modeling, or price rather than that strength.
- ManageEngine Firewall Analyzer sits far below enterprise pricing at $395 per device per year, making it the mid-market pick.
- Skybox Security ceased operations in February 2025, so it is not listed here as a live alternative.
- Enterprise NSPM platforms are quote-based and licensed by managed device count, commonly landing in five to six figures annually for meaningful estates.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best FireMon alternatives
#1
Tufin Orchestration Suite
Best for: Broadest multi-vendor coverage
Visit tufin.com
Starting priceSee website
Free planNo
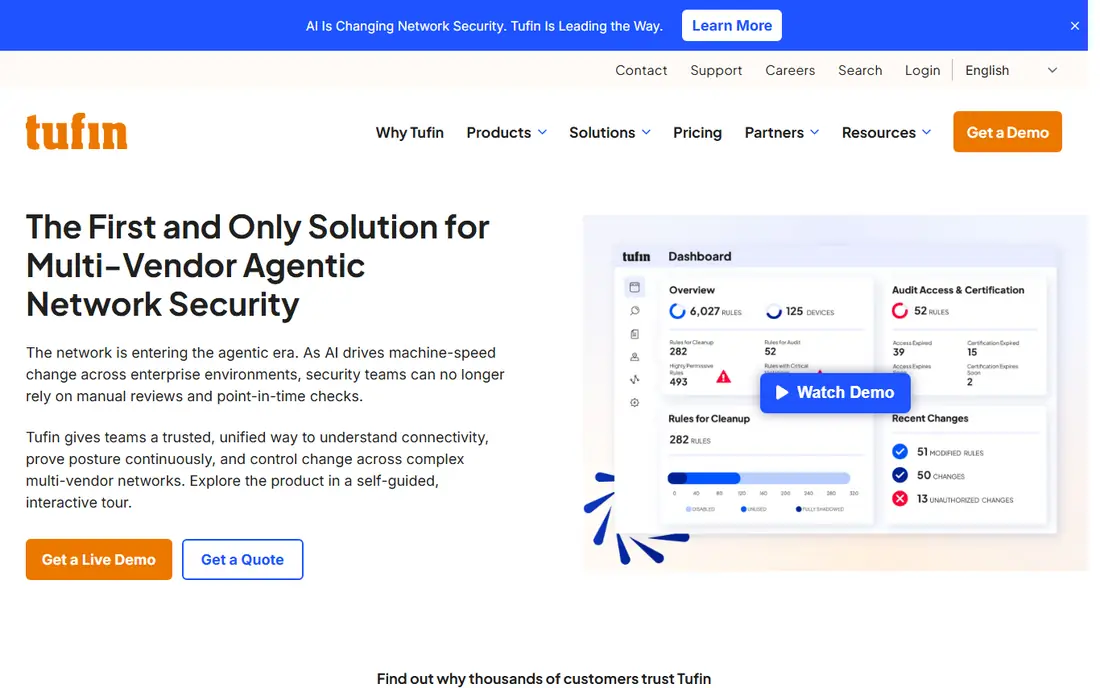
Tufin Orchestration Suite offers the widest device and cloud coverage in network security policy management, which matters most for sprawling multi-vendor estates where breadth beats elegance. It automates policy changes from request through risk analysis to implementation, with topology modeling that shows how a change affects real network paths. Compliance reporting covers common frameworks, and rule cleanup tools surface redundant and risky rules.
Tufin strengthened its position by acquiring Skybox technology assets after Skybox Security ceased operations in February 2025, though no support transfer came with that deal for existing Skybox customers. Pricing is quote-based and enterprise-tier, licensed by managed device count, with a genuine implementation project attached. Organizations still running Skybox should treat migration to Tufin, AlgoSec, or FireMon as an active project rather than a future plan.
What we like- Widest device and cloud coverage
- Multi-vendor policy automation
- Topology modeling
- Compliance reporting
Watch out for- Quote-only pricing
- Genuine implementation project attached
- On-premises deployment with some hybrid options
Starting priceSee website
Free planNo
AlgoSec leads on application-centric change automation. Changes are requested in business terms, such as allowing an application to reach a database, rather than as IP-and-port tickets, and the platform automates implementation with zero-touch deployment where supported. Traffic flow simulation and detailed analytics show the effect of a change before it goes live, which cuts the back-and-forth that plagues manual firewall work.
Published comparisons list AlgoSec starting prices inconsistently, from $4,900 in one older comparison to $14,500 in another, so treat both figures as dated and request a current quote. Pricing is quote-based and enterprise-tier, licensed by device count, and application discovery requires upfront investment to deliver the automation promise. Organizations where application owners queue up network change requests will find AlgoSec the most productive FireMon alternative.
What we like- Strongest change automation
- Application-centric model
- Zero-touch implementation
- Traffic flow simulation
Watch out for- Quote-based enterprise pricing
- Application discovery needs upfront investment
- Interface modernization requested by users
Starting price$395/device/year
Free planNo
ManageEngine Firewall Analyzer is the mid-market pick for teams that need policy analysis without enterprise NSPM pricing. It analyzes firewall rules for redundancy, risk, and compliance, tracks configuration changes, and reports on traffic and security events from firewall logs. The published price of $395 per device per year sits far below the five-to-six-figure annual totals of enterprise platforms, which makes it accessible to mid-market security teams.
Automation depth is thinner than Tufin or AlgoSec, with less zero-touch change implementation and narrower multi-vendor breadth. Teams that mainly need rule cleanup, compliance evidence, and change visibility will find Firewall Analyzer sufficient, while teams that need full change automation across many vendors should budget for an enterprise platform instead.
What we like- Far below enterprise pricing
- Published per-device price
- Rule analysis and compliance reports
- Log analysis included
Watch out for- Less automation depth than Tufin or AlgoSec
- Smaller multi-vendor breadth
- Enterprise features thinner
#4
Cisco Defense Orchestrator
Best for: Cisco-centric estates
Visit cisco.com
Starting priceSee website
Free planNo
Cisco Defense Orchestrator, also called Cisco Secure Firewall Management Center in some comparisons, suits organizations standardized on Cisco firewalls. It centralizes policy management, rule optimization, and change workflows across Cisco devices, with cloud-delivered orchestration that reduces on-premises management overhead. For Cisco-centric estates, native tooling often covers the need without a separate NSPM platform.
Pricing is quote-based, and value drops outside Cisco estates, since multi-vendor coverage is narrower than Tufin or AlgoSec. Teams with a single firewall vendor should first check whether native tools cover their needs at no extra cost before buying a dedicated NSPM platform. Cisco shops that want centralized orchestration will find Defense Orchestrator the natural FireMon alternative.
What we like- Native Cisco firewall management
- Centralized policy across Cisco devices
- Cloud-delivered orchestration
- Strong for Cisco shops
Watch out for- Quote-only pricing
- Limited value outside Cisco estates
- Narrower multi-vendor coverage than Tufin
Starting priceSee website
Free planNo
RedSeal is strongest for network modeling and attack-path analysis alongside Forward Networks. It builds a model of the network from device configurations, then shows which attack paths actually reach critical assets and whether segmentation prevents the paths teams believe it prevents. That verification matters, since misconfiguration is a leading cause of exposure and firewall rules alone do not prove segmentation works.
Pricing is quote-based, and the modeling focus means change automation is thinner than AlgoSec or Tufin. Implementation takes expertise, since model accuracy depends on complete configuration collection. Teams whose main driver is proving segmentation and finding risky paths, rather than automating changes, will find RedSeal the most analytical FireMon alternative.
What we like- Strong network modeling
- Attack-path analysis
- Segmentation verification
- Compliance evidence
Watch out for- Quote-only pricing
- Modeling focus means thinner change automation
- Implementation takes expertise
Starting priceSee website
Free planNo
Forward Networks matches RedSeal on network modeling and verification. It creates a digital twin of the network from configurations, verifies that intended policies hold, and previews the impact of a proposed change before implementation. That preview catches errors that rule lists alone miss, such as a change that opens a path through a different device than expected.
Pricing is quote-based, and the modeling focus again means thinner change automation than Tufin or AlgoSec. Accuracy depends on complete data collection across devices and clouds, so teams with partial visibility should fix collection first. Network teams that prioritize verification over automation will find Forward Networks a strong FireMon alternative.
What we like- Strong network modeling
- Configuration verification
- Change impact preview
- Cloud and on-premises coverage
Watch out for- Quote-only pricing
- Modeling focus over change automation
- Needs complete data collection for accuracy
Starting price$0.065/GB
Free planNo
AWS Firewall Manager suits AWS-centric teams that need central firewall rule management across many accounts. It deploys and manages AWS WAF rules, Shield Advanced protections, VPC security groups, and Network Firewall policies from one console, with compliance reporting across accounts. That central control replaces account-by-account rule editing, which is error-prone at scale.
Pricing starts at $0.065 per GB in published comparisons, with usage-based billing that scales with traffic, plus underlying service charges. AWS Firewall Manager covers AWS only, so hybrid estates with on-premises firewalls need a separate tool or an enterprise NSPM platform. AWS-first teams will find it the most cost-effective FireMon alternative for cloud-only estates.
What we like- Central firewall rule management across AWS accounts
- Usage-based pricing
- Integrates with AWS WAF, Shield, and security groups
Watch out for- AWS-only
- No on-premises firewall coverage
- Pricing scales with traffic
- Narrower than full NSPM
Starting priceSee website
Free planNo
Palo Alto Panorama is the native answer for Palo Alto Networks estates. It centralizes policy management, rule optimization, and unused-rule identification across Palo Alto firewalls, with device groups and templates that scale to large deployments. For single-vendor Palo Alto shops, Panorama often provides the full policy management need at no extra NSPM cost beyond the Palo Alto platform itself.
Panorama covers Palo Alto devices only, so multi-vendor estates still need Tufin, AlgoSec, or FireMon. Dedicated NSPM becomes necessary when teams run multiple firewall vendors, cloud security groups, or formal multi-team change workflows. Palo Alto shops that do not need multi-vendor coverage should use Panorama before buying a separate platform.
What we like- Centralized Palo Alto policy
- Rule optimization
- Unused-rule identification
- No extra NSPM cost for Palo Alto shops
Watch out for- Palo Alto only
- No multi-vendor coverage
- Narrower than dedicated NSPM for heterogeneous estates
How we chose
We compared FireMon alternatives on multi-vendor coverage, change automation, real-time detection, network modeling, compliance reporting, and pricing transparency. FireMon itself starts near $59,995 in published comparisons and leads on real-time change detection, flagging out-of-band changes within minutes, plus strong rule usage analytics for cleanup projects. We therefore weighted automation and modeling strengths that complement or replace that detection focus. Prices come from vendor pages and published comparisons from 2026, and they change often, so confirm the current price before purchase.
How to choose the right FireMon alternative
Start with estate breadth. Single-vendor teams should use native tools such as Panorama or Cisco Defense Orchestrator before buying dedicated NSPM. Multi-vendor teams should shortlist Tufin for breadth and AlgoSec for application-centric automation, and budget implementation services alongside licensing, since enterprise NSPM totals commonly land in five to six figures annually.
Next, decide whether your driver is change automation, detection, or modeling. Detection-driven teams should stay close to FireMon strengths, automation-driven teams should test AlgoSec zero-touch workflows, and verification-driven teams should test RedSeal or Forward Networks modeling. Finally, run a proof of concept with real device configurations, including a risky rule cleanup and a multi-team change request, before signing a multi-year contract.
Frequently asked questions
What is FireMon?
FireMon is a network security policy management platform that automates firewall and cloud security group policies, with real-time change detection and rule usage analytics. Published comparisons list pricing from $59,995.
Is there a cheap FireMon alternative?
ManageEngine Firewall Analyzer at $395 per device per year is far below enterprise NSPM pricing and suits mid-market teams. AWS Firewall Manager at $0.065 per GB suits AWS-only estates at usage-based cost.
Is Skybox still available?
No, Skybox Security ceased operations in February 2025, and its technology assets were acquired by Tufin without a support transfer for existing customers. Organizations still running Skybox should migrate to Tufin, AlgoSec, or FireMon.
Which FireMon alternative is best for change automation?
AlgoSec leads on application-centric change automation, with zero-touch implementation and traffic flow simulation. Tufin leads on breadth of multi-vendor coverage for heterogeneous estates.
Do I need NSPM if I only use one firewall vendor?
Often not. Native tools such as Palo Alto Panorama or Cisco management platforms provide centralized policy, rule optimization, and unused-rule identification within their own estates at no extra cost.
Can I migrate policies from FireMon?
Most tools here support configuration import, API migration, or partner-led migration for policies, rules, and compliance data. Test the import with a sample device group before migrating the full estate.
Sources we checked (0)
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 AlgoSec
 ManageEngine Firewall Analyzer
 RedSeal
 Forward Networks
 AWS Firewall Manager
 Palo Alto Panorama