How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Threat intelligence tools answer different questions: who targets you, which alerts to ignore, what is for sale about you on the dark web, and what infrastructure is about to activate.
- No single provider owns all four questions, and 2026 movement sits in noise-filtering specialists, EU-sovereign platforms, and mid-market dark-web coverage.
- Recorded Future offers the broadest commercial feed coverage, Mandiant offers the deepest incident-response research, and CrowdStrike fuses adversary tradecraft with endpoint telemetry.
- Most enterprise threat intelligence pricing is custom or quote-based, so budget from guide figures and request proposals on the same scope.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
Starting priceSee website
Free planNo
Recorded Future runs the Intelligence Cloud in Core, Professional, and Elite tiers, with a Pathfinder AI assistant for report synthesis and actor-profile drafting. It offers the broadest commercial feed coverage in 2026 vendor comparisons, making it the best fit for always-on feed operations with SIEM integration. Its Triage sandbox, inherited from Hatching, handles high-volume sample processing for mature security operations centers.
Enterprise pricing is the barrier: UK G-Cloud figures list 80,000 to 114,750 pounds per licence, which shows the scale of investment involved, and the platform needs analyst staffing to turn feeds into action. For organizations that want machine-speed, all-source intelligence at scale, Recorded Future is the broadest option here.
What we like- Broadest commercial feed coverage
- Intelligence Cloud tiers
- AI assistant for report synthesis
Watch out for- Enterprise pricing, UK G-Cloud figures of 80,000 to 114,750 pounds per licence show the scale
- Needs analyst staffing
Starting priceSee website
Free planNo
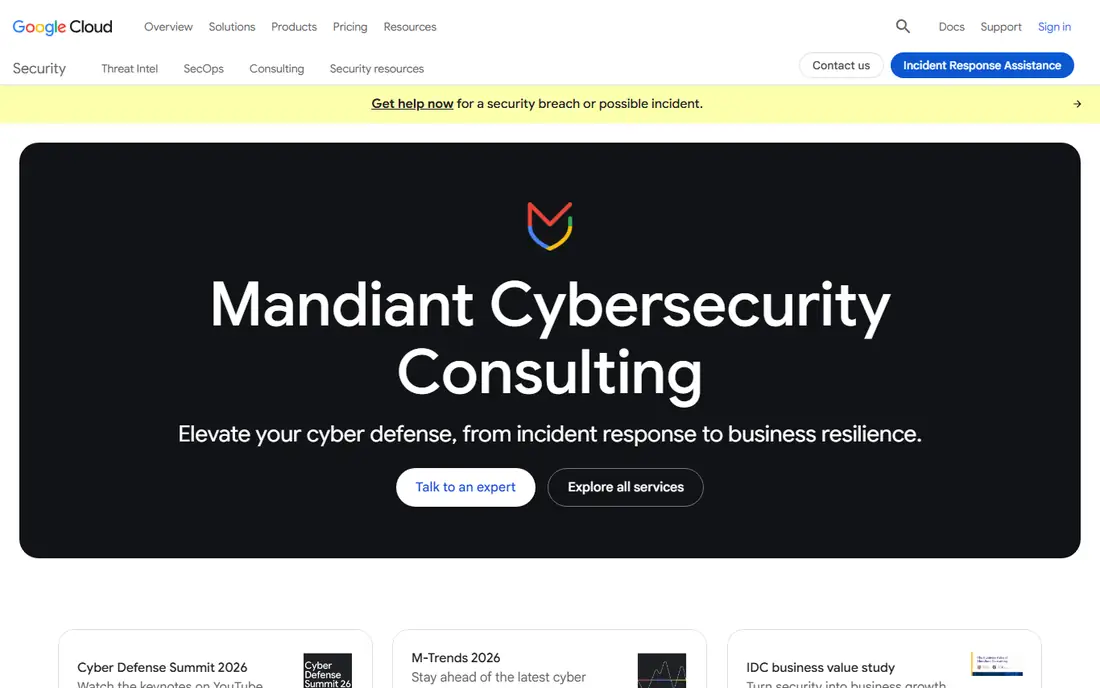
Mandiant, now part of Google Cloud, is the gold standard for incident response and threat intelligence, with researchers behind some of the most significant threat actor discoveries in cybersecurity history. Mandiant Advantage pairs with Gemini in Threat Intelligence for natural language queries, APT report summaries, and actor profiling, while the annual M-Trends report sets industry benchmarks for breach reality. Its DFIR research depth suits frontline breach work.
Pricing is custom quote only and not published, with consulting from $50,000 and enterprise deployments from $100,000 to $1 million in guides, and the Google Cloud acquisition ties recommendations closer to the Google ecosystem. For DFIR-heavy workflows and post-breach response, Mandiant offers the deepest research here.
What we like- Deepest incident-response research
- Annual M-Trends report
- Gemini AI queries and summaries
Watch out for- Custom quote only, not published
- Premium consulting from $50,000
- Ties recommendations closer to Google
#3
CrowdStrike Falcon Adversary Intelligence
Best for: Endpoint-first adversary intelligence
Visit crowdstrike.com
Starting priceSee website
Free planNo
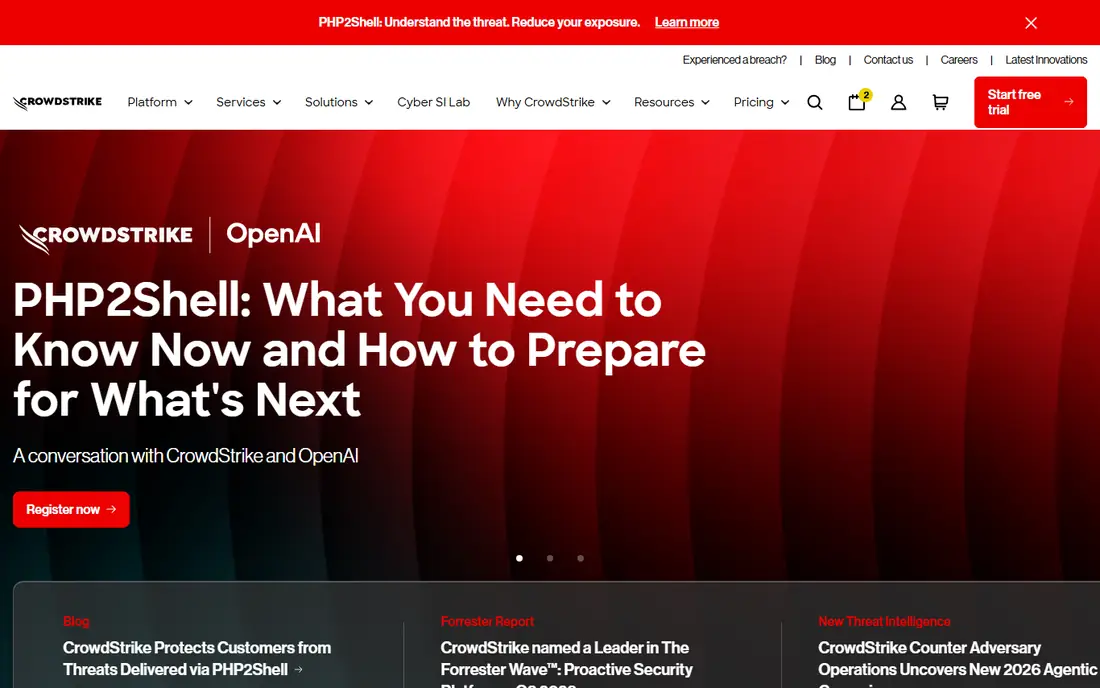
CrowdStrike Falcon Adversary Intelligence Premium pairs with Charlotte AI for natural language queries and triage summaries, plus IBM ATOM integration, and fuses adversary tradecraft with endpoint telemetry from the Falcon platform. Its OverWatch team provides managed threat hunting with 24-hour coverage, and its adversary intelligence database supports attribution for organizations already running Falcon endpoints.
The scope is Falcon-centric, so shops without Falcon get less value, and UK G-Cloud figures list adversary intelligence at 47 to 250 pounds per device per year. For endpoint-first organizations that want tradecraft fused with their own telemetry, CrowdStrike is the strongest fit here.
What we like- Adversary tradecraft fused with endpoint telemetry
- Charlotte AI queries
- OverWatch threat hunting
Watch out for- Falcon-centric scope
- Adversary intelligence pricing of 47 to 250 pounds per device per year in UK G-Cloud
- Enterprise cost
#4
Microsoft Defender Threat Intelligence
Best for: Microsoft-centric shops with E5
Visit microsoft.com
Starting priceSee website
Free planNo
Microsoft Defender Threat Intelligence suits Microsoft-centric shops with E5 licensing, offering broad Microsoft telemetry and a threat graph plus Security Copilot multi-agent orchestration for SOC workflows. As of September 2026, eligible Microsoft 365 E5 customers can use integrated security operations capabilities without a separate Sentinel workspace, which simplifies deployment for existing Microsoft shops.
Full cross-domain XDR correlation needs both Defender for Endpoint Plan 2 and Defender for Office 365 Plan 2 active together, so E5 alone does not cover everything, and Security Copilot costs $4 per SCU per hour provisioned. For Microsoft shops that want intelligence inside their existing stack, Defender TI offers the best integration here.
What we like- Broad Microsoft telemetry and threat graph
- Security Copilot orchestration
- Included in E5 licensing paths
Watch out for- Full XDR correlation needs specific Defender plans together
- Security Copilot at $4 per SCU per hour provisioned
Starting priceSee website
Free planNo
Anomali ThreatStream pairs with Anomali Lens, a browser extension for contextual enrichment, and offers a STIX-native platform with strong ISAC integrations for information sharing communities. It suits organizations that participate in sector sharing groups and need structured threat data that flows into detection and response workflows without manual reformatting.
Pricing is custom enterprise and not published, and the platform shines most for organizations already active in sharing communities. For ISAC-participating organizations with STIX-heavy workflows, Anomali offers the most sharing-native platform here.
What we like- STIX-native platform
- Strong ISAC integrations
- Lens browser extension for enrichment
Watch out for- Custom enterprise pricing, not published
- Needs existing sharing-community participation to shine
Starting priceSee website
Free planNo
ThreatConnect pairs its platform with Polarity, an overlay for natural language querying on the threat intelligence graph, and offers SOAR-heavy integration for organizations with existing security orchestration investment. Its mid-market sweet spot suits companies that need operational intelligence without enterprise-scale budgets, and its workflow automation turns intelligence into detection and response actions.
Pricing is custom enterprise, and its feed breadth trails Recorded Future for all-source coverage. For mid-market organizations with existing SOAR investment that want intelligence woven into automation, ThreatConnect is the best fit here.
What we like- Mid-market sweet spot
- Polarity overlay for enrichment
- SOAR-heavy integration
Watch out for- Custom enterprise pricing
- Mid-market focus means less feed breadth than Recorded Future
Starting priceSee website
Free planNo
EclecticIQ Intelligence Center suits European buyers and regulated industries, with a STIX-native platform and EU-sovereign positioning that matters for organizations with data residency and sovereignty requirements. Its agentic workflow connectors sit on a 2026 roadmap, showing a platform still building automation depth, while its regulated-sector strength covers finance, government, and critical infrastructure use cases.
Pricing is custom enterprise, and its feed breadth is smaller than the US giants. For European buyers and regulated industries that need sovereign intelligence operations, EclecticIQ offers the strongest regional fit here.
What we like- European regulated-sector strength
- STIX-native platform
- EU-sovereign positioning
Watch out for- Custom enterprise pricing
- Smaller feed breadth than US giants
- Agentic workflows on 2026 roadmap
Starting priceSee website
Free planNo
Intel 471 TITAN pairs with research services for AI-assisted forum translation and actor correlation, and offers the deepest criminal-underground forum coverage in 2026 comparisons. It answers the question of who is actually operating in the underground, tracking threat actors across forums and marketplaces that broad feeds cover only thinly. That depth suits organizations whose risk sits in targeted underground activity.
Pricing is custom quote only and not published, and its narrow focus means it complements rather than replaces a broad feed platform. For organizations tracking specific threat actors in the underground, Intel 471 offers the deepest coverage here.
What we like- Deepest criminal-underground forum coverage
- AI-assisted forum translation
- Actor correlation
Watch out for- Custom quote only, not published
- Narrow focus means it complements rather than replaces broad feeds
How we chose
We compared 2026 vendor comparison studies for eleven incumbents, checking feed coverage, AI features, pricing shape, data depth, and best fit. We favored tools with clear intelligence questions answered, published pricing signals where available, and integration depth with SIEM and SOAR platforms. We did not claim hands-on testing, and most enterprise pricing here is custom, so request proposals on the same scope before budgeting.
Start from the sentence you need answered. If the sentence is "tell me who targets us and how," shortlist Recorded Future, CrowdStrike, and Mandiant for tradecraft and attribution. If it is "tell me which alerts to ignore," shortlist platforms with strong SIEM integration and noise filtering, such as Recorded Future and ThreatConnect. If it is "tell me what is for sale about us on the dark web," shortlist Intel 471 and mid-market dark-web coverage. If it is "tell me before the infrastructure activates," shortlist external attack surface tools alongside intelligence feeds, since feeds alone rarely cover that sentence.
Staffing and operationalization matter more than feeds
A feed without analysts becomes noise, so budget staffing alongside licensing: a platform that produces thousands of indicators daily needs triage, enrichment, and automation to turn data into detection rules. Check API access, STIX support, SIEM and SOAR integrations, and analyst accessibility before buying, since a feed that cannot flow into your detection stack adds work rather than reducing it. Pilot with your own alerts and incidents, not vendor demos, to judge whether the tool answers your sentences.
Pricing reality for threat intelligence
Enterprise threat intelligence pricing is custom or quote-based for most vendors here, with guide figures ranging from tens of thousands to hundreds of thousands per year depending on scope, endpoints, and negotiation. Always get multiple quotes, since vendors rarely publish standard pricing, and confirm what the licence covers: seats, feeds, API calls, and support all vary. Mid-market buyers should shortlist ThreatConnect and Microsoft paths first, while enterprise buyers should compare Recorded Future, Mandiant, and CrowdStrike on the same scope.
Frequently asked questions
What is threat intelligence used for?
Threat intelligence tells security teams who targets them, how attackers operate, which alerts matter, and what is exposed about them, so detection and response focus on real risk rather than noise. It feeds SIEM detection rules, incident response, vulnerability prioritization, and executive risk reporting.
Do small companies need threat intelligence tools?
Most small companies need basic threat feeds inside their endpoint or firewall products rather than standalone intelligence platforms, since enterprise tools need analyst staffing. Mid-market companies with a security team should shortlist ThreatConnect or Microsoft paths before enterprise platforms.
What is the difference between threat feeds and threat intelligence platforms?
Threat feeds deliver raw indicators like malicious IPs and hashes, while platforms collect, enrich, correlate, and operationalize those indicators into detection rules, reports, and workflows. A feed without a platform becomes noise, while a platform without good feeds produces polished reports on thin data.
How much do threat intelligence tools cost?
Most enterprise tools cost tens of thousands to hundreds of thousands per year on custom quotes, with guide figures from 47 to 250 pounds per device per year for CrowdStrike adversary intelligence and 80,000 to 114,750 pounds per licence for Recorded Future on UK G-Cloud. Always request multiple quotes on the same scope.
Which threat intelligence tool is best for dark web monitoring?
Intel 471 offers the deepest criminal-underground forum coverage for tracking specific threat actors, while Recorded Future and mid-market dark-web tools cover broader exposure monitoring. Choose Intel 471 for actor tracking and a broader platform for general exposure coverage.
Sources we checked (10)
- https://www.recordedfuture.com
- https://cloud.google.com/security/mandiant
- https://www.crowdstrike.com
- https://www.microsoft.com/security
- https://www.anomali.com
- https://threatconnect.com
- https://www.eclecticiq.com
- https://intel471.com
- https://threatintelagents.com/
- https://cyberpress.org/cti-feeds-to-watch/
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 Recorded Future
 Mandiant Advantage
 Anomali ThreatStream
 ThreatConnect
 EclecticIQ
 Intel 471 TITAN