How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Healthcare-specific tools such as Medcurity and Accountable suit clinics and practices that need HIPAA only, at a lower price than multi-framework platforms.
- Vanta, Drata, Secureframe, and Sprinto suit technology companies that need HIPAA plus SOC 2 or ISO 27001 in one programme.
- Paubox solves a narrower job, HIPAA-compliant email, and pairs well with a broader compliance platform rather than replacing one.
- Audit fees, implementation help, and extra frameworks are often billed separately, so compare total programme cost, not just the software price.
- No software purchase transfers compliance responsibility, so assign an owner for risk, training, and incident response before buying.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Vanta | Technology companies building a multi-framework trust programme | See website | No |
 Drata | Scaling tech teams that want continuous monitoring and audit readiness | See website | No |
 Secureframe | Teams that want compliance software plus expert guidance | $7,500 per year | No |
 Sprinto | Companies that want fast, automated multi-framework compliance | $8,000 per year | No |
 Medcurity | Small and mid-size healthcare organisations that need HIPAA only | $499 per year | No |
 Accountable | Small healthcare teams that want guided HIPAA compliance with a certificate | $169 per month | Free trial |
 HIPAA One | Hospitals and larger practices running annual risk assessments | See website | Free trial |
 Paubox | Healthcare teams that need HIPAA-compliant email without portals | $29 per month | Free trial |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best HIPAA compliance software for healthcare teams
#1Vanta
Best for: Technology companies building a multi-framework trust programme4.5/5 on
G2 (2,742 reviews, checked Oct 2026)
Visit vanta.com
Starting priceSee website
Free planNo
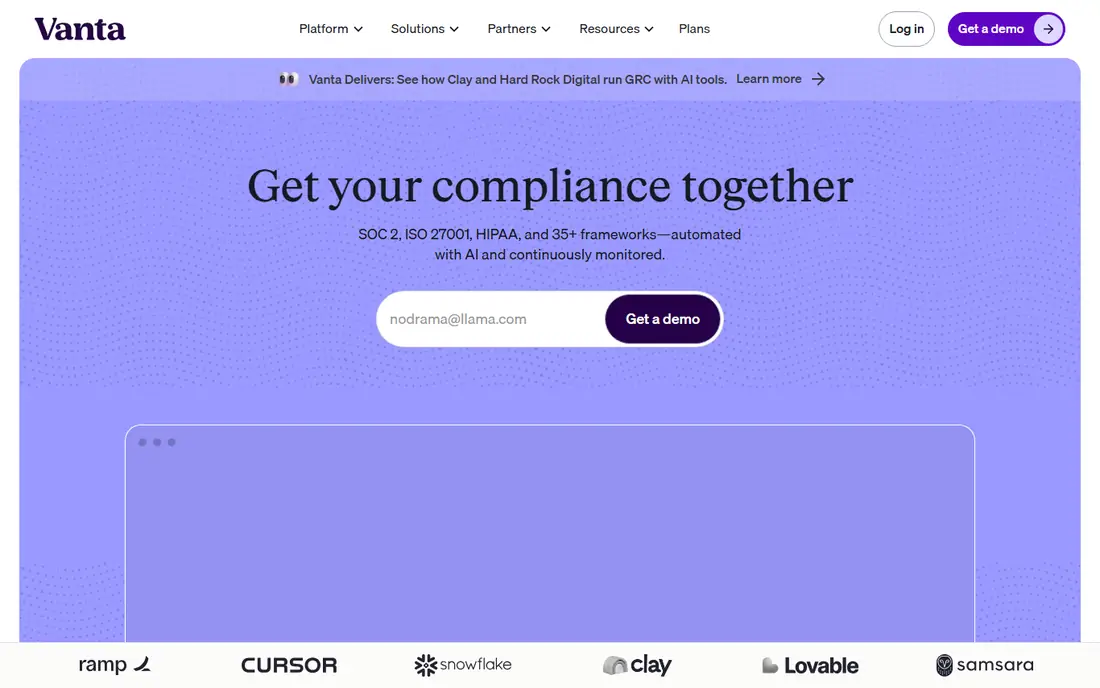
Vanta is the default choice for software companies that must prove HIPAA alongside SOC 2, ISO 27001, PCI, or GDPR. It maps cloud infrastructure to HIPAA controls, collects evidence continuously, and flags control failures as they appear rather than at audit time. An AI agent drafts policies, answers security questionnaires, and surfaces issues, and a trust centre lets customers review security posture without repeated back-and-forth. For a company whose buyers ask for several frameworks, keeping them in one system avoids duplicated work.
Vanta does not publish pricing, and third-party estimates for 2026 range widely, from around $10,000 per year for a single-framework start to far higher for larger teams and more frameworks. Audit fees sit on top. That makes Vanta hard to justify for a small clinic that needs HIPAA alone. For a health-tech company with enterprise buyers, the breadth and auditor network often justify the quote. Ask for a written scope that names frameworks, integrations, and support before signing.
What we like- Very broad framework coverage, hundreds of integrations, strong trust centre for customers
Watch out for- Pricing is quoted, not published, audit fees are separate, more than most clinics need
#2Drata
Best for: Scaling tech teams that want continuous monitoring and audit readiness4.7/5 on
G2 (1,392 reviews, checked Oct 2026)
Visit drata.com
Starting priceSee website
Free planNo
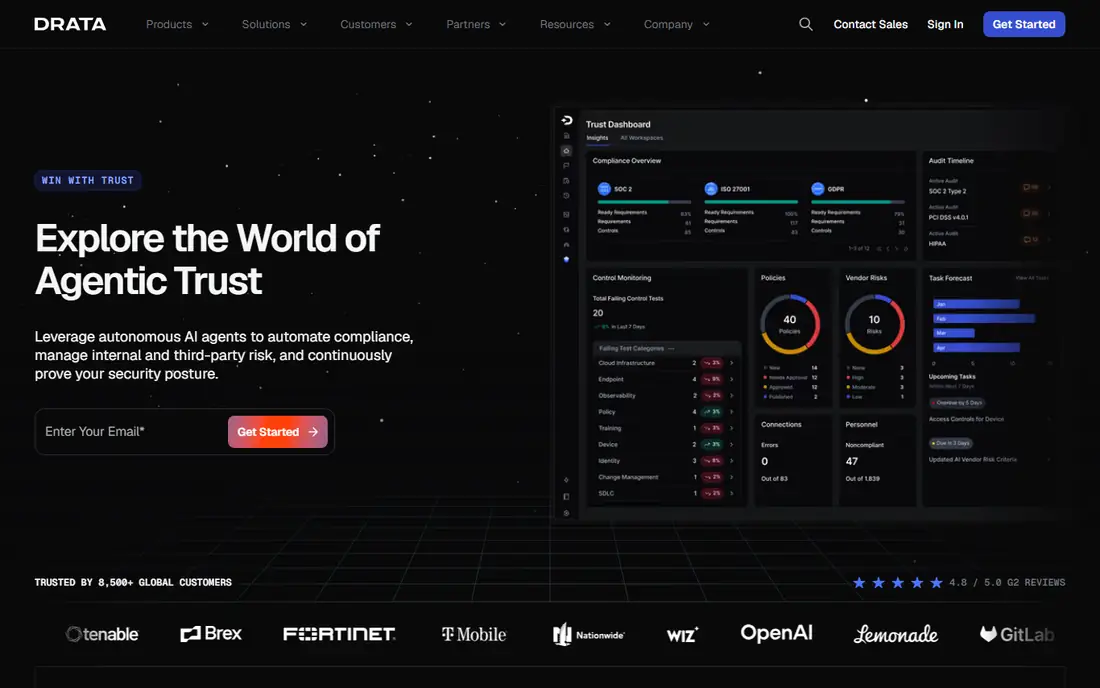
Drata competes directly with Vanta for technology-led compliance teams. It maps controls once and reuses them across frameworks, collects evidence automatically from cloud, identity, and HR systems, and monitors controls continuously so gaps surface early. A trust centre and AI questionnaire help shorten sales security reviews, which matters for companies selling to hospitals and large employers. Reviewers often praise its dashboards and onboarding for teams that already understand compliance basics.
Like Vanta, Drata does not publish list prices, and reported 2026 contracts range from roughly $7,500 to $15,000 per year for startups up to far higher for enterprises, with each added framework adding cost. The honest catch is that automation does not remove implementation work. Scoping, configuration, and auditor coordination still take staff time or a paid partner. Drata fits teams with a security or compliance owner who can drive the programme. Smaller practices will find healthcare-specific tools simpler and cheaper.
What we like- Strong automation and control mapping, continuous monitoring, good auditor network
Watch out for- Pricing is quoted, costs rise with frameworks and headcount, implementation help is extra
#3Secureframe
Best for: Teams that want compliance software plus expert guidance4.7/5 on
G2 (823 reviews, checked Oct 2026)
Visit secureframe.com
Starting price$7,500 per year
Free planNo
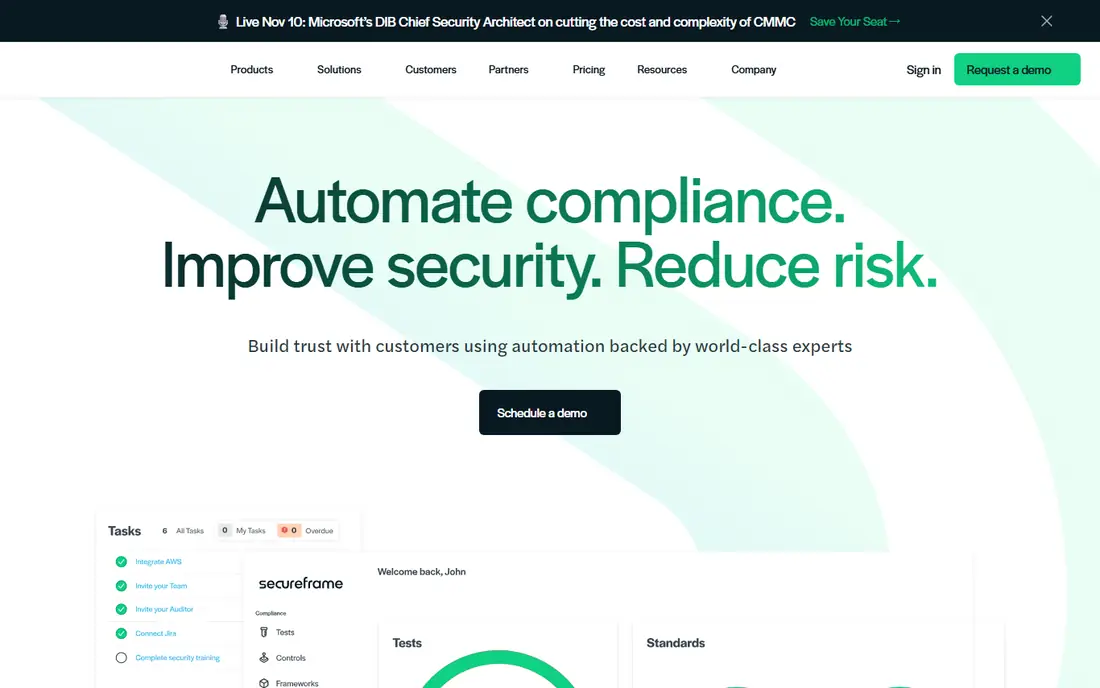
Secureframe blends automation with advisory support, which suits teams without deep in-house compliance expertise. The platform collects evidence across cloud and business systems, monitors controls, and provides policy templates, while experts help with audit preparation and framework questions. Its public packages page lists Fundamentals starting at $7,500 per year, which gives buyers a firmer starting point than fully quoted rivals, though final quotes vary with scope and add-ons.
That guidance is the main reason to choose Secureframe over a pure self-serve tool. A team that is unsure how to scope HIPAA, or that lacks a dedicated compliance hire, gets someone to call when stuck. The trade is breadth. Its integration library and auditor network are smaller than Vanta's, so teams with unusual stacks should confirm coverage before committing. Also check whether bundled advisory overlaps with an existing consultant, to avoid paying twice for the same advice.
What we like- Guided experience with in-house experts, automated evidence collection, HIPAA plus other frameworks
Watch out for- Smaller integration and auditor network than Vanta, advisory may duplicate outside help
#4Sprinto
Best for: Companies that want fast, automated multi-framework compliance4.7/5 on
G2 (1,685 reviews, checked Oct 2026)
Visit sprinto.com
Starting price$8,000 per year
Free planNo
Sprinto positions itself as an autonomous trust platform, monitoring controls continuously, refreshing evidence, and routing approvals without waiting for the next audit cycle. It supports more than 200 frameworks, including HIPAA, SOC 2, ISO 27001, GDPR, and PCI DSS, with 300 plus integrations across cloud, identity, HR, and SaaS tools. Vendor risk, AI governance, and trust centre features sit in the same platform, which suits companies whose compliance scope keeps growing.
Third-party pricing guides put Sprinto around $8,000 per year and above, depending on size and frameworks. For a technology company that needs HIPAA as part of a wider programme, that can undercut larger rivals while keeping automation depth. For a clinic, Sprinto is usually the wrong shape. Its workflows assume a tech stack and a compliance team, not a practice manager juggling patients, staff training, and vendor agreements. Choose Sprinto for breadth and speed, not for healthcare-specific hand-holding.
What we like- Broad framework library, 300 plus integrations, automation-first design
Watch out for- HIPAA is one framework among many, less healthcare-specific workflow than clinic tools
#5
Medcurity
Best for: Small and mid-size healthcare organisations that need HIPAA only
Visit medcurity.com
Starting price$499 per year
Free planNo
Medcurity focuses on one job, helping healthcare organisations complete a Security Risk Analysis and maintain a HIPAA programme through the year. The platform covers administrative, technical, and physical safeguards, with policy templates, training tracking, business associate agreement management, data flow mapping, and incident response planning. Higher tiers add onsite physical security assessments and a dedicated advisor, while the base tier is a self-service automated tool.
The starting price of $499 per year makes Medcurity the most affordable full HIPAA platform on this list, and that matters for small practices and rural providers with tight budgets. The trade is scope. Medcurity does not try to be a general governance platform, so a health-tech company that also needs SOC 2 will still need another tool or a multi-framework platform. For a clinic, practice, or community health centre that needs HIPAA done well and affordably, Medcurity is a strong first look.
What we like- Lowest starting price on this list, healthcare-specific risk assessments, expert support options
Watch out for- No free plan, higher tiers needed for onsite assessments and dedicated advisors
#6
Accountable
Best for: Small healthcare teams that want guided HIPAA compliance with a certificate
Visit accountablehq.com
Starting price$169 per month
Free planFree trial
Accountable guides small healthcare teams through HIPAA step by step, using an AI-assisted setup that customises policies, risk assessments, and training to how the business actually operates. The platform tracks training completion, manages vendors and business associate agreements, maps data flows, and produces audit-ready documentation, with a compliance certificate at the end of the process. Support from a compliance team, including help preparing an audit response, is part of the appeal for teams without a compliance specialist.
Pricing is published and clear. Basic HIPAA starts at $169 per month billed annually, covering 15 employees, with extra seats at $9 per month each. Plus and Pro tiers add monitoring, advanced training, dedicated support, and scheduled security testing at higher monthly rates. The honest catch is seat math. A 50-person practice pays considerably more than the headline rate, so model the full headcount before comparing with flat-rate rivals. For teams under 20 people, Accountable is one of the clearest options available.
What we like- Published pricing, AI-assisted setup, training and agreement tracking in one place
Watch out for- Per-seat costs add up for larger teams, higher tiers needed for monitoring and testing
Starting priceSee website
Free planFree trial
HIPAA One is a cloud suite built around the annual HIPAA security risk assessment, guiding organisations through privacy and security practices across devices, applications, and networks without relying on sampling. It includes workforce training courses, vendor contract management, and remediation tracking, and its service team can perform and manage assessments alongside an internal team. That assessment-first design suits hospitals, health systems, and larger practices that must evidence a thorough yearly review.
Pricing is quoted rather than published as a single list, and third-party figures vary enough that this entry uses See website. A free trial is available for evaluation. HIPAA One will feel less modern than newer platforms, and smaller practices may find Accountable or Medcurity simpler for day-to-day programme management. Where HIPAA One earns its place is rigour at scale, for organisations that need a defensible, organisation-wide assessment record year after year.
What we like- Built for full annual assessments, no sampling shortcuts, training and vendor tools included
Watch out for- Pricing is quoted and varies, older interface feel than newer rivals
#8
Paubox
Best for: Healthcare teams that need HIPAA-compliant email without portals
Visit paubox.com
Starting price$29 per month
Free planFree trial
Paubox solves one HIPAA problem well, which is email that carries patient information. It encrypts every outbound email automatically and works with Google Workspace and Microsoft 365, so staff keep using familiar inboxes and recipients open messages normally, without portals or extra passwords. Higher tiers add inbound protection against phishing, spoofing, and malware, plus archiving and data loss prevention for organisations that need to control what leaves the inbox.
Standard pricing starts at $29 per month billed annually for up to five senders, with Plus at $59 and Premium at $69 per month on the same basis, and a 14-day free trial across tiers. Paubox is not a compliance programme on its own. It does not run a risk analysis, train staff, or manage policies, so pair it with one of the broader tools on this list. For any practice that emails patients, referrals, or insurers, it removes one of the most common sources of accidental exposure.
What we like- Automatic encryption, works with Google Workspace and Microsoft 365, no recipient passwords
Watch out for- Email only, not a full compliance platform, higher tiers needed for archiving and data loss prevention
How we chose
We started from vendor pricing pages and product documentation, then checked claims against public reviews on G2 and Capterra and healthcare buyer discussion. A tool made this list only if it is currently sold and directly supports HIPAA work, whether as a full programme platform or, in Paubox's case, a core safeguard. We favoured published pricing where available and marked quoted pricing as See website rather than copying an unverified figure. We also weighed fit by organisation type, since a tool built for a SaaS company and a tool built for a clinic solve the same regulation in different ways.
What to check before you buy
Start by naming your scope. List the systems that store or transmit protected health information, the vendors that touch it, and the frameworks your customers or partners actually require. A clinic that needs HIPAA alone should not pay for a multi-framework platform, while a health-tech vendor that faces SOC 2 questionnaires as well should not buy a HIPAA-only tool and then add a second platform later. Scope decides the shortlist more than any feature table.
Next, price the whole programme. Ask each vendor what the quote includes and excludes, including implementation, training seats, extra frameworks, and support tiers, and ask separately what an audit will cost. Confirm who owns evidence when an integration breaks, how records export if you leave, and whether business associate agreements are included. Finally, assign an internal owner before signing. Software tracks tasks, but a named person must still review risks, chase training, and lead incident response. Without that owner, even the best platform becomes an expensive filing cabinet.
Frequently asked questions
What does HIPAA compliance software actually do?
HIPAA compliance software organises the work behind compliance, including risk assessments, policies, staff training, vendor agreements, and incident records. Some platforms also monitor technical controls automatically. The software does not grant compliance by itself. The organisation must still follow its policies, fix gaps, and keep records current, and it remains responsible for how patient information is handled.
Do small practices need HIPAA compliance software?
Most small practices benefit from it, because HIPAA requires documented risk analysis, training, policies, and vendor agreements even for a small team. A low-cost healthcare-specific tool such as Medcurity or Accountable is usually enough, while a spreadsheet system often fails at audit time through missing records. The right size depends on headcount, systems, and whether the practice handles electronic health information directly.
How much does HIPAA compliance software cost?
Prices in this guide range from $499 per year for Medcurity to quoted enterprise pricing for Vanta and Drata, with mid-range options such as Secureframe from $7,500 per year and Accountable from $169 per month. Audit fees, implementation help, and added frameworks usually cost extra. Compare total programme cost for the first year, not just the software subscription, before deciding.
Is a HIPAA certificate from a vendor the same as being compliant?
No. A vendor certificate shows that an organisation completed that vendor's process, but HIPAA compliance is an ongoing obligation judged on actual safeguards and records. Regulators and auditors look at risk analyses, policies, training records, and incident handling, not at a badge alone. Treat any certificate as evidence of work done, not as a guarantee against findings.
Can one tool cover HIPAA and SOC 2 together?
Yes, multi-framework platforms such as Vanta, Drata, Secureframe, and Sprinto cover HIPAA alongside SOC 2 and other standards by mapping shared controls once. That suits technology companies selling to healthcare and enterprise buyers. Clinics that only need HIPAA usually pay less with a healthcare-specific tool, since they avoid paying for frameworks they will never use.
What should we ask a vendor before signing?
Ask what the quote includes, how audit support works, how evidence exports if you leave, and whether a business associate agreement is provided. Ask how training, risk assessment, and incident records are tracked, and who at the vendor helps when a control fails. Get answers in writing, and confirm pricing for extra seats, frameworks, and renewal years before committing to an annual contract.
Sources we checked (9)
- https://www.vanta.com
- https://drata.com
- https://secureframe.com
- https://sprinto.com
- https://medcurity.com
- https://www.accountablehq.com
- https://intraprisehealth.com/hipaa-one/
- https://www.paubox.com
- https://medcurity.com/hipaa-compliance-software-pricing-guide/
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.