How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Application detection and response, or ADR, protects running applications from inside, judging attacks with code-level context that a firewall alone cannot see.
- Contrast Security offers the deepest dedicated in-process protection, while Datadog and Dynatrace deliver runtime security through agents you may already run.
- Audit your existing observability subscriptions before buying: Datadog and Dynatrace estates often own runtime security capability that was never activated.
- Start in monitor-only mode on one critical app, measure overhead and false-block rates against real traffic, then graduate to blocking where evidence supports it.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
Starting priceSee website
Free planNo
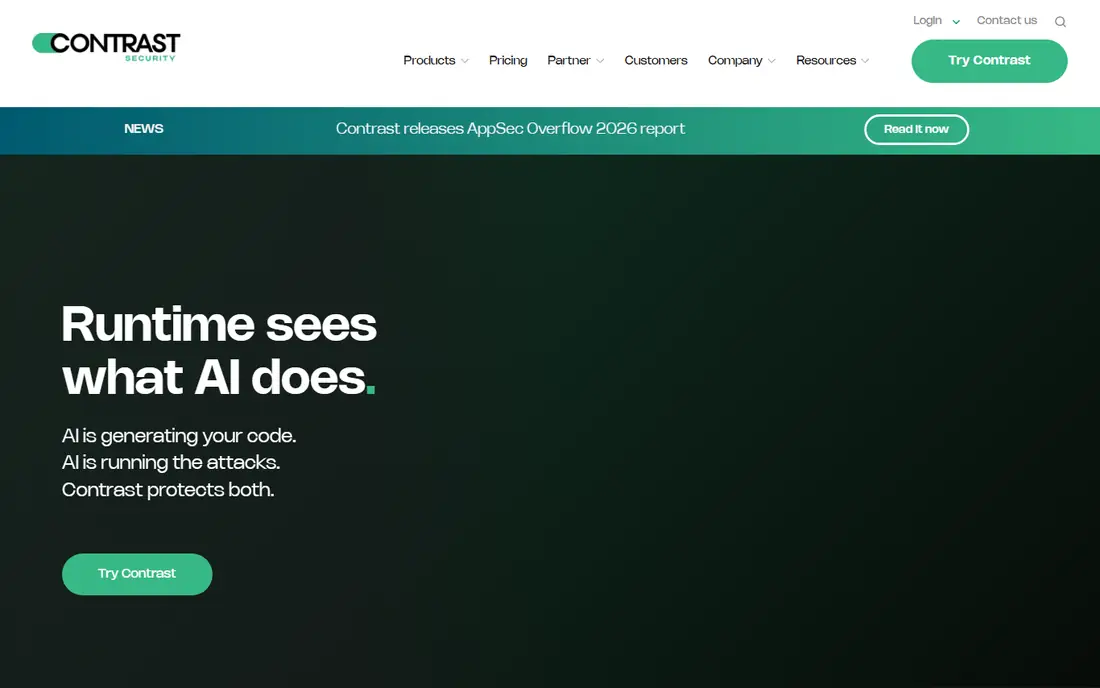
Contrast Security is the dedicated pick, offering the deepest in-process depth among runtime protection tools, with a dedicated ADR product alongside its IAST testing product. Because the agent runs inside the application, it sees what the application actually executes, distinguishing real exploits from scanner noise with code-level context that edge tools cannot match. A new agent is available for current deployments, and pricing is per app.
The trade-offs are procurement and operations: pricing is per app and quote only, and each app needs agent deployment and tuning. For organizations where in-process context is the requirement, such as high-value applications facing targeted attacks, Contrast is the tool that 2026 runtime comparisons rank first for depth.
What we like- Deepest in-process depth among dedicated tools
- Dedicated ADR and IAST products
- New agent available
- Per-app pricing
Watch out for- Per-app pricing, quote only
- New agent deployment per app
- Dedicated platform adds a vendor to manage
Starting price$36 per host per month
Free planNo
Datadog Application Security Monitoring, built on acquired Sqreen technology, is the strong option if you already use Datadog for APM, since no new agent is needed: the APM agent you run gains runtime security with trace context. APM standalone starts at $36 per host per month billed annually, with Pro at $41 and Enterprise at $47, and infrastructure monitoring starts at $15 per host per month.
The honest catch is the bill: Datadog prices per product per host, so a 50-host footprint running APM Pro plus infrastructure plus logs lands in five figures monthly. Security depth is good rather than deepest. For cloud-native teams already standardized on Datadog, turning on ASM is the fastest path to runtime protection.
What we like- No new agent needed if you run Datadog APM
- Trace-context runtime security
- 14-day trial
- 800-plus integrations
- APM standalone from $36 per host per month annual
Watch out for- Usage-based pricing compounds with hosts and products
- Security depth is good, not deepest
- Bill needs a spreadsheet to model
#3
Dynatrace Application Security
Best for: Observability teams with Dynatrace
Visit dynatrace.com
Starting priceSee website
Free planNo
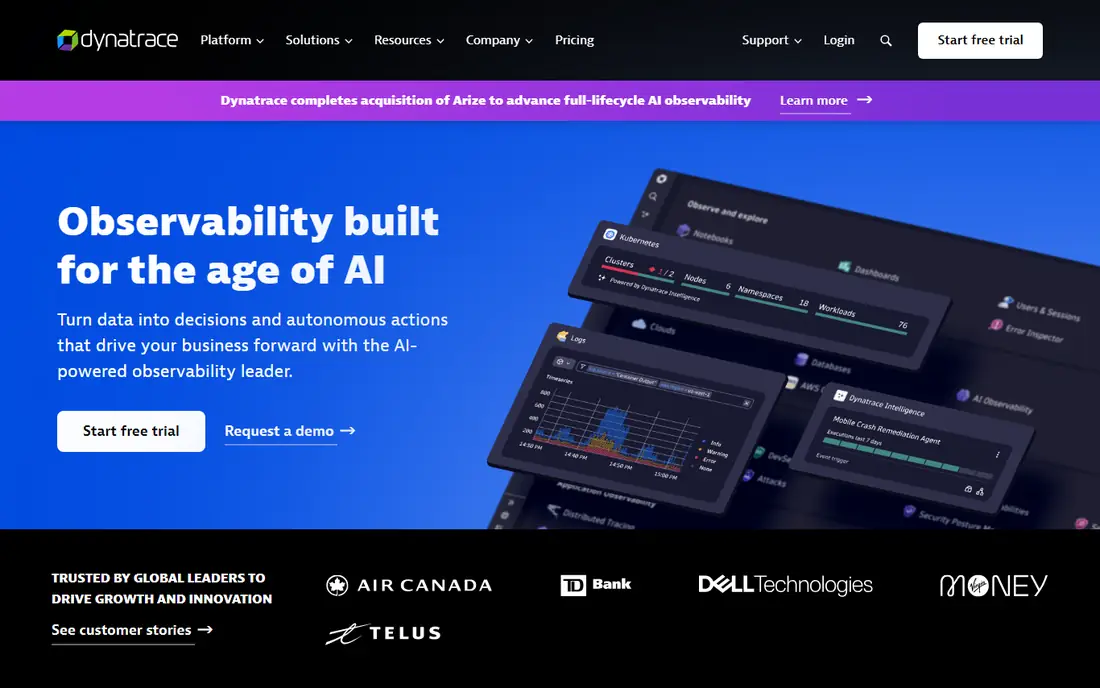
Dynatrace Application Security fills the same role as Datadog ASM on the Dynatrace platform: runtime security delivered through OneAgent, with no new agent to deploy, using exposure-based analysis that ties vulnerabilities to whether code paths are actually reachable in production. That exposure view helps teams prioritize fixes that matter over theoretical findings.
Pricing is usage-based and not published as a simple starting figure, and depth is good rather than deepest compared with Contrast. Full value needs the Dynatrace platform. For Dynatrace estates, activating application security is the lowest-friction ADR upgrade available.
What we like- No new agent needed with OneAgent
- Exposure-based runtime security
- Application context from observability data
- Usage-based pricing
Watch out for- Usage-based pricing
- Depth is good rather than deepest
- Full value needs the Dynatrace platform
Starting priceSee website
Free planNo
Waratek is the specialist pick for JVM workloads, offering JVM-deep runtime protection with a new agent, and it remains the choice where Java applications cannot redeploy for patching. Its runtime patching approach protects legacy Java without code changes, which matters for old applications whose owners cannot rebuild them on demand.
Pricing is quote only, the focus is JVM-only, and the ecosystem is smaller than platform rivals. For organizations with legacy Java estates that cannot be patched normally, Waratek is the specialist that keeps those applications defensible.
What we like- JVM-deep protection
- New agent available
- Suits legacy Java that cannot redeploy
- Runtime patching without code changes
Watch out for- Quote-only pricing
- JVM-only focus
- Smaller ecosystem than platform rivals
Starting priceSee website
Free planNo
Fastly, including its Signal Sciences heritage, provides service-layer protection at the edge, absorbing volumetric noise cheaply before it reaches applications and judging requests at the service layer. Module-based deployment and tiered pricing make it easy to add to an existing edge setup, and it pairs well with in-process ADR rather than replacing it.
Service-layer depth is shallower than in-process agents, since the edge cannot see inside application execution. Treat Fastly as the outer layer: it handles broad coverage and volumetric attacks, leaving the in-process agent to judge requests that deserve code-level scrutiny. For edge-first architectures, it is the strongest edge ADR complement.
What we like- Service-layer protection at the edge
- Module-based deployment
- Tiered pricing
- Absorbs volumetric noise cheaply before it reaches apps
Watch out for- Service-layer depth is shallower than in-process agents
- Edge protection complements rather than replaces ADR
- Tiered pricing needs scoping
Starting priceSee website
Free planNo
Jscrambler is the client-side pick, defending the browser layer where traditional server-side RASP cannot see: JavaScript protection, anti-tampering, client-side threat monitoring and script integrity controls for payment pages. With PCI DSS 6.4.3-era requirements making payment-page script defense a compliance line item, this layer is now a requirement for payment environments, not an optional extra.
It is browser-only and not a replacement for server-side RASP, it needs a separate budget line, and JavaScript build integration is required. For organizations running payment pages or script-heavy web applications, Jscrambler covers the attack surface that server tools miss.
What we like- Dedicated client-side security
- Payment-page script defense
- Addresses an attack surface traditional RASP misses
- Tiered pricing
- Strong for PCI DSS 6.4.3-era requirements
Watch out for- Browser-only coverage, not a replacement for server-side RASP
- Requires a separate budget line
- JavaScript build integration needed
Starting priceSee website
Free planNo
Oligo Security is a runtime-deep ADR vendor purpose-built for application detection and response on modern stacks, with a new agent and runtime-level visibility into application behavior. As a newer entrant, it competes on ADR focus rather than platform breadth, which suits teams that want runtime protection as a dedicated capability.
Pricing is quote only, the vendor track record is shorter than Contrast's, and language coverage needs checking against your stack, since Java and .NET have the broadest RASP coverage while Go and Rust options are limited. For modern-stack teams evaluating dedicated ADR beyond the established names, Oligo deserves a pilot.
What we like- Runtime-deep ADR
- Modern stack coverage
- Purpose-built for application detection and response
- New agent available
Watch out for- Quote-only pricing
- Newer vendor with a smaller track record than Contrast
- Coverage by language needs checking
#8Checkmarx
Best for: Platform runtime context4.2/5 on
G2 (49 reviews, checked Oct 2026)
Visit checkmarx.com
Starting priceSee website
Free planNo
Checkmarx is the platform pick, offering correlated runtime context alongside its broader application security suite, including IAST and static analysis. For organizations already standardized on Checkmarx for testing, adding runtime context keeps findings, correlation and remediation in one platform rather than adding a separate ADR vendor.
Pricing is quote only, runtime context is correlated rather than deepest in-process depth, and platform breadth adds complexity for teams that only need ADR. For platform buyers who value one vendor across testing and runtime, Checkmarx is the most coherent choice.
What we like- Platform with correlated runtime context
- Broad application security suite
- IAST and runtime correlation
- Enterprise customer base
Watch out for- Quote-only pricing
- Runtime context is correlated rather than deepest in-process
- Platform breadth adds complexity
How we chose
We ranked tools by runtime depth, deployment realism and estate fit, using 2026 RASP and ADR comparisons that rated Contrast deepest for dedicated in-process protection, Waratek JVM-deep, Datadog and Dynatrace good via existing observability agents, Fastly service-layer at the edge, and Jscrambler browser-layer for client-side defense. Pricing is quote-based for most dedicated tools, with Datadog APM standalone from $36 per host per month annual as the only published starting figure here.
We also excluded stale names: K2 is pruned from current shortlists, Hdiv has been absorbed, and Imperva RASP is ruled out for new procurement after its 2025 end-of-life announcement, per 2026 comparisons. OpenRASP, the only free option, has been unmaintained since January 2022 and is viable for evaluation, not production, so it is not listed as a production pick. No tool here was used hands-on in production for this guide.
What to check before you buy
Audit what you already own first. Datadog and Dynatrace estates often own runtime security capability that was never activated, and platform suites often include runtime context unlicensed. Turning on what you own beats buying a new platform.
Then pilot in monitor-only mode on one tier-one application. Measure overhead and false-block rates against real traffic for a sprint, then graduate to blocking on the routes where evidence supports it. Teams that flip global blocking on day one usually flip it off by day ten. Pair every in-process layer with your web application firewall rather than replacing it, and budget the client side separately for payment pages.
Frequently asked questions
What is application detection and response?
Application detection and response, or ADR, monitors running applications from inside, detecting and blocking attacks with code-level context. It evolved from runtime application self-protection, or RASP, adding detection, correlation and response workflows for security teams.
What is the best ADR tool in 2026?
Contrast Security offers the deepest dedicated in-process protection. Datadog ASM and Dynatrace Application Security are best if you already run those observability agents, Waratek is best for legacy JVM workloads, and Jscrambler is best for client-side and payment page defense.
Do I need ADR if I already have a firewall?
Yes, for high-value applications. A firewall sees network traffic, while ADR sees what the application actually executes, catching attacks that look legitimate at the edge. Pair the two: the edge absorbs volumetric noise cheaply, and ADR judges requests that deserve code-level scrutiny.
How should I deploy ADR safely?
Start in monitor-only mode on one tier-one application, measure overhead and false-block rates against real traffic for a sprint, then graduate to blocking on routes where evidence supports it. Avoid global blocking on day one, which usually gets disabled fast after false positives.
Which languages do ADR tools support best?
Java and .NET have the broadest coverage. Node.js and Python support is common but less mature, and Go and Rust have limited options due to their compiled nature. Check each tool's documentation for current language support before buying.
Is there a free ADR tool?
OpenRASP by Baidu is the only free option, but it has been unmaintained since January 2022, so treat it as an evaluation tool rather than a production dependency. For actively maintained open-source runtime defense, ModSecurity covers a similar layer, though it is a firewall rather than true ADR.
Sources we checked (0)
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 Contrast Security
 Datadog ASM
 Waratek
 Fastly
 Jscrambler
 Oligo Security