How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- SonarQube is the safest default, pairing code quality gates with security scanning and a genuinely usable free self hosted tier.
- Snyk Code and Semgrep are the fastest developer friendly scanners, with Snyk fitting teams already in the Snyk ecosystem and Semgrep winning for custom rules.
- CodeRabbit adds AI pull request review on top of deterministic scanning, which suits teams merging large amounts of AI generated code.
- Checkmarx and Veracode are built for regulated enterprises with compliance deadlines, and expect five figure annual contracts and longer rollouts.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 SonarQube | Quality gates plus security in one platform | $30 per month | Yes |
 Snyk Code | Developer first security in Snyk ecosystem | $25 per developer/month | Yes |
 Semgrep | Custom security rules and fast scans | $30 per contributor/month | Yes |
 Codacy | Affordable all in one quality and security | $15 per user/month | Yes |
 DeepSource | Automated review with verified autofixes | $24 per user/month | Free trial |
 CodeRabbit | AI pull request review | $24 per user/month | Yes |
 Checkmarx | Enterprise AppSec with compliance needs | See website | No |
 Veracode | Audit ready security programs | See website | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
Starting price$30 per month
Free planYes
SonarQube is the default for teams that want code quality and security in one gate. Pull request analysis, quality gates and security rules run in CI, so bad code fails the build before merge. The Cloud free tier covers pull request analysis up to 50,000 lines on private projects and never expires, while Community Build is free and self hosted for main branch analysis.
The limits are tiering. Community Build cannot analyze pull requests, and advanced SAST, taint analysis for some languages and AI agents sit on higher tiers. Cloud Team starts around 30 to 34 dollars a month depending on lines of code, and server editions price per instance per year by code size. For a team that wants one rule based gate for quality and security, SonarQube is the safest pick.
What we like- Quality gates block bad merges in CI
- Free Community Build self hosted
- 30 plus languages with taint analysis on paid tiers
Watch out for- Community Build covers main branch only with no PR analysis
- Advanced SAST features sit on Enterprise
- Server editions price by lines of code
#2
Snyk Code
Best for: Developer first security in Snyk ecosystem
Visit snyk.io
Starting price$25 per developer/month
Free planYes
Snyk Code fits teams already using Snyk for open source dependencies, containers or infrastructure. Code findings sit beside dependency findings in one dashboard, scans run fast in the IDE and in pull requests, and fix guidance is written for developers rather than auditors. Team starts at 25 dollars per contributing developer per month, with 100 projects and 1,000 tests a month for up to 10 developers.
The free tier is small, with 5 projects and 100 Code tests a month, and the enterprise credit model, where one credit equals one dollar, needs careful budgeting at scale. For a team that wants code and dependency security from one vendor with minimal friction, Snyk Code is a strong pick.
What we like- Fast scans inside developer workflow
- Code and dependency findings from one vendor
- Strong IDE and Git integrations
Watch out for- Free tier limited to 5 projects and 100 tests a month
- Team capped at 10 developers and 100 projects
- Enterprise uses a credit model
#3Semgrep
Best for: Custom security rules and fast scans4.6/5 on
G2 (56 reviews, checked Oct 2026)
Visit semgrep.dev
Starting price$30 per contributor/month
Free planYes
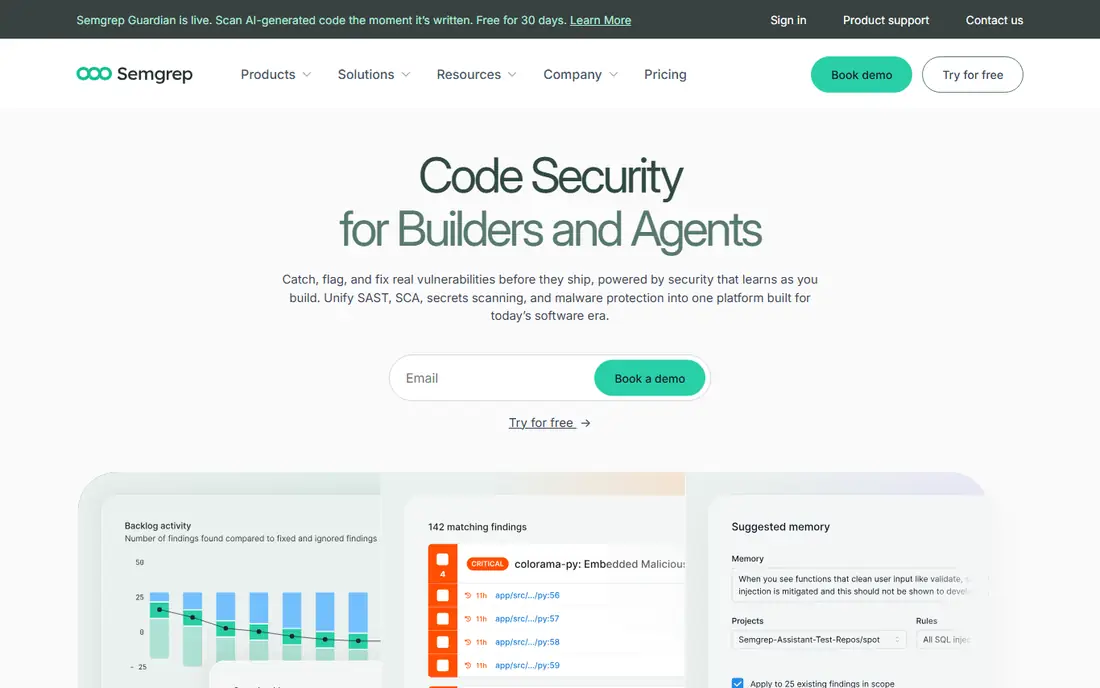
Semgrep wins when a team wants to write its own security rules. The open source engine scans in seconds, the registry carries OWASP mapped rule packs, and teams can write pattern rules for their own frameworks and APIs. The free tier covers 10 contributors, 10 private repos, cross file analysis and Pro rules, which is the strongest free offer in this category on raw capability.
The gaps are secrets detection, which the free tier excludes, and the skill needed to write good custom rules. Paid Code starts at 30 dollars per contributor per month in some comparisons, 35 dollars in others, so confirm the current price before budgeting. For a security minded team that wants control over detection logic, Semgrep is the best tool here.
What we like- Open source engine with custom pattern rules
- Fast scans in seconds
- Free tier covers 10 contributors and 10 private repos
Watch out for- Secrets detection excluded from free tier
- Contributor based pricing adds up
- Rule writing needs security skill
#4Codacy
Best for: Affordable all in one quality and security4.6/5 on
G2 (31 reviews, checked Oct 2026)
Visit codacy.com
Starting price$15 per user/month
Free planYes
Codacy is the budget all rounder, pairing code quality and security in one platform at 15 dollars per user per month on Pro in some comparisons, 18 dollars on Team in others. The free Developer tier covers open source fully and small private use, and Team covers 49 languages. Setup is fast, and automated review comments land directly in pull requests.
The caps matter: Team limits to 30 developers and 100 private repos, so larger teams must move to higher tiers. Analysis depth also trails SonarQube for complex codebases, and AI review features trail CodeRabbit. For a small team that wants quality plus security at the lowest paid price, Codacy is the value pick.
What we like- Cheapest paid tier among full platforms
- Free Developer tier
- 49 languages on Team
Watch out for- Team caps at 30 developers and 100 private repos
- AI features trail CodeRabbit
- Analysis depth trails SonarQube
#5DeepSource
Best for: Automated review with verified autofixes4.6/5 on
G2 (22 reviews, checked Oct 2026)
Visit deepsource.com
Starting price$24 per user/month
Free planFree trial
DeepSource focuses on automated code review that developers trust, with low false positives and autofixes verified before they are suggested. Team pricing sits around 24 to 30 dollars per user per month depending on source and billing, and AI review adds 8 dollars per 10,000 lines on Standard or 15 dollars on Advanced, with a 100 dollar annual AI credit per user. Public repos are free with a monthly PR review allowance.
Language coverage is narrower than SonarQube, and AI review costs scale with code size, so large codebases should model that line item. For a team that wants review comments it can act on without wading through noise, DeepSource is a strong pick.
What we like- Low false positives with verified autofixes
- AI review priced per lines of code
- Free for public repos
Watch out for- Team pricing varies by source
- AI review adds 8 to 15 dollars per 10,000 lines
- Language coverage is narrower than SonarQube
Starting price$24 per user/month
Free planYes
CodeRabbit is the AI layer for pull request review. It walks through each PR, links related issues and past PRs, and flags intent, logic and style problems that rule based scanners miss. That matters more as AI generated code fills pull requests, since generated code can look clean while missing the point. Essentials starts at 24 dollars per user per month billed annually, and open source repos are free.
CodeRabbit does not replace a deterministic scanner: it can miss a known vulnerability pattern that Semgrep or SonarQube would catch, and it can flag non issues. Team pricing at 48 dollars per user adds up. Pair CodeRabbit with a scanner like SonarQube or Semgrep, and use it for review quality, not as the only security gate.
What we like- AI walkthrough of every PR with linked issues
- Free for open source repos
- Catches intent and logic issues scanners miss
Watch out for- AI review complements, not replaces, deterministic scanners
- Team costs 48 dollars per user
- Usage and accuracy vary by codebase
#7Checkmarx
Best for: Enterprise AppSec with compliance needs4.2/5 on
G2 (49 reviews, checked Oct 2026)
Visit checkmarx.com
Starting priceSee website
Free planNo
Checkmarx is built for enterprise application security programs with compliance deadlines. It combines static analysis, dynamic testing and software composition analysis in one platform, with reporting that auditors accept. Large, complex codebases and regulated industries are its home ground.
The cost and pace are enterprise scale: pricing is quote only, with minimums around 40,000 dollars a year in independent comparisons, and scans run slower than developer first tools. Rollout takes months, not days. For a regulated enterprise that needs attestation grade reporting, Checkmarx earns its price. For a startup, it is overkill.
What we like- Deep SAST, DAST and SCA in one platform
- Strong compliance reporting
- Handles complex enterprise codebases
Watch out for- Quote only pricing with five figure minimums
- Slower scans than developer tools
- Rollout takes months
Starting priceSee website
Free planNo
Veracode suits security programs that must prove their work to auditors, customers or regulators. SAST and DAST coverage, policy gates and attestation reporting are the core strengths, with a long track record in regulated industries. Teams that must show a formal security program to win enterprise deals will find Veracode familiar to their customers.
Pricing is quote only, starting around 15,000 dollars a year for SAST alone in independent comparisons, with full programs reaching five figures and beyond. There is no free tier, and the developer experience feels heavier than Snyk or Semgrep. Choose Veracode when audit readiness is the buying reason, not when developer speed is.
What we like- Attestation and audit ready reporting
- SAST plus DAST coverage
- Long track record in regulated industries
Watch out for- Quote only pricing from about 15,000 dollars a year for SAST
- No free tier
- Developer experience trails newer tools
How we chose
We compared published pricing pages and independent pricing checks from October 2026, and we weighed free tier limits, per contributor prices, language coverage, scan speed, false positive handling, AI review quality and compliance reporting. We noted where prices conflict across sources, since vendors change tiers often, and we favored tools with a usable free tier for small teams. No tool was credited with hands-on testing, and no user counts, awards or ratings were invented for this guide.
What to check before you buy
Start with your merge workflow, not the feature list. A deterministic scanner like SonarQube or Semgrep belongs as a CI gate that blocks bad merges, while an AI reviewer like CodeRabbit belongs as a review assistant that improves code quality. Running both covers more than either alone, and the combination costs less than a single enterprise platform for most teams.
Next, count contributors honestly, since most tools here price per contributor or per developer, and the free tier caps are low: 10 contributors at Semgrep, 5 projects at Snyk, 30 developers at Codacy. Then test on your own code: run a trial scan on your largest repository and count false positives, since a noisy scanner gets ignored. Finally, check compliance needs early, since only Checkmarx and Veracode deliver audit ready attestation out of the box.
Frequently asked questions
Can free tiers handle real security scanning?
Yes, for small teams. Semgrep free covers 10 contributors and 10 private repos with cross file analysis, SonarQube Cloud free covers pull request analysis up to 50,000 lines, and Snyk free covers 5 projects. Larger teams, secrets detection and advanced taint analysis need paid tiers.
Do AI code review tools replace security scanners?
No. AI reviewers like CodeRabbit catch intent and logic issues, but they can miss known vulnerability patterns and can flag non issues. Deterministic scanners like Semgrep and SonarQube catch known patterns reliably. Use both: the scanner as the gate, the AI reviewer as the assistant.
Which tool is best for custom security rules?
Semgrep, by a wide margin. Its open source engine and pattern rule language let teams write rules for their own frameworks, and the registry offers OWASP mapped packs to start from. No other tool here matches that rule flexibility at a comparable price.
How much does enterprise AppSec really cost?
Checkmarx minimums run around 40,000 dollars a year and Veracode SAST from about 15,000 dollars a year in independent comparisons, with full programs reaching 50,000 to 200,000 dollars. Developer tools cost a fraction of that, but they do not deliver the same audit ready reporting.
Should AI generated code get extra review?
Yes. Generated code can look clean while missing business logic, mishandling edge cases or repeating insecure patterns. Pair a deterministic scanner gate with AI pull request review, and keep a human reviewer on security sensitive changes regardless of who wrote the code.
What is the cheapest path to code security?
Start with Semgrep free and SonarQube Cloud free together, which cover custom rules and quality gates at no cost for small teams. Add Codacy Pro at 15 dollars per user or Snyk Team at 25 dollars per developer when you outgrow the free caps.
Sources we checked (4)
- https://rankite.com/blog/best-static-code-analysis-software
- https://aicodereview.cc/blog/ai-code-review-security-vulnerabilities/
- https://aicodereview.cc/blog/best-static-analysis-tools-buyers-guide/
- https://dev.to/rahulxsingh/7-best-semgrep-alternatives-for-code-security-scanning-in-2026-21pi
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.