How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Vanta and Drata are the most recognized Secureframe replacements, with wide integrations and strong trust centers.
- Thoropass stands out by bundling software with its own audit firm, which simplifies the path to a signed report.
- Sprinto, Scytale, and Scrut suit teams that want guided help and broad framework coverage without enterprise pricing.
- Hyperproof and Strike Graph fit larger programs that manage many frameworks, risks, and audits together.
- Always budget the audit fee separately, since most platforms sell software only and the audit is a second contract.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Vanta | Widest recognition and integrations | See website | No |
 Drata | Continuous multi-framework monitoring | See website | No |
 Sprinto | Fast startup compliance | See website | No |
 Thoropass | Software plus audit in one vendor | See website | No |
 Scytale | Guided compliance with experts | See website | No |
 Scrut | AI-assisted compliance and risk | See website | No |
 Hyperproof | Enterprise GRC programs | See website | No |
 Strike Graph | Flexible AI-native compliance | See website | No |
 Apptega | Service providers and in-house teams | See website | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best Secureframe alternatives for SOC 2 and beyond
#1Vanta
Best for: Widest recognition and integrations4.5/5 on
G2 (2,742 reviews, checked Oct 2026)
Visit vanta.com
Starting priceSee website
Free planNo
Vanta is the safest choice when enterprise buyers ask what tool you use. Its name is widely recognized in security reviews, and its integration library covers cloud, identity, HR, ticketing, and code tools that auditors expect to see connected. Continuous monitoring flags control gaps as they appear, and the trust center lets prospects check your posture without repeated document requests. Questionnaire automation also cuts the time sales teams spend answering security reviews.
The main drawback is cost structure. The platform price is only part of the bill, since trust center features, questionnaire automation, and extra frameworks can add up, and the SOC 2 audit itself is a separate engagement with an outside firm. Teams should request a full quote that lists every module they need. For companies selling to large enterprises, Vanta's recognition often justifies that total.
What we like- Very large integration library
- Strong trust center and questionnaire automation
- Broad framework coverage
Watch out for- Pricing is quote-based and total cost grows with add-ons
- Audit fee is separate
#2Drata
Best for: Continuous multi-framework monitoring4.7/5 on
G2 (1,392 reviews, checked Oct 2026)
Visit drata.com
Starting priceSee website
Free planNo
Drata maps controls once and reuses them across SOC 2, ISO 27001, HIPAA, GDPR, and other frameworks, which saves work when a company adds a second standard. Evidence collection runs continuously from connected systems, so teams see control health in real time rather than scrambling before an audit. The trust center and AI-assisted questionnaire responses help sales teams answer security questions faster and with consistent language.
Drata is built for growth, and its pricing reflects that. Small startups may find the quote higher than leaner tools such as Sprinto or Scytale, especially once trust center and risk features are added. If you plan to hold several frameworks and want one governed system for controls, risks, and evidence, Drata is a strong Secureframe replacement.
What we like- Continuous control monitoring
- Control mapping across frameworks
- Strong trust center
Watch out for- Quote-based pricing
- Smaller teams may pay for enterprise depth they do not use
#3Sprinto
Best for: Fast startup compliance4.7/5 on
G2 (1,685 reviews, checked Oct 2026)
Visit sprinto.com
Starting priceSee website
Free planNo
Sprinto is designed for startups that need SOC 2 or ISO 27001 quickly and without a dedicated compliance hire. It connects to cloud, identity, HR, and development tools, monitors controls continuously, and guides teams through policies, evidence, and remediation tasks. Its framework library is large, which helps companies that operate across regions or serve regulated customers. Vendor risk management and a trust center are included in the wider platform.
Sprinto's speed is its main selling point, but buyers should still confirm what the quote covers. Framework count, employee count, and add-on modules all affect price, and the audit remains a separate cost. For a small team that wants structure and momentum toward a first audit, Sprinto gives clearer guidance than a bare platform.
What we like- Broad framework library
- Guided setup for first-time teams
- Continuous monitoring and vendor risk
Watch out for- Pricing varies by headcount and frameworks, so quotes differ widely
- Audit fee is separate
#4Thoropass
Best for: Software plus audit in one vendor4.7/5 on
G2 (585 reviews, checked Oct 2026)
Visit thoropass.com
Starting priceSee website
Free planNo
Thoropass differs from most tools here because it pairs software with its own audit and assurance team. Evidence, tasks, and auditor requests live in one place, so teams do not manage a platform in one system and an auditor in another. That setup shortens the back-and-forth that often delays a first SOC 2 report, and it suits teams without prior audit experience. Thoropass also covers HIPAA, HITRUST, ISO 27001, PCI, and GDPR, which matters for healthcare and fintech companies.
The trade-off is auditor independence and choice. Some companies prefer to pick their own auditor, and Thoropass's bundled model does not suit that preference. Pricing is also quote-based, so compare its combined software-plus-audit price against a platform quote plus a separate audit quote. For teams that want one vendor to carry them to a signed report, Thoropass is the clearest option.
What we like- In-house auditors in the same platform
- Task-based audit workflow
- Strong healthcare and fintech fit
Watch out for- Using its audit firm limits auditor choice
- Pricing is quote-based
Starting priceSee website
Free planNo
Scytale combines automation with human experts who guide a team from kickoff through audit and renewal. That guidance helps companies that lack a compliance lead, since experts help scope controls, prepare evidence, and respond to auditor questions. The platform supports many security, privacy, and AI frameworks, with control mapping that reduces duplicate work when adding a standard. A trust center lets customers view compliance status without repeated requests.
Scytale's price depends on frameworks, headcount, and whether audit or penetration testing support is bundled, so request a detailed quote. Teams that want software only may find Scytale more hands-on than needed, while teams that want a guide will value the expert layer. It is a good middle ground between a self-serve platform and a full consulting engagement.
What we like- Dedicated compliance experts
- Broad framework support
- Trust center included
Watch out for- Audit and penetration testing may be add-ons
- Pricing is quote-based
#6Scrut
Best for: AI-assisted compliance and risk4.9/5 on
Capterra (139 reviews, checked Oct 2026)
Visit scrut.io
Starting priceSee website
Free planNo
Scrut covers compliance, risk, and trust in one platform, with AI assistants that draft policies, collect evidence, detect gaps, and answer security questionnaires. Its risk register connects cloud, access, policy, and vendor signals, so a failed control shows up as a prioritized risk rather than an isolated alert. Integrations cover common cloud, identity, and development tools, and the trust center keeps customer-facing proof current.
AI output still needs human review, especially for policy language and questionnaire answers that customers rely on. Scrut's pricing is quote-based, so compare the full platform cost against Vanta and Drata at the same framework count. For teams that want compliance and risk management together, with AI help on routine work, Scrut is a strong fit.
What we like- AI assistants for policies, evidence, and questionnaires
- Risk register and vendor risk in one place
- Broad integrations
Watch out for- Newer AI features need review before relying on outputs
- Pricing is quote-based
#7Hyperproof
Best for: Enterprise GRC programs4.5/5 on
G2 (223 reviews, checked Oct 2026)
Visit hyperproof.io
Starting priceSee website
Free planNo
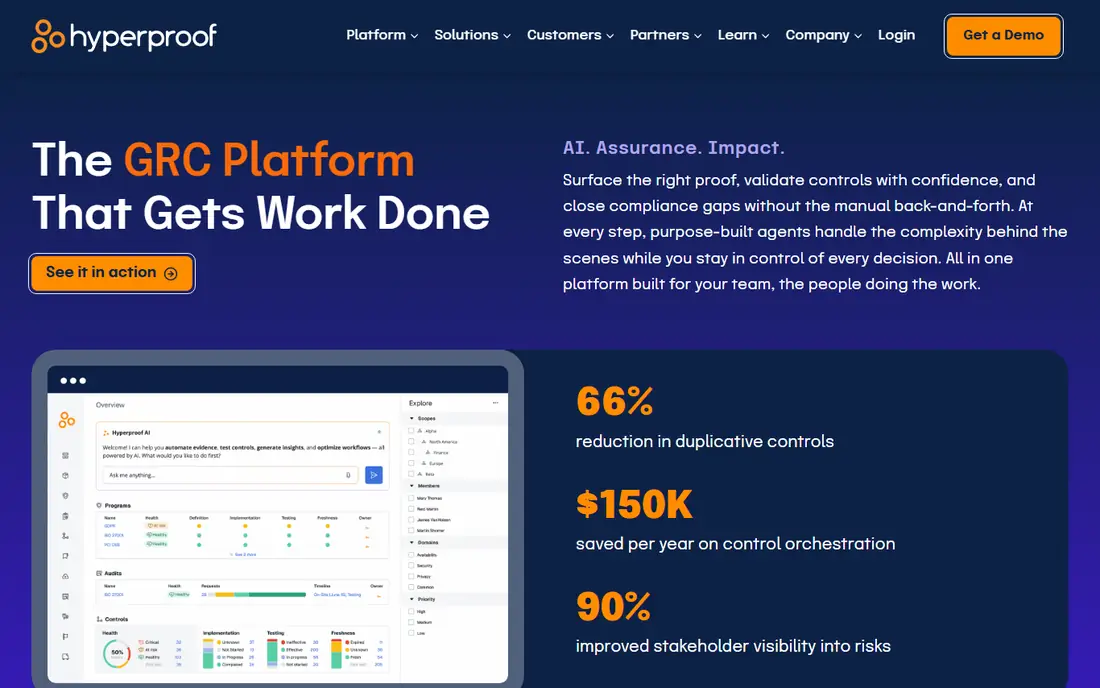
Hyperproof is a governance, risk, and compliance platform that manages compliance, risk, audit, and trust together. Its common control approach maps one control to many frameworks, which cuts duplicate work for companies that run SOC 2, ISO 27001, and internal audit programs at once. Auditors can collaborate in the platform, evidence links to requests, and risk data feeds into the same system. A government-focused version serves high-security organizations.
Hyperproof suits mid-market and enterprise teams more than early startups. Pricing is quote-based, and implementation takes more planning than a startup-focused tool. If your program spans several frameworks, business units, and audit types, Hyperproof gives the structure that simpler tools lack.
What we like- Large framework library
- Common control set across programs
- Audit collaboration and risk management
Watch out for- Enterprise focus and pricing
- Smaller teams may find it heavier than needed
#8Strike Graph
Best for: Flexible AI-native compliance4.6/5 on
G2 (197 reviews, checked Oct 2026)
Visit strikegraph.com
Starting priceSee website
Free planNo
Strike Graph lets teams design a security program around their actual business rather than forcing a fixed template. Controls, evidence, and frameworks can be tailored, which helps companies with unusual products or regulatory mixes. AI-assisted setup connects systems and collects evidence, and real-time tracking shows readiness across frameworks. That flexibility suits teams that outgrew a rigid checklist tool but do not need a full enterprise GRC suite.
Brand recognition is lower than Vanta or Drata, so enterprise buyers may ask more questions during security reviews, though a trust center and audit report still carry the weight. Pricing is quote-based, so compare it at your framework and headcount level. For teams that value adaptability, Strike Graph is a practical Secureframe alternative.
What we like- Flexible control design for unique programs
- AI-assisted evidence collection
- Clear audit readiness tracking
Watch out for- Smaller brand recognition than Vanta or Drata
- Pricing is quote-based
Starting priceSee website
Free planNo
Apptega serves managed security providers and in-house teams that run compliance programs for several clients or business units. It supports many frameworks, maps controls across them, and tracks assessments, risks, and remediation in one place. Providers can manage multiple clients from one account, which makes it useful for firms that sell compliance as a service. In-house teams get structured guidance for each control, which helps non-specialists run a program.
Apptega's automation is less deep than Vanta or Drata for very large cloud environments, where continuous evidence collection matters most. Pricing is quote-based, though its positioning is generally more affordable than enterprise GRC platforms. For providers and small teams that need solid structure without enterprise cost, Apptega is worth a quote.
What we like- Framework cross-mapping
- Affordable positioning for providers
- Multi-client program management
Watch out for- Automation depth trails Vanta and Drata for large cloud estates
- Best known for provider use
How we chose
We compared vendor pricing pages, documentation, and public reviews on G2, Capterra, and Reddit, and we checked each vendor homepage to confirm the product still exists and accepts new customers. We favored tools that automate SOC 2, ISO 27001, or HIPAA work, meaning evidence collection, control monitoring, and audit preparation, over generic project tools. We also weighed framework coverage, audit support, expert guidance, and fit for startups versus enterprises, and we replaced any tool whose homepage belonged to a different product.
Choosing the right Secureframe alternative
Separate the platform price from the audit price
Most vendors sell software only, so the audit fee, penetration test, and readiness help are extra. Ask each vendor for a written total that includes the platform, each framework, the trust center, questionnaire automation, and the audit. Thoropass is the exception here, since it bundles audit services, so compare its combined price against the split total from other vendors.
Pick the level of help you actually need
A team with a security lead may only need automation and monitoring, which points to Vanta, Drata, or Scrut. A team without compliance experience benefits from guided help, which points to Sprinto, Scytale, or Thoropass. Paying for expert guidance you do not need wastes budget, while skipping it when you need it delays the audit.
Confirm your integrations before you sign
List your cloud provider, identity tool, HR system, code host, and ticketing tool, then check each one against the vendor integration list. A missing connector means manual evidence uploads, which erodes the automation value. Also confirm how often evidence refreshes, since stale evidence creates audit findings.
Frequently asked questions
What is the cheapest Secureframe alternative?
Pricing in this market is mostly quote-based, so there is no single cheapest tool for every company. Sprinto, Scytale, and Scrut often quote lower than Vanta and Drata for small teams, while Thoropass bundles the audit fee. Request quotes at the same headcount and framework count to compare fairly.
Does any alternative include the SOC 2 audit?
Thoropass bundles software with audit services from its own assurance team. Most other tools connect you with partner auditors or let you bring your own, and the audit fee is separate. Always ask whether a quote includes the audit, since that single line can change the total by thousands of dollars.
How long does SOC 2 take with these tools?
A first SOC 2 Type 1 audit often takes a few months from kickoff, including control setup, evidence collection, and auditor review. Type 2 adds an observation period, typically several months, during which controls must operate. Tools speed up evidence work, but they cannot shorten the observation period an auditor requires.
Can I migrate from Secureframe to another tool?
Yes, in most cases. You can export policies, controls, and evidence from Secureframe and rebuild them in the new platform, though control mapping and integration setup still take time. Ask the new vendor about migration help, and plan the switch between audit cycles when possible to avoid disrupting an active audit.
Which alternative is best for a startup?
Sprinto and Scytale suit startups that want guided help toward a first audit, while Vanta suits startups selling to large enterprises that recognize the brand. Thoropass suits startups that want software and audit from one vendor. The right pick depends on budget, buyer expectations, and whether you have compliance experience in-house.
Do these tools cover HIPAA and ISO 27001 too?
Yes, all nine tools in this list support multiple frameworks, including SOC 2, ISO 27001, and HIPAA in most cases. Framework coverage still varies, so confirm your exact standards, including GDPR, PCI DSS, or HITRUST, before signing. Control mapping across frameworks is where these tools save the most time.
Sources we checked (9)
- https://www.vanta.com/pricing
- https://drata.com/pricing
- https://www.sprinto.com/pricing
- https://thoropass.com/pricing
- https://www.scytale.ai/pricing
- https://www.scrut.io/pricing
- https://hyperproof.io/pricing
- https://www.strikegraph.com/pricing
- https://www.apptega.com/pricing
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.