How we make this list: we compare pricing pages, product documentation and public user reviews. Rankite is independent; if a vendor ever pays for a featured spot, that listing is clearly labeled Partner.
Key takeaways
- If you handle card numbers directly, the biggest win is keeping card data out of your environment entirely. Very Good Security vaults the data so your PCI scope collapses.
- For the compliance process itself, Drata, Vanta and Secureframe automate evidence collection and continuous control monitoring across frameworks including PCI DSS.
- Sprinto and Scrut Automation aim at smaller teams that need PCI DSS without an enterprise compliance department.
- Data-security tools like Netwrix and Varonis help with the technical side: who touches cardholder data, where it lives, and whether access is appropriate.
- Almost none of these vendors publish pricing. Budget for annual contracts and get the scope of frameworks included in writing before you sign.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Drata | companies automating evidence collection across frameworks | See website | No |
 Vanta | getting audit-ready quickly with guided setup | See website | No |
 Secureframe | startups that want compliance experts on call | See website | No |
 Sprinto | smaller teams that need compliance automation without enterprise overhead | See website | No |
 Scrut Automation | cloud-native teams that want compliance plus risk management in one place | See website | No |
 Very Good Security | fintech and SaaS companies that want card data out of their systems | $1,000/month (Starter) | No |
 Netwrix | auditing who accesses cardholder data across your environment | See website | No |
 Varonis | enterprises governing data access at scale | See website | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
The best PCI compliance software
#1
Drata
Best for: companies automating evidence collection across frameworks
Visit drata.com
Starting priceSee website
Free planNo
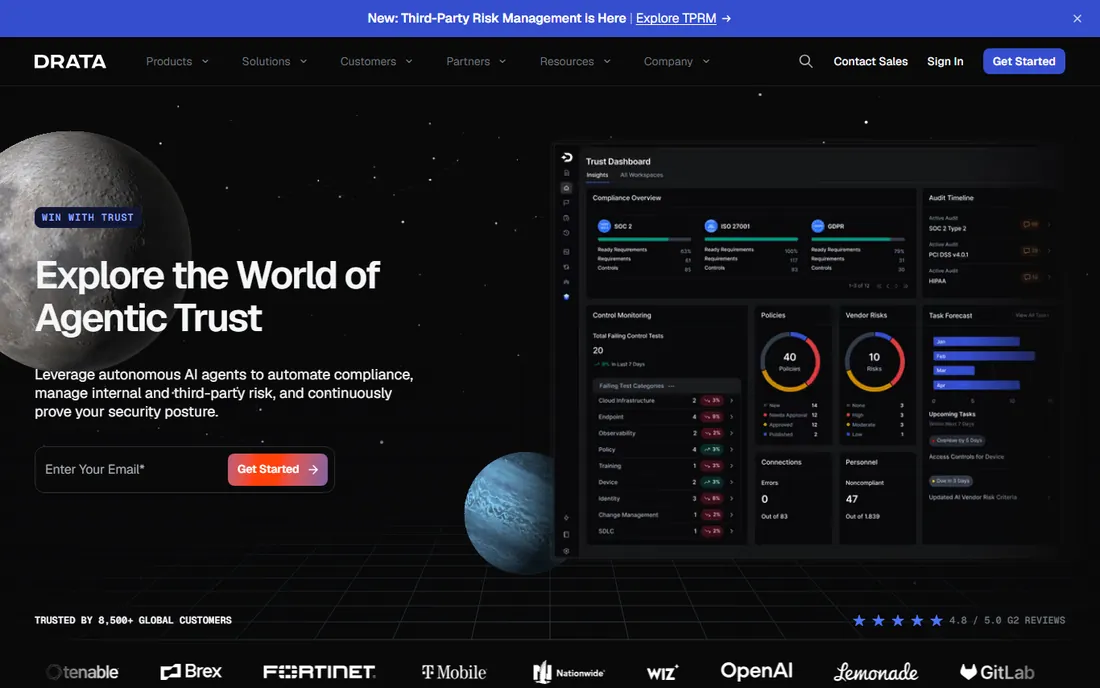
Drata's whole pitch is replacing the pre-audit scramble. It connects to your cloud accounts, HR systems and security tools, then continuously monitors controls and collects the evidence auditors ask for. PCI DSS sits alongside SOC 2, ISO 27001, HIPAA and GDPR in the same control set, which matters if your customers demand multiple certifications.
Pricing is deliberately not published. Drata sells Foundation, Advanced and Enterprise plans through sales, and observed contracts run from roughly $10,000 a year upward depending on company size and framework count. There is no free tier and no trial. Buy it when the cost of manual audit prep exceeds the contract, which for most growing SaaS companies happens fast.
What we like- Continuous control monitoring
- Broad framework library including PCI DSS
- Strong integrations
Watch out for- Quote-only pricing
- Annual contracts
- More platform than a tiny shop needs
#2
Vanta
Best for: getting audit-ready quickly with guided setup
Visit vanta.com
Starting priceSee website
Free planNo
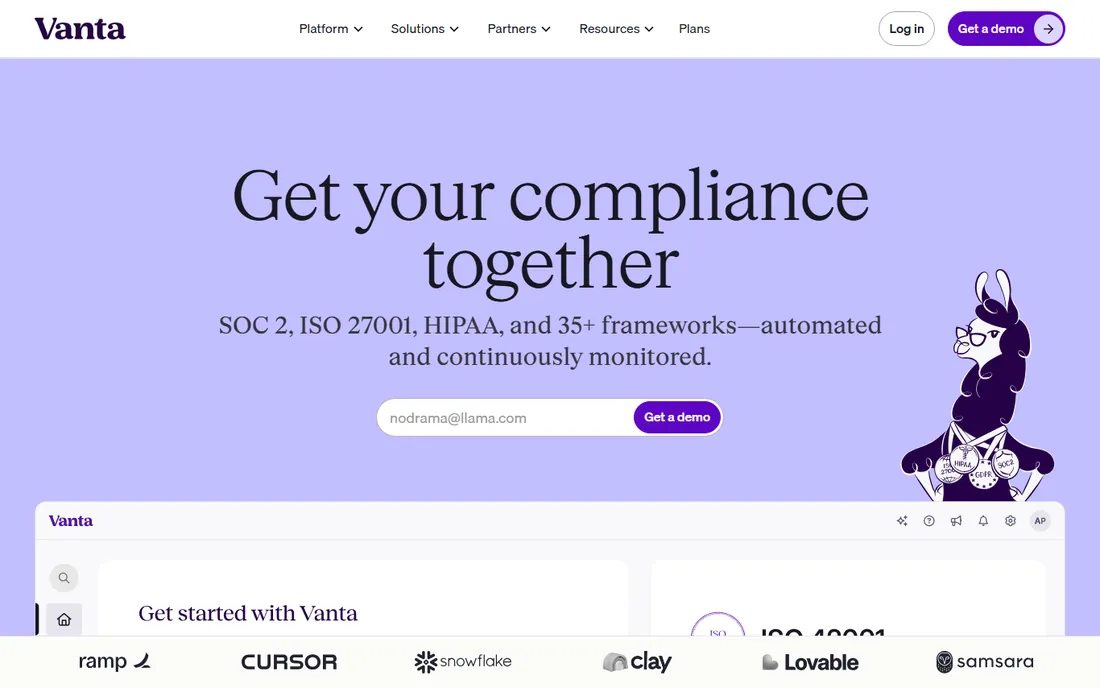
Vanta competes directly with Drata for the compliance-automation crown, and the honest difference is emphasis: Vanta pushes hardest on time-to-first-audit. Its guided setup walks a small team through scoping, evidence collection and remediation in weeks rather than quarters, and its auditor network connects you with firms that already know the platform.
Like Drata, pricing is quote-based with no published numbers and no free plan. For a startup that needs PCI DSS because an enterprise customer put it in the contract, Vanta's speed story is compelling. For a company that already runs a mature security program, compare its automation depth against Drata before deciding.
What we like- Guided onboarding that moves fast
- Large auditor network
- Good for first-time certification
Watch out for- Pricing behind sales
- Automation depth varies by framework
Starting priceSee website
Free planNo
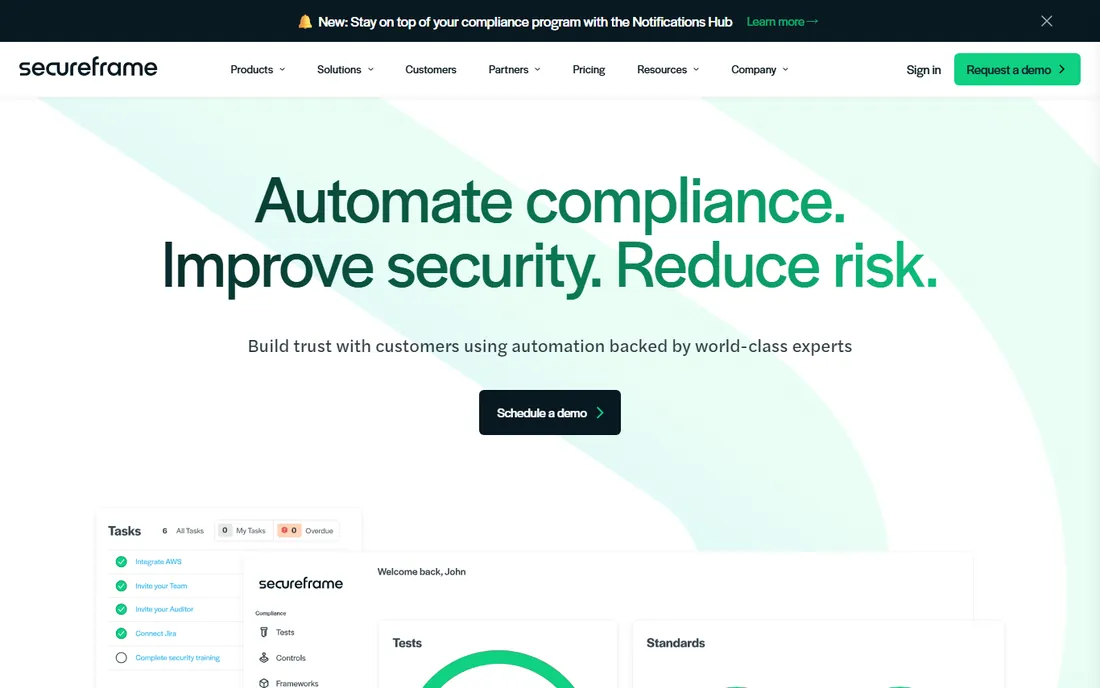
Secureframe leans into the service layer. Alongside automated control monitoring, it offers readymade policy templates and access to compliance experts who can guide a team through its first PCI DSS assessment. That hand-holding is the differentiator for companies without a dedicated security hire.
The platform covers the standard frameworks and continuous monitoring, but the integration catalog is narrower than Drata's or Vanta's. Pricing is not published. Choose Secureframe when the buyer is a founder or ops lead rather than a security engineer, because that is who the product is built for.
What we like- Strong onboarding support
- Readymade policies
- Auditor marketplace
Watch out for- Quote-only pricing
- Smaller integration catalog than the leaders
#4
Sprinto
Best for: smaller teams that need compliance automation without enterprise overhead
Visit sprinto.com
Starting priceSee website
Free planNo
Sprinto targets the part of the market the big platforms price out: companies with dozens of employees rather than hundreds. It automates control monitoring and evidence collection for PCI DSS, SOC 2, ISO 27001 and others, with a setup process designed to be measured in days.
The tradeoff for the smaller-company focus is depth. Complex multi-entity environments and heavily regulated industries may outgrow it. Pricing is not published, but the positioning is clear: if Drata feels like too much platform for your team, Sprinto is worth a demo.
What we like- Positioned for SMB budgets
- Quick setup
- Covers PCI DSS plus common frameworks
Watch out for- Less depth for complex enterprise environments
- Pricing not public
#5
Scrut Automation
Best for: cloud-native teams that want compliance plus risk management in one place
Visit scrut.io
Starting priceSee website
Free planNo
Scrut Automation bundles compliance automation with continuous risk management, which is a sensible combination for PCI DSS: the standard is as much about ongoing risk practices as it is about passing an annual assessment. The platform monitors controls, manages evidence and tracks risk in one place.
Brand recognition lags the US incumbents, and pricing requires a sales conversation. For mid-market teams that want one tool covering both compliance and risk without paying enterprise-platform prices, Scrut deserves a look.
What we like- Combines compliance automation with risk management
- Cloud-native design
- Competitive for mid-market
Watch out for- Smaller brand recognition
- Quote-based pricing
Starting price$1,000/month (Starter)
Free planNo
VGS attacks PCI compliance from a different angle: instead of proving your systems handle card data safely, you stop handling card data at all. Card numbers go into VGS's vault, and your systems work with tokens. That collapses PCI scope, because the cardholder data environment is no longer yours.
The Starter plan begins at $1,000 a month, with Growth packages on custom pricing that add network tokens, account updater and compliance support. For a small startup with tiny card volume, a processor-hosted payment form achieves similar scope reduction for less. For a growing fintech using multiple processors, VGS's orchestration features justify the spend.
What we like- Tokenization shrinks PCI scope dramatically
- Network tokens and account updater
- Works with Stripe
Watch out for- Meaningful cost for small card volumes
- Procurement review is thorough
#7
Netwrix
Best for: auditing who accesses cardholder data across your environment
Visit netwrix.com
Starting priceSee website
Free planNo
PCI DSS Requirement 10 is all about logging and monitoring who touches cardholder data, and that is Netwrix's home turf. It tracks access to sensitive data across file servers, databases and Active Directory, producing the audit trails and alerts that assessors ask for. It also monitors configuration changes that could weaken the cardholder data environment.
This is a technical tool for IT and security teams, not a compliance-management platform. Expect quote-based pricing and an enterprise sales process. Pair it with a compliance automation platform if you also need the policy and evidence-management side.
What we like- Detailed access auditing for PCI requirements
- Change tracking
- Broad platform coverage
Watch out for- Quote-only pricing
- Interface reflects its enterprise roots
Starting priceSee website
Free planNo
Varonis starts from a different question: where is your sensitive data, who can reach it, and should they be able to? It discovers and classifies data across cloud and on-prem systems, then enforces least-privilege access and flags abnormal behavior. For PCI DSS, that maps directly to protecting stored cardholder data and restricting access by business need-to-know.
It is enterprise software in price and complexity, built for organizations with sprawling data estates. A small e-commerce shop does not need Varonis. A large retailer or processor with cardholder data across dozens of systems does.
What we like- Automatic data discovery and classification
- Least-privilege enforcement
- Insider threat detection
Watch out for- Enterprise pricing and complexity
- Overkill for small card environments
How to scope PCI DSS before buying software
First, determine your PCI scope, because it decides which tools matter. If card data never touches your systems (processor-hosted checkout, tokenization), your compliance burden is a short self-assessment questionnaire and your tooling needs are minimal. If you store, process or transmit cardholder data, the full standard applies and the tooling bill grows.
Second, separate the two jobs. Compliance automation platforms (Drata, Vanta, Secureframe, Sprinto, Scrut) manage the process: policies, evidence, control monitoring, audit prep. Data-security tools (Netwrix, Varonis) and vaulting (VGS) address the technical requirements: access control, logging, encryption, scope reduction. Most companies need one of each, not two of one kind.
Third, count the frameworks. If you need SOC 2 and PCI DSS, buy a platform that covers both in one control set rather than two point tools. The overlap in evidence collection is large, and a single platform avoids duplicating work.
Fourth, get framework scope in writing. Quote-based pricing means the proposal defines what you bought. Confirm which frameworks, how many employees or systems are covered, and what the auditor relationship costs before you sign the annual contract.
How we chose
We selected tools that exist today and address real PCI DSS jobs: compliance automation, card data vaulting, access auditing and data governance. Pricing facts come from vendor pages and documentation checked in October 2026, including VGS's published Starter pricing and Drata's published plan structure. Vendors that do not publish pricing are listed as See website, and we did not invent numbers. Confirm live pricing with each vendor before buying.
The scope-reduction playbook
The cheapest PCI compliance program is the one you do not need. Every system that touches card data expands your assessment scope, so the first move is always to remove systems from scope: use a processor-hosted payment page, tokenize stored cards with a vault like VGS, and segment networks so the cardholder data environment is as small as possible.
Only then does tooling enter the picture. With a small scope, a compliance automation platform plus basic logging may be enough. With a large scope, you will need access auditing, file integrity monitoring and possibly a dedicated data-security platform. Buy in that order, and re-scope annually, because scope creeps back every time an engineer adds a new integration.
Frequently asked questions
What is PCI compliance software?
Software that helps organizations meet the Payment Card Industry Data Security Standard. It includes compliance automation platforms that manage evidence and controls, vaulting tools that remove card data from your systems, and data-security tools that audit access to cardholder data.
Do small businesses need PCI compliance software?
It depends on scope. A small shop using a processor-hosted checkout has minimal scope and may only need the self-assessment questionnaire. A business that stores or processes card numbers needs real tooling for logging, access control and evidence management.
How much does PCI compliance software cost?
Compliance automation platforms are quote-based, with observed contracts starting around $10,000 a year. VGS publishes a Starter plan at $1,000 a month. Expect annual contracts and get framework coverage in writing.
What is the fastest way to reduce PCI scope?
Stop touching card data. Use processor-hosted payment forms and tokenize stored cards with a vault provider. Every system removed from the cardholder data environment shrinks the assessment.
Can compliance automation replace a PCI assessor?
No. Tools like Drata and Vanta automate evidence collection and control monitoring, which makes assessments faster and cheaper, but the assessment itself still requires a qualified assessor or the appropriate self-assessment questionnaire.
Which frameworks do these tools cover besides PCI DSS?
Most compliance automation platforms cover SOC 2, ISO 27001, HIPAA, GDPR and others in the same control set. Data-security tools like Netwrix and Varonis support PCI DSS alongside GDPR, HIPAA and SOX. Confirm your specific frameworks are included before buying.
Sources we checked (7)
- https://www.lepide.com/blog/top-10-pci-compliance-audit-and-reporting-tools/
- https://walletinvestor.com/news/finance-news/pci-compliance-vaulting-apis-6-fintech-picks-for-2026/
- https://soc2auditors.org/insights/drata-pricing/
- https://www.spotsaas.com/compare/drata-vs-trustero
- https://www.cyera.com/blog/best-data-security-solutions-and-how-to-choose-the-right-one
- https://SourceForge.net/software/pci-compliance/
- https://www.getapp.com/security-software/pci-compliance/f/access-control/
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has spent more than a decade helping SaaS and e-commerce brands grow through search. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.