How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
What is the best NIS2 compliance software for startups?
Cyberday is the best NIS2 compliance software for most startups, because it names NIS2 as a supported framework, turns the work into prioritised tasks inside Microsoft Teams, and publishes a starting price of 267 euros a month for teams under 20 people. Secureframe is the best alternative, with automated evidence collection from 7,500 dollars a year.
Key takeaways
- Cyberday leads for startups, with NIS2 task lists, a 14-day trial and a published price from 267 euros a month.
- Secureframe is the only other tool here with a published starting price, at 7,500 dollars a year for one framework.
- Drata, Vanta, OneTrust and LogicGate publish no prices, so get a written quote first.
- NIS2 applies to entities in scope by sector and size, so check scope before you buy.
- No tool files your incident report or registers you, so plan for that work too.
Does NIS2 apply to a small startup?
NIS2 applies to a startup only when it falls inside the sectors and size bands the directive sets, so many small startups outside those sectors face no direct NIS2 duty. NIS2 is EU Directive 2022/2555, and it covers essential and important entities in the Annex I and II sectors, which include energy, transport, banking, health, digital infrastructure, ICT services and manufacturing. The size rule generally catches medium-sized and larger entities, meaning 50 or more employees or turnover above 10 million euros. Member states may also name smaller entities with a key role, so a small supplier can still be pulled in.
Even a startup outside scope can feel NIS2 through its customers. An in-scope customer must manage supply chain security under Article 21, and that duty often reaches the startup as a contract term or a security questionnaire. Transposition timing varies by member state, so check the law in each country where you operate. Fines reach 10 million euros or 2 percent of worldwide turnover for essential entities, and 7 million euros or 1.4 percent for important entities. This guide gives general information, not legal advice, so confirm your position with counsel.
What does NIS2 actually require a startup to do?
NIS2 requires in-scope entities to run risk management measures, report significant incidents, secure their supply chains, and keep their management body accountable. Article 21 lists ten risk management measures, covering risk analysis, incident handling, business continuity, supply chain security, system acquisition and development, testing measures, cyber hygiene and training, cryptography, human resources security, access control, and multi-factor authentication.
Incident reporting runs on fixed clocks. A significant incident needs an early warning within 24 hours, a notification within 72 hours, and a final report within one month. The management body must approve the measures, oversee them, and can be held liable, and its members must follow training. Entities must also register with their competent authority. Software helps with the documented half: policies, controls, evidence, risk records and supplier reviews. It does not replace the legal duties, and no tool here files a report or completes a registration for you.
How should a startup choose NIS2 compliance software?
A startup should choose NIS2 software by checking that NIS2 is a named framework, that setup takes days rather than months, and that the price is published or quoted in writing. A tool that names NIS2, with controls mapped to Article 21, saves weeks of manual mapping. A tool that only covers SOC 2 and ISO 27001 can still help, because those controls overlap with NIS2, but the team must do the mapping itself.
Next, test how the work reaches the team. A task-based tool that assigns small jobs to named people fits a startup with no compliance hire, while an evidence automation platform fits a team whose cloud tools can feed it data. Check the integrations against the stack the startup already runs, and whether incident tracking and supplier reviews sit inside the same product. Ask for a trial using one real NIS2 requirement, and ask how long a team of your size takes to reach a first gap report. Finally, check hosting and language, since EU data hosting matters for some customers. Avoid an enterprise suite that needs a consultant to configure it, because a six-month rollout defeats the point for a small team.
What does NIS2 compliance software cost in 2026?
NIS2 compliance software for a startup costs from about 3,200 euros a year at the cheapest published price to more than 20,000 dollars a year for quote-only platforms, before audit and staff time. The two published prices in this guide are Cyberday at 267 euros a month billed annually, or 3,200 euros a year, for teams under 20 people, and Secureframe Fundamentals from 7,500 dollars a year for one framework.
The other six tools publish no prices. Third-party data fills the gap with reported medians: about 20,000 dollars a year for Vanta, about 25,000 for Drata, about 12,000 for OneTrust, and about 54,000 for LogicGate. A 15-person startup pays 3,200 euros a year on Cyberday, or 7,500 dollars a year on Secureframe, while a quote-only platform could cost three to six times the Cyberday figure. Add auditor fees, penetration testing and staff time outside the licence. Some vendors discount multi-year deals by 15 to 25 percent, and renewal rises of 10 to 25 percent are common, so get the second-year price in writing.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Cyberday | Startups that want NIS2 as a named framework with step-by-step tasks and a published price | €267/month, billed annually (€3,200/year), for teams under 20 employees, vendor pricing page checked 12 Nov 2026 | No free plan; 14-day free trial, all features, no credit card required |
 Secureframe | Startups that want automated evidence collection with a published starting price | $7,500/year, Fundamentals plan, vendor pricing page checked 12 Nov 2026 | No free plan; demo on request |
 Drata | Growing startups that want continuous control monitoring across many frameworks | quote | No free plan; demo on request |
 Vanta | Startups that want a widely used compliance platform with a large integration library | quote | No free plan; demo on request |
 Scrut | Startups that want SOC 2 first with NIS2 and other frameworks added later | $15,000/year, AWS Marketplace listing for up to 20 employees, third-party reported, vendor pricing page returns 404 | No free plan; demo on request |
 6clicks | Startups that want a full GRC platform with risk, audit and vendor management in one place | quote | No free plan; free trial available |
 OneTrust | Startups that also need privacy, consent and AI governance beside NIS2 | quote | No free plan; no public free trial, demo on request |
 LogicGate | Startups that want to build custom risk and compliance workflows without code | quote | No free plan; demo on request |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
| Tool |
Best for |
Starting price |
Free plan |
| Cyberday |
NIS2 task lists for small teams |
€267/month, billed annually (€3,200/year), under 20 employees |
No free plan; 14-day free trial |
| Secureframe |
Automated evidence collection |
$7,500/year, Fundamentals |
No free plan; demo on request |
| Drata |
Continuous monitoring across frameworks |
quote |
No free plan; demo on request |
| Vanta |
Widely used platform, large integrations |
quote |
No free plan; demo on request |
| Scrut |
SOC 2 first, NIS2 added later |
$15,000/year, AWS Marketplace, up to 20 employees |
No free plan; demo on request |
| 6clicks |
Full GRC with risk and audit |
quote |
No free plan; free trial available |
| OneTrust |
Privacy and NIS2 in one platform |
quote |
No free plan; demo on request |
| LogicGate |
Custom no-code GRC workflows |
quote |
No free plan; demo on request |
#1
Cyberday
Best for: Startups that want NIS2 as a named framework with step-by-step tasks and a published price
Visit cyberday.ai
Starting price€267/month, billed annually (€3,200/year), for teams under 20 employees, vendor pricing page checked 12 Nov 2026
Free planNo free plan; 14-day free trial, all features, no credit card required
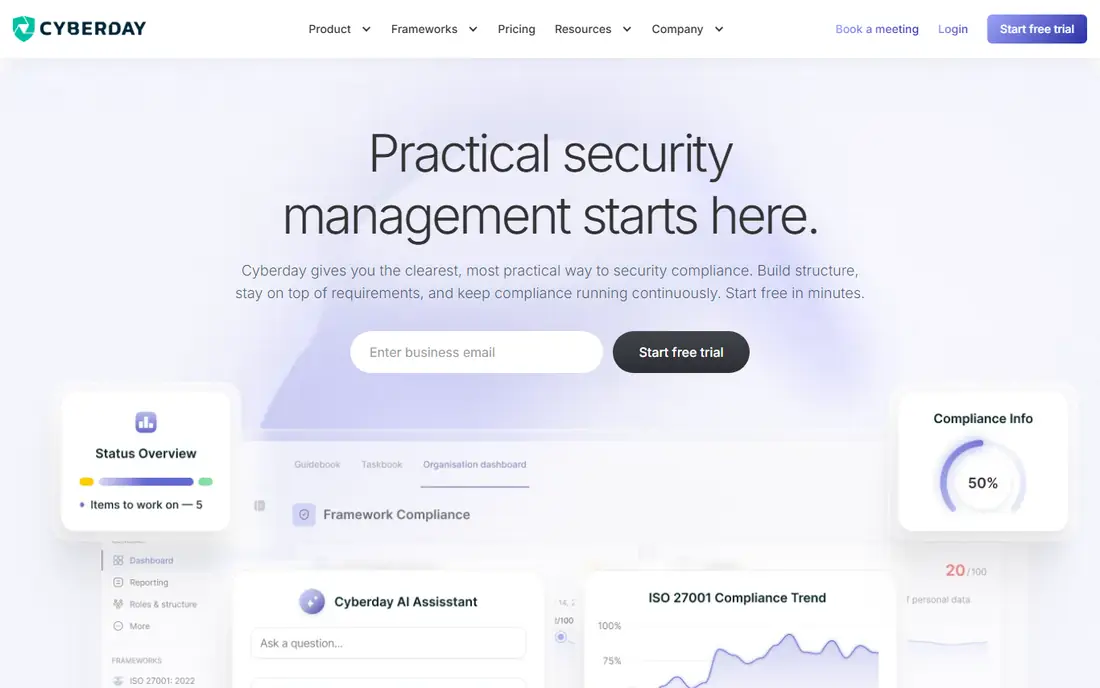
Cyberday splits NIS2, ISO 27001, DORA and other frameworks into prioritised tasks inside Microsoft Teams or Slack. Each requirement becomes a task with an owner, a due date and a way to prove it was done, which fits a small team with no compliance hire. Pricing is by headcount, not per user, so the whole team can take part without seat fees. The vendor pricing page checked 12 Nov 2026 lists 267 euros a month billed annually for under 20 employees.
What we like- NIS2 named framework, task-based guidance inside Microsoft Teams, published prices by headcount, unlimited users, AI assistant for policy writing
Watch out for- The Teams-first design suits Microsoft shops best, and third-party listings conflict, with some showing 250 euros a month and others 680 euros a month, so use the vendor page figure
#2Secureframe
Best for: Startups that want automated evidence collection with a published starting price4.7/5 on
G2 (823 reviews, checked Oct 2026)
Visit secureframe.com
Starting price$7,500/year, Fundamentals plan, vendor pricing page checked 12 Nov 2026
Free planNo free plan; demo on request
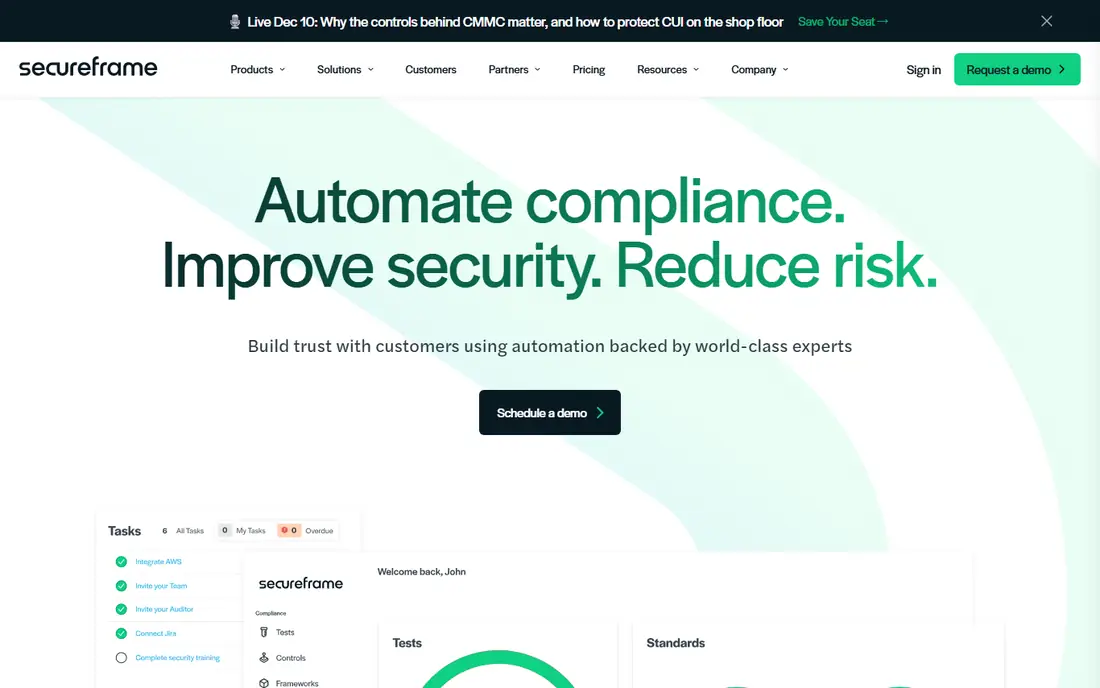
Secureframe connects to a startup cloud and SaaS stack, pulls evidence automatically, and maps controls across frameworks so NIS2 work can count toward ISO 27001 or SOC 2. The vendor pricing page checked 12 Nov 2026 lists Fundamentals from 7,500 dollars a year, with Complete and Defense sold by quote. That published price matters, because a startup can budget before a sales call. The catch is the one-framework limit, so a team that needs NIS2 and ISO 27001 together should price the upgrade.
What we like- Published starting price, automated evidence collection, 40-plus frameworks including NIS2, US or UK data centre choice, named customer success manager
Watch out for- Fundamentals covers only one framework, so NIS2 plus ISO 27001 costs more, and SSO and SCIM start on the quote-only Complete plan
#3Drata
Best for: Growing startups that want continuous control monitoring across many frameworks4.7/5 on
G2 (1,392 reviews, checked Oct 2026)
Visit drata.com
Starting pricequote
Free planNo free plan; demo on request
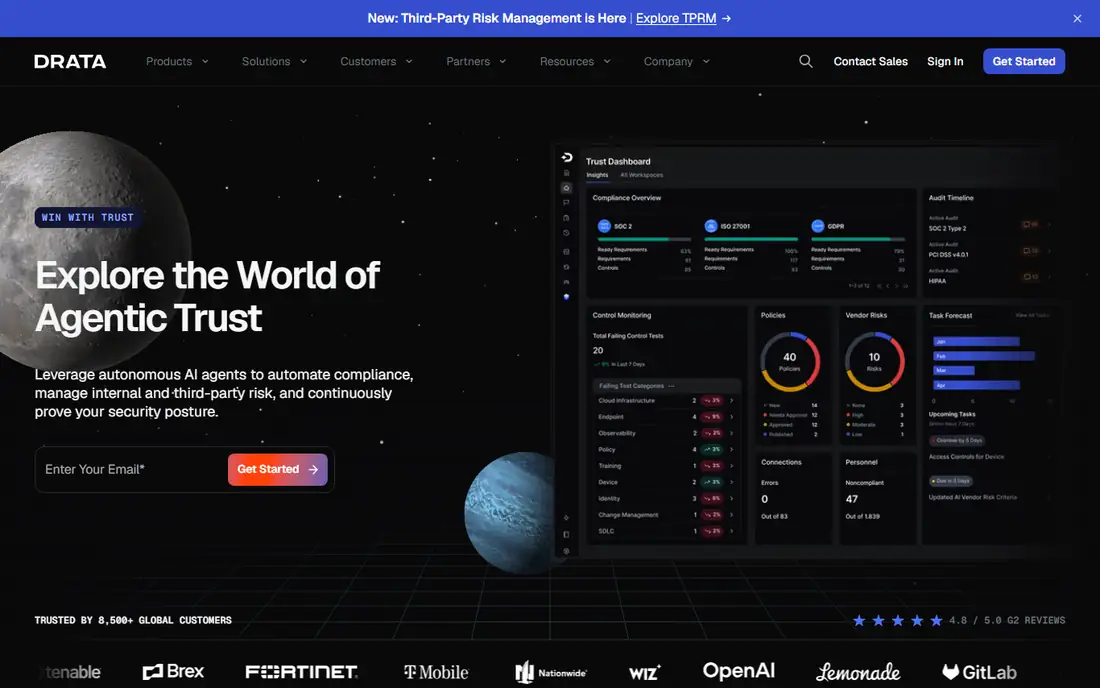
Drata connects to cloud, identity and developer tools, tests controls continuously, and collects evidence for auditors. Its library lists NIS 2 beside SOC 2, ISO 27001, GDPR and DORA, and controls mapped once can serve several frameworks. The vendor site shows no dollar figure, so the price comes from a sales quote. One source puts the entry tier at 7,500 to 15,000 dollars a year, while Vendr data puts the median near 25,000 dollars a year. Get the quote in writing with the framework count stated, and budget separately for the audit itself.
What we like- NIS 2 in a 30-plus framework library, continuous monitoring with 170-plus integrations, control mapping that reuses evidence across frameworks, trust centre and questionnaire automation
Watch out for- No published price, and third-party contract data conflicts, with entry tiers reported from about 7,500 to 15,000 dollars a year and a median near 25,000 dollars a year
#4Vanta
Best for: Startups that want a widely used compliance platform with a large integration library4.5/5 on
G2 (2,742 reviews, checked Oct 2026)
Visit vanta.com
Starting pricequote
Free planNo free plan; demo on request
Vanta is the best-known compliance automation platform for startups, and its NIS2 offering maps controls to the directive with more than 50 controls and 100 policy templates. Evidence collection runs from over 375 integrations, and the trust centre and questionnaire automation help a startup answer customer security reviews. The vendor pricing page checked 12 Nov 2026 names four plans, Essentials, Plus, Growth and Enterprise, with no dollar figures on any of them. Ask for a quote that states headcount, frameworks and add-ons.
What we like- NIS 2 mapped as a framework, more than 375 integrations, 600-plus automated tests, policy templates, trust centre, large auditor network
Watch out for- No published price, and third-party figures conflict, with entry contracts reported from about 10,000 dollars a year and a Vendr median of 20,000 dollars a year
#5Scrut
Best for: Startups that want SOC 2 first with NIS2 and other frameworks added later4.9/5 on
Capterra (139 reviews, checked Oct 2026)
Visit scrut.io
Starting price$15,000/year, AWS Marketplace listing for up to 20 employees, third-party reported, vendor pricing page returns 404
Free planNo free plan; demo on request
Scrut covers NIS2 alongside SOC 2, ISO 27001, HIPAA and GDPR, and its vendor blog describes NIS2 support with automated evidence collection and policy enforcement. It runs continuous tests, flags drift when a control slips, and keeps a live risk register next to vendor reviews and access reviews. Pricing is the weak point: the vendor pricing page returned a 404 when checked in October 2026, and the only public figure is an AWS Marketplace listing of 15,000 dollars for 12 months covering up to 20 employees. Get a written quote for a NIS2 scope before budgeting.
What we like- 70-plus frameworks, continuous tests with drift detection, risk register and vendor reviews in one place, audit centre for working with an auditor
Watch out for- No price on its own website, and the only public figure is a marketplace listing, so the quote for NIS2 scope may differ from the SOC 2 list price
#6
6clicks
Best for: Startups that want a full GRC platform with risk, audit and vendor management in one place
Visit 6clicks.com
Starting pricequote
Free planNo free plan; free trial available
6clicks is a GRC platform rather than a single-framework tool, covering risk, compliance, audit management and vendor oversight, with a library of more than 100 frameworks. Its Hailey AI engine maps obligations to controls and drafts risk assessments, which cuts manual mapping for small teams. The hub-and-spoke design also suits a startup group, since each spoke runs its own environment under one hub. The vendor pricing page checked 12 Nov 2026 lists no dollar figures, so a written quote is the only reliable figure.
What we like- 100-plus pre-built frameworks, Hailey AI for control mapping and risk assessment, hub-and-spoke model for multi-entity groups, unlimited users on enterprise licences
Watch out for- The vendor pricing page shows no dollar figures, and third-party sources conflict, reporting a Startup plan at 4,800 dollars a year in one place and about 10,000 dollars a year in another
#7OneTrust
Best for: Startups that also need privacy, consent and AI governance beside NIS24.3/5 on
G2 (155 reviews, checked Oct 2026)
Visit onetrust.com
Starting pricequote
Free planNo free plan; no public free trial, demo on request
OneTrust is the broadest platform here, joining privacy, consent, AI governance, tech risk and third-party management in one system. Its compliance module lists NIS2 among more than 50 ready-to-use frameworks, and its shared evidence framework collects evidence once and maps it across frameworks. The trade-off is scale and price: OneTrust publishes no prices and sells by personalised quote, and the old low-cost startup tiers are no longer offered. Shortlist OneTrust only when privacy work is as large as the NIS2 work.
What we like- 50-plus frameworks including NIS2, shared evidence framework that maps one control to many frameworks, strong privacy and third-party risk modules, EU hosting options
Watch out for- Enterprise quote-only pricing with usage meters, and third-party data puts the median contract near 12,000 dollars a year, which is heavy for a small startup
#8LogicGate
Best for: Startups that want to build custom risk and compliance workflows without code4.6/5 on
G2 (191 reviews, checked Oct 2026)
Visit logicgate.com
Starting pricequote
Free planNo free plan; demo on request
LogicGate Risk Cloud is a no-code GRC platform, so a startup can build applications for risk assessments, control testing, incident tracking and policy management without developers. Its content library covers NIS2 and DORA, and buyers pay for selected applications and power users, while standard and external users cost no extra. The price is the problem: the vendor publishes no prices, and third-party data puts the median contract near 54,000 dollars a year, with the lowest observed near 12,300 dollars a year. Shortlist LogicGate only when custom workflows matter more than a fixed low price.
What we like- No-code workflow builder with 30-plus pre-built applications, regulatory content covering NIS2 and DORA, standard and external users included without extra licence cost
Watch out for- Quote-only modular pricing, with third-party data putting the median contract near 54,000 dollars a year, which puts it out of reach for most startups
Frequently asked questions
Does my startup need to comply with NIS2?
Only if it falls in scope by sector and size, or if a customer in scope passes NIS2 duties down in a contract. NIS2 covers essential and important entities in listed sectors, generally medium-sized and larger, though member states may name smaller entities with a key role. A startup outside those sectors faces no direct duty, but it may still need evidence for customers.
How much does NIS2 compliance software cost for a startup?
Published prices start at 3,200 euros a year for Cyberday under 20 employees, and 7,500 dollars a year for Secureframe Fundamentals covering one framework. The other tools here publish no prices, and third-party medians run from about 12,000 dollars a year for OneTrust to about 54,000 dollars a year for LogicGate. Auditor fees and staff time sit outside the licence.
Can NIS2 software file my incident report?
No, the software cannot file the report for you. It can track the incident, gather the evidence and keep the timeline, but the entity itself must notify its CSIRT or competent authority. NIS2 sets an early warning within 24 hours, a notification within 72 hours and a final report within one month. Registration is also the entity's own duty, not the software's.
Is ISO 27001 enough for NIS2?
No, ISO 27001 helps a lot but does not cover NIS2 on its own. Many ISO 27001 controls map to the Article 21 measures, so a startup with ISO 27001 work done starts ahead. NIS2 adds its own duties, including incident reporting clocks, registration, management accountability and supply chain security. A tool that maps one control to both frameworks saves repeat work.
What is the cheapest NIS2 compliance software for startups?
Cyberday has the cheapest published price in this guide, at 267 euros a month billed annually for teams under 20 people, or 3,200 euros a year. A third-party source reports a 6clicks Startup plan at 4,800 dollars a year, but the vendor page shows no price, so that figure is unverified. The cheapest list price is not always the cheapest total cost.
Sources we checked (9)
- https://eur-lex.europa.eu/eli/dir/2022/2555/oj
- https://www.cyberday.ai/pricing
- https://secureframe.com/pricing
- https://drata.com
- https://www.vanta.com/pricing
- https://scrut.io/post/eu-compliance-regulations
- https://6clicks.com/pricing
- https://www.onetrust.com
- https://www.logicgate.com
How we picked
We picked tools with named NIS2 coverage on the vendor site, a working official website checked 12 Nov 2026, and a fit for small teams without a compliance hire. We checked each vendor pricing page on 12 Nov 2026 and recorded quote-only pricing where no figure was published, with third-party medians flagged as reported rather than vendor figures.
Last verified: 12 November 2026
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.