How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- HackerOne has the largest program volume and the best learning library, but also the fiercest competition on public programs.
- Intigriti and Bugcrowd are often the most forgiving starting points, with clearer onboarding and faster feedback for new researchers.
- Read disclosed reports and program scope documents before you test anything, because scope violations waste time and harm reputation.
- Private program invitations, earned through valid reports, usually pay better and face less competition than crowded public programs.
- Your first bounty is often a low or medium severity finding, so set expectations around learning and valid reports, not large payouts.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 HackerOne | Largest program choice and learning resources | Free to join | Yes |
 Bugcrowd | Balanced progression from public to private programs | Free to join | Yes |
 Intigriti | Beginners who want fast feedback and European programs | Free to join | Yes |
 YesWeHack | European programs with managed support | Free to join | Yes |
 HackenProof | Crypto and web programs for newer researchers | Free to join | Yes |
 Open Bug Bounty | Responsible disclosure practice without payout pressure | Free to join | Yes |
 Synack | Vetted researchers ready for higher value work | Free to join | Yes |
 Immunefi | Web3 researchers targeting smart contracts later | Free to join | Yes |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
#1HackerOne
Best for: Largest program choice and learning resources4.5/5 on
G2 (94 reviews, checked Oct 2026)
Visit hackerone.com
Starting priceFree to join
Free planYes
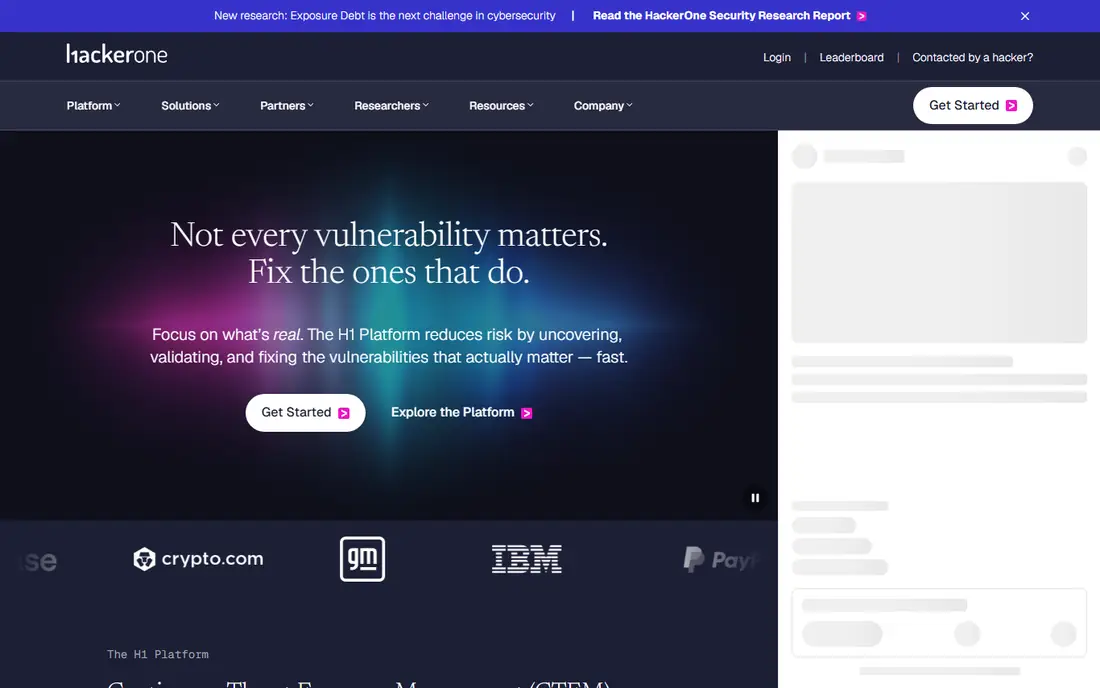
HackerOne is the default starting point because it has the most programs, the most disclosed reports, and the most learning material in one place. Hacker101 teaches common vulnerability types with labs, and Hacktivity lets you read real, resolved reports to see how researchers found a bug, how they wrote it up, and how the company fixed it. That library alone makes HackerOne valuable even before your first bounty.
Competition is the drawback. Popular public programs attract thousands of researchers, so common bugs are found fast and duplicates are common. HackerOne reputation, signal, and impact scores also affect private invitations, and a string of invalid reports can slow your progress. Start with a smaller, less crowded program, read its scope carefully, and focus on one vulnerability class. Used that way, HackerOne is the best long term platform, even if your first valid report comes elsewhere.
What we like- Largest public program directory
- Hacker101 training and disclosed Hacktivity reports
- Clear path to private programs
Watch out for- Public programs are crowded
- Reputation penalties for invalid reports can hurt beginners
- Competition for common bugs is high
#2Bugcrowd
Best for: Balanced progression from public to private programs4.3/5 on
G2 (61 reviews, checked Oct 2026)
Visit bugcrowd.com
Starting priceFree to join
Free planYes
Bugcrowd sits between HackerOne scale and Intigriti friendliness. Its managed triage means a Bugcrowd team often validates reports before they reach the customer, which can give beginners clearer feedback than a direct to customer model. CrowdMatch also routes researchers toward programs that match their skills and track record, so as you earn valid reports, better invitations follow. That progression is motivating for a beginner who wants a visible path forward.
The platform is smaller than HackerOne, so program choice is narrower, and some attractive programs are private or application based. Bugcrowd also serves US government, fintech, and healthcare programs, which can have stricter scope and disclosure rules, so read each program brief closely. For a beginner who wants structure and feedback, Bugcrowd is an excellent second platform, and a good first choice if HackerOne feels overwhelming.
What we like- Managed triage on many programs
- CrowdMatch routing to suitable programs
- Researcher ratings that reward accuracy
Watch out for- Program volume is smaller than HackerOne
- Some programs require an application or invitation
#3Intigriti
Best for: Beginners who want fast feedback and European programs4.7/5 on
G2 (32 reviews, checked Oct 2026)
Visit intigriti.com
Starting priceFree to join
Free planYes
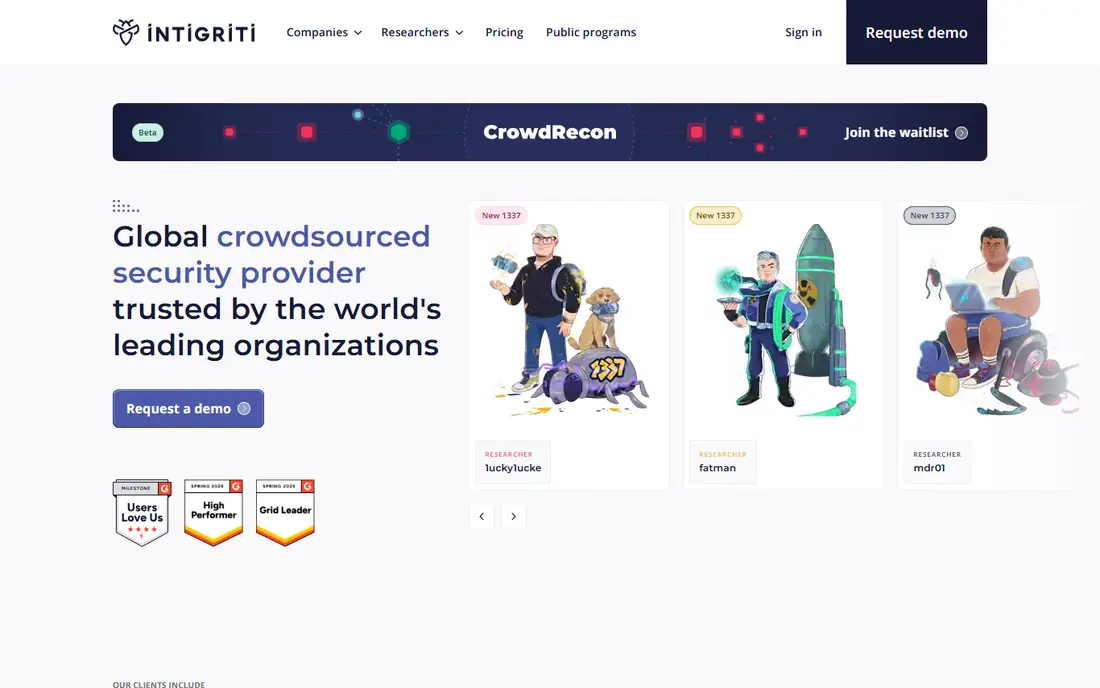
Intigriti is frequently recommended as the best first platform for complete beginners, and the reasons are practical: onboarding is clean, triage is often fast, and the reputation system rewards recent activity, so a new researcher is not permanently behind long time hunters. European companies form a large part of the program list, which also means less competition on some programs than on the most popular US targets, and GDPR focused scope documents are often clear about what is allowed.
The trade off is scale. Intigriti has fewer programs than HackerOne, and US focused hunters may find fewer domestic targets. The platform also uses public, private, application, and registered confidentiality modes, so check the mode before you start, because it affects disclosure and invitation. If you are starting from zero, Intigriti is the friendliest place to earn your first valid reports and build confidence.
What we like- Clean onboarding
- Fast triage reported by many researchers
- Seasonal reputation that rewards current activity
Watch out for- Program volume is smaller than HackerOne
- European focus means fewer US programs
#4YesWeHack
Best for: European programs with managed support4.8/5 on
G2 (33 reviews, checked Oct 2026)
Visit yeswehack.com
Starting priceFree to join
Free planYes
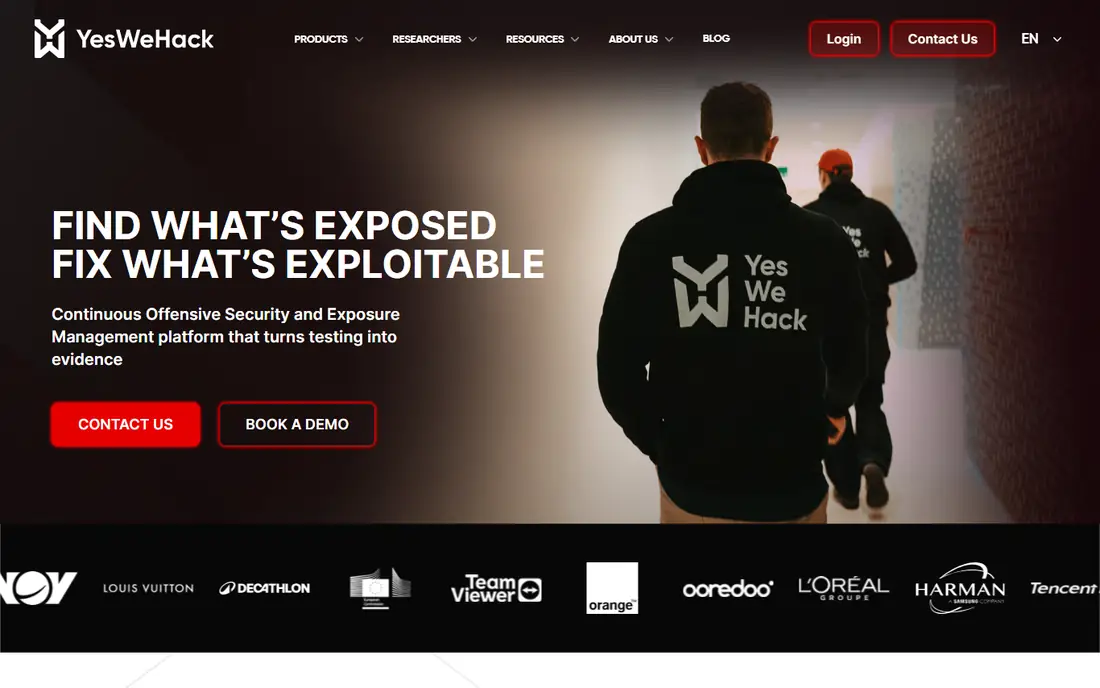
YesWeHack is a European platform with a growing program list, including automotive, technology, and public sector targets that do not appear on US platforms. Programs often start private before expanding to public, which can give early researchers a less crowded field, and managed support helps with triage and communication. For a researcher based in Europe, or targeting European companies, YesWeHack is a serious alternative to Intigriti.
Scale and language are the limits. The program list is smaller than the giants, and some programs operate primarily in French, which can be a barrier if you do not read French. Rewards on named public programs commonly range from 100 euros to several thousand euros depending on severity, so set expectations accordingly. Add YesWeHack once you have a few valid reports, or start here if European targets are your focus.
What we like- Strong European program list, including automotive and French companies
- Managed programs with clear scope
- Growing community
Watch out for- Smaller than HackerOne and Bugcrowd
- Fewer English language programs than some rivals
Starting priceFree to join
Free planYes
HackenProof covers both traditional web programs and crypto and blockchain targets, which gives a beginner two learning paths in one account. Web programs let you practice common vulnerabilities such as cross site scripting, authentication flaws, and API issues, while crypto programs introduce wallet, exchange, and smart contract attack surfaces. Public listings often show bounty ranges, so you can judge whether a program is worth your time before you start.
The highest payouts on HackenProof usually require smart contract or blockchain expertise, which most beginners do not have yet, so start with web programs and build toward crypto targets. Program volume is also smaller than HackerOne or Bugcrowd. For a beginner who is curious about crypto security but wants to start with web basics, HackenProof is a useful additional platform.
What we like- Mix of crypto and traditional web programs
- Beginner accessible public programs
- Clear bounty ranges on many listings
Watch out for- Crypto focus means smart contract skills help for the highest payouts
- Program volume is smaller than the leaders
#6Open Bug Bounty
Best for: Responsible disclosure practice without payout pressure3.7/5 on
G2 (11 reviews, checked Oct 2026)
Visit openbugbounty.org
Starting priceFree to join
Free planYes
Open Bug Bounty is different from the other platforms here, because it focuses on responsible disclosure for websites that may not run a formal bounty program. A beginner can practice finding a vulnerability, writing a clear report, and following a disclosure process, without the pressure of competing for a payout or protecting a reputation score. That practice is valuable, because report quality often decides whether a valid bug is accepted and paid on paid platforms.
The limit is money. Many Open Bug Bounty disclosures receive no payment, only recognition, so treat it as training, not income. You must still follow responsible disclosure rules, give the owner time to fix the issue, and never test a system aggressively or without a legal basis. Use Open Bug Bounty to sharpen reporting skills, then move paid hunting to HackerOne, Bugcrowd, or Intigriti.
What we like- Open disclosure model for websites without a formal program
- Good for practicing report writing
- No program application needed
Watch out for- No guaranteed payouts
- Many targets have no bounty
- Not a substitute for a paid platform
#7Synack
Best for: Vetted researchers ready for higher value work4.8/5 on
G2 (21 reviews, checked Oct 2026)
Visit synack.com
Starting priceFree to join
Free planYes
Synack is included here as a goal, not a starting point, because beginners need to know where the path leads. The Red Team model vets researchers, gives controlled access to targets, and rotates assignments to reduce duplicate work, which means less wasted effort than on crowded public programs. Missions and vulnerabilities can pay well, with vulnerability payments commonly in the hundreds to thousands of dollars depending on severity.
Access is the barrier. Synack is invite only, requires vetting, and suits intermediate to expert researchers, so a beginner should not apply on day one. Build a track record on HackerOne, Bugcrowd, or Intigriti first, with valid reports and clean scope compliance, then apply when you have evidence of skill. Knowing Synack exists helps you plan that progression, rather than chasing only public bounties forever.
What we like- Vetted Red Team model with less public competition
- Controlled target access
- Mission based work with guaranteed pay elements
Watch out for- Invite only and heavily vetted, so not a beginner starting point
- Requires experience and an application process
Starting priceFree to join
Free planYes
Immunefi specializes in Web3 and crypto, with bounties for smart contracts, DeFi protocols, and blockchain infrastructure. Critical bugs on major protocols can pay extremely large amounts compared with web programs, which is why Immunefi attracts experienced blockchain researchers. Its severity framework and payout guidance are clear, so you can see what a critical, high, or medium finding is worth before you start.
For a pure beginner, Immunefi is a stretch goal. Smart contract auditing requires Solidity, DeFi mechanics, and tooling that web hunting does not teach, and top programs are highly competitive. Start with web platforms, learn the fundamentals, then study smart contracts separately if Web3 interests you. If you already have blockchain skills, Immunefi is the platform to prioritize.
What we like- Largest Web3 bounty platform
- Very large payouts for critical smart contract bugs
- Clear severity and payout frameworks
Watch out for- Requires smart contract and DeFi knowledge
- Not beginner friendly for web only researchers
- High competition for top programs
How we chose
We compared program directories, onboarding, triage models, reputation systems, learning resources, payout guidance, and public researcher reviews, alongside platform documentation. We favored platforms that are free for researchers, publish clear scope and disclosure rules, and offer a realistic path from public programs to private invitations, and we included stretch platforms such as Synack and Immunefi so beginners can see the full progression.
How to get your first valid report
Pick one platform and one program, then read everything before you test. Read the scope, the out of scope list, the bounty table, and at least five disclosed reports for that program or a similar one. Choose a narrow focus for your first month, such as cross site scripting, broken access control, or API authorization, and learn its test cases deeply, rather than scanning for every bug type at once.
Write reports as if a busy engineer will read them. Include a clear title, steps to reproduce, impact, a proof of concept that stays inside scope, and a suggested fix. Avoid automated scanner dumps, avoid testing out of scope assets, and do not submit a report you have not reproduced. A single valid, well written report that earns a private invitation is worth more than ten rushed, invalid submissions.
Beginner starter plan
- Week one: join Intigriti and HackerOne, complete Hacker101, and read 20 disclosed reports.
- Week two: pick one program, read its scope twice, and map its assets and authentication flows.
- Week three: test one vulnerability class thoroughly, take notes, and reproduce every finding.
- Week four: submit your best finding with a clear write up, then review the triage feedback and adjust.
Frequently asked questions
Do I need to pay to join a bug bounty platform?
No. Researcher accounts on HackerOne, Bugcrowd, Intigriti, and the other platforms here are free to join. Platforms earn revenue from customers who run programs, not from researchers, and payouts go to researchers for valid findings.
How much can a beginner earn from bug bounties?
A first bounty is often a low or medium severity finding worth tens to a few hundred dollars, and many beginners earn nothing in their first months while learning. Experienced researchers earn far more, but treat early bug bounty work as paid learning, not as a reliable income, until you have a consistent record of valid reports.
Do I need certifications to start bug bounty hunting?
No certification is required to join a platform, but foundational knowledge in web security, HTTP, authentication, and common vulnerabilities helps greatly. Free training such as Hacker101, PortSwigger Web Security Academy, and TryHackMe rooms can build that foundation before you hunt live targets.
Is bug bounty hunting legal?
Yes, when you test only systems that are in scope for a program you have joined, follow the program rules, and do not access, alter, or exfiltrate data beyond what the program allows. Testing a system without permission, even with good intentions, can be illegal, so scope compliance is essential.
What is the difference between a public and a private program?
Public programs are open to any researcher on the platform, so competition is high. Private programs invite selected researchers based on reputation, skill, and track record, so competition is lower and payouts are often higher. Valid public reports are the usual route to private invitations.
How do I choose between HackerOne, Bugcrowd, and Intigriti?
Start with Intigriti if you want the gentlest onboarding, Bugcrowd if you want structured triage and progression, and HackerOne if you want the largest program choice and learning library. Many researchers eventually use all three, but start with one program on one platform to avoid spreading your effort too thin.
Sources we checked (9)
- https://www.hackerone.com
- https://www.bugcrowd.com
- https://www.intigriti.com
- https://www.yeswehack.com
- https://hackenproof.com
- https://www.openbugbounty.org
- https://www.synack.com
- https://immunefi.com
- https://www.cloudsek.com/knowledge-base/best-bug-bounty-platforms
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.