How we make this list: we compare pricing pages, product documentation and public user reviews. Rankite is independent; if a vendor ever pays for a featured spot, that listing is clearly labeled Partner.
Key takeaways
- Magnet AXIOM and Cellebrite anchor most modern labs: AXIOM for computer and cloud evidence, Cellebrite for mobile extraction.
- Exterro FTK remains the heavyweight for processing huge datasets fast, now inside Exterro's wider data risk platform.
- Oxygen Forensic Detective and Belkasoft X are strong mid-market picks with broad device support and friendlier pricing conversations.
- X-Ways Forensics is the examiner's scalpel: fast, precise, and demanding of real expertise.
- Autopsy is free and open source, which makes it the default for students, small agencies, and anyone validating findings with a second tool.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
 Magnet AXIOM | Computer, mobile and cloud investigations in one case file | See website | No |
 Cellebrite | Mobile extraction at any skill level | See website | No |
 Exterro FTK | Processing massive datasets quickly | See website | No |
 Oxygen Forensic Detective | Shops needing the widest device coverage | See website | No |
 X-Ways Forensics | Examiners who want total control | See website | No |
 Autopsy | Free investigations and second opinions | Free | Yes |
 Belkasoft X | Acquisition-to-report in one suite | See website | Free trial |
 Elcomsoft | Breaking into encrypted evidence | See website | No |
 Passware Kit | Decrypting files, disks, and phones | See website | No |
 Paraben E3 | Agencies watching the budget | See website | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
Nobody buys forensic software casually. Every purchase here runs through procurement, needs courtroom defensibility, and gets compared against whatever the lab already owns. So here is the honest framing: there is no single best tool, only the right combination for your caseload. Mobile-heavy shops start with Cellebrite or Oxygen. Computer-heavy labs start with AXIOM or FTK. Everyone needs a decryption answer (Elcomsoft or Passware) and a second opinion tool (Autopsy, X-Ways). The ten below cover that full spread.
Starting priceSee website
Free planNo
Magnet AXIOM is the closest thing digital forensics has to a default platform. AXIOM Process acquires from computers, phones, and cloud sources, and AXIOM Examine stitches it all into one timeline with artifacts parsed for hundreds of apps. For labs that handle mixed-device cases, which is nearly everyone now, that unified view saves hours of correlation work.
The tradeoff is cost and compute. Pricing runs through sales, and it is enterprise-priced. Large cases also want a well-specced processing machine. But the artifact coverage, the update cadence, and the ecosystem (including Graykey for iOS access and Magnet Review for sharing) make AXIOM the safe center of a lab's toolkit.
What we like- Single timeline across computer, mobile, and cloud evidence
- Strong artifact support and frequent updates
- Magnet Review helps share findings with non-technical stakeholders
Watch out for- Quote-based enterprise pricing
- Processing large cases demands serious hardware
Starting priceSee website
Free planNo
Cellebrite built its name on getting data off locked phones, and it still leads there. UFED and the newer Genesis platform cover extraction, decoding, and analysis, with field kits that let officers triage devices at the point of capture. The analytics layer helps teams move from raw extraction to actual investigative insight.
It is the most expensive answer to the mobile question, and buyers should go in expecting hard questions from oversight bodies about capabilities and use policies. For agencies where mobile evidence decides cases, though, there is a reason Cellebrite is standard issue.
What we like- Deepest mobile extraction capabilities in the industry
- Field-ready kits for on-scene triage
- Strong analytics and case management around the extraction
Watch out for- Premium pricing
- Some advanced capabilities draw public scrutiny, so expect procurement questions
Starting priceSee website
Free planNo
FTK (Forensic Toolkit) earned its reputation on speed: it was built to index and search terabytes when competitors choked. Under Exterro, it is now the Exterro FTK Suite inside a broader data risk management platform spanning eDiscovery, privacy, and breach response.
That platform story is a plus for enterprises and large agencies that want forensics connected to legal workflows, and a needless complication for small labs that just want fast processing. Either way, when the dataset is huge and the deadline is short, FTK is still the tool examiners reach for.
What we like- Legendary processing speed and distributed architecture
- Now part of a unified eDiscovery and forensics platform
- Proven in the largest investigations
Watch out for- Enterprise sales process
- The platform story is bigger than many labs need
Starting priceSee website
Free planNo
Oxygen Forensic Detective is the completeness pick. Mobile, computer, cloud, drones, call data records, it ingests from a remarkable range of sources and gives you timeline, link analysis, and geo-mapping to make sense of it. The cloud extraction coverage (100+ services) is a genuine differentiator as cases keep moving off devices.
The interface reflects the feature count: powerful but dense. Pricing is quote-based through the vendor. For labs that never know what device will walk through the door next, Oxygen's breadth is hard to beat.
What we like- 35,000+ supported devices plus 100+ cloud services
- Good link analysis, mapping, and facial categorization
- Collaborative review options
Watch out for- Quote-based pricing
- Interface packs in a lot, which takes learning
Starting priceSee website
Free planNo
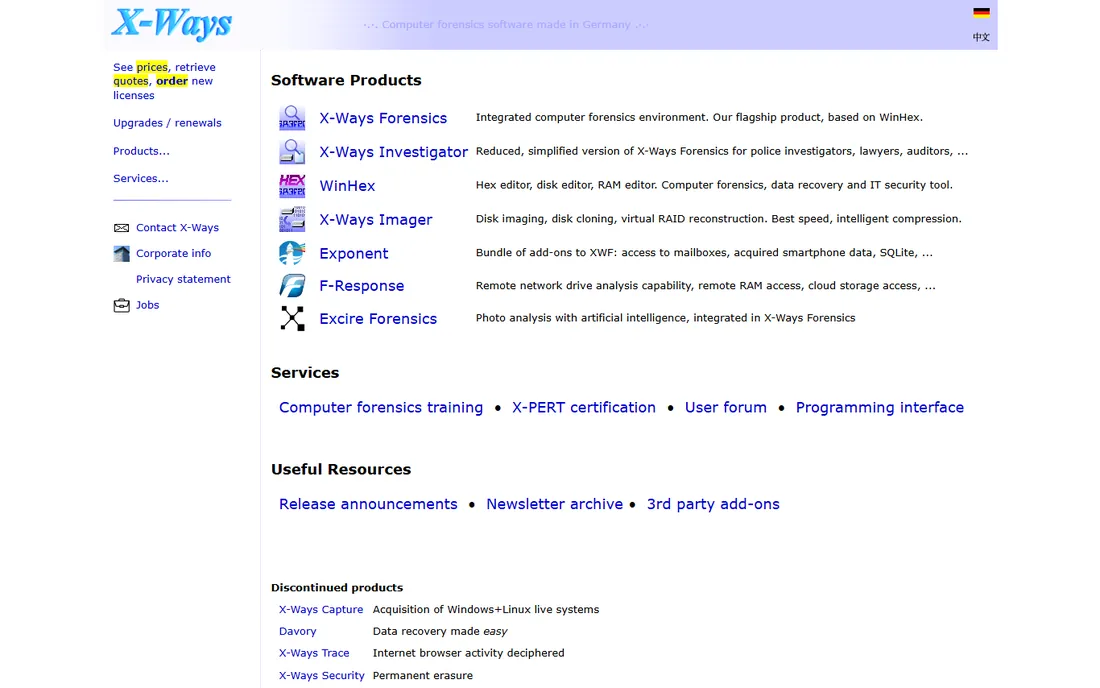
X-Ways Forensics is the tool senior examiners quietly love. Built on WinHex, it is fast, precise, and stays out of your way, giving you direct access to disk structures, file systems, and data carving with minimal overhead. It runs well on modest hardware where heavier suites crawl.
It is not a beginner tool. X-Ways assumes competence: the interface is dense, the documentation is technical, and there is no hand-holding wizard layer. Pair it with a more automated suite for triage, and use X-Ways when you need to verify, dig deeper, or work a case the automated tools cannot quite crack.
What we like- Extremely fast and resource-light
- Fine-grained hex-level control
- Honest one-time licensing from a small vendor
Watch out for- Steep learning curve
- Assumes you already understand file systems
Starting priceFree
Free planYes
Autopsy, built on The Sleuth Kit, is the free backbone of digital forensics education and a legitimate casework tool. It handles disk images and mobile extractions with timeline analysis, keyword search, hash filtering, and a plugin architecture that the community keeps extending.
It will not outrun FTK on a multi-terabyte case, and when something breaks you are reading forums, not calling support. But as a training platform, a validation tool (run the same image through Autopsy and your commercial suite and compare), and an option for agencies with no budget, it is indispensable. Every lab should have it installed even if it is not the primary tool.
What we like- Completely free and open source
- Modular with community plugins
- Widely used for training and validation
Watch out for- Slower than commercial tools on big cases
- Support is community-based
- Interface shows its open-source roots
Starting priceSee website
Free planFree trial
Belkasoft X pitches itself as the complete investigation in one product: acquire from mobile, computer, and cloud sources, analyze with timeline and artifact parsing, then build court-ready reports. It is a genuine all-rounder, and the free trial means you can test it on your own casework before talking to sales.
The company is smaller than the two giants, which cuts both ways: more responsive support and development, less market inertia behind it. For mid-size labs and corporate DFIR teams that want one suite without enterprise-platform complexity, Belkasoft X deserves a slot on the shortlist.
What we like- Covers the full workflow from acquisition to reporting
- Strong mobile and computer artifact support
- Free trial available
Watch out for- Quote-based pricing
- Smaller vendor than Magnet or Cellebrite
Starting priceSee website
Free planNo
Every lab eventually hits a locked device or an encrypted container, and that is Elcomsoft's entire business. Its tools recover passwords, break into iOS backups and cloud accounts, and decrypt disks, using GPU acceleration to make brute force practical. The products are mature and the update pace tracks new OS releases closely.
This is a specialist, not a suite: you buy Elcomsoft alongside your main forensic platform, not instead of it. Note that some products carry export or jurisdictional restrictions, so procurement needs to check eligibility early.
What we like- Deep password recovery and decryption expertise
- GPU-accelerated attacks
- Tools for iOS, cloud, and desktop encryption
Watch out for- Narrow focus (decryption, not full investigations)
- Some tools have jurisdictional purchase restrictions
Starting priceSee website
Free planNo
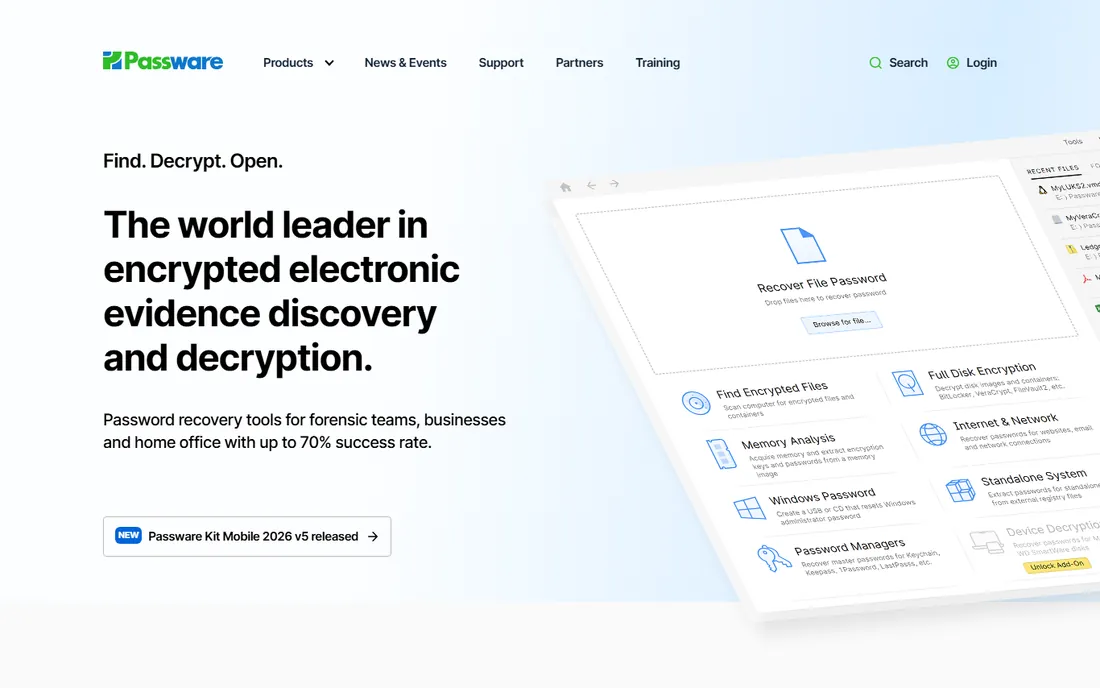
Passware Kit takes a smart approach to the decryption problem: it scans a case, finds every encrypted file and disk, identifies the encryption type, and tells you how hard each one will be to crack. That triage alone saves labs from burning weeks on hopeless passwords. When a target is crackable, distributed agents and GPU acceleration do the work.
The honest caveat applies to every decryption vendor: a long random password will not fall, no matter the software. Passware's value is in finding the weak ones fast and telling you which ones to deprioritize. It is a standard companion to AXIOM, FTK, or Autopsy in serious labs.
What we like- Detects encryption and estimates crack difficulty before you commit time
- Distributed password recovery across agents
- Strong mobile passcode recovery
Watch out for- Annual or multi-year licensing
- Success depends on password strength, which no tool can fix
Starting priceSee website
Free planNo
Paraben has been in forensics since 1999 and positions E3 as the affordable all-rounder. The Digital Investigator Membership bundles software, support, and training certification into a monthly or annual fee, which is easier for small agencies to budget than a five-figure perpetual license. Coverage spans phones, computers, and IoT, with newer AI features for correlation and link mapping.
You give up some depth: the artifact and device support lists are shorter than Cellebrite's or Magnet's. But for sheriff's offices, small departments, and private consultants, Paraben's combination of price, training, and support is a pragmatic package.
What we like- Membership pricing (monthly or annual) instead of big upfront licenses
- Mobile, computer, and IoT coverage
- Includes training and AI-assisted analysis
Watch out for- Smaller artifact library than the giants
- Membership model means costs never stop
Three questions decide the shortlist. First, what is your caseload: mobile-heavy (Cellebrite, Oxygen), computer-heavy (AXIOM, FTK, X-Ways), or mixed (AXIOM, Belkasoft, Paraben)? Second, what is your budget model: big upfront licenses, annual renewals, or Paraben-style membership? Third, who does the work: seasoned examiners who will love X-Ways, or a mixed team that needs guided workflows? Answer those and the field narrows fast. Whatever you pick, budget for training; the tool is only as good as the examiner driving it, and every vendor here sells training for a reason.
Frequently asked questions
What is the best digital forensics software for law enforcement?
Most agencies standardize on Magnet AXIOM for computers and cloud plus Cellebrite for mobile devices. Smaller departments often pick Paraben E3 or Belkasoft X for cost reasons, and nearly everyone keeps Autopsy installed as a free second tool.
Is there really a free forensic tool worth using?
Yes: Autopsy. It is open source, widely used in training and real casework, and good enough to validate findings from commercial tools. It is slower on huge datasets and community-supported, but the price is right.
How much does forensic software cost?
Vendors rarely publish prices; nearly everything here is quote-based and typically runs from thousands to tens of thousands per seat per year depending on modules. Autopsy is free, Paraben uses monthly or annual membership pricing, and X-Ways is known for straightforward one-time licensing.
Do I need separate tools for mobile and computer forensics?
Increasingly, no. AXIOM, Oxygen, Belkasoft X, and Paraben E3 all handle mobile, computer, and cloud sources in one case file. Specialists still lead at the extremes: Cellebrite for mobile extraction depth, X-Ways for low-level disk work.
What about encrypted phones and files?
That is a separate purchase. Elcomsoft and Passware specialize in password recovery and decryption and are designed to sit alongside your main forensic suite. No tool can crack a strong passphrase, so these are for finding the weak ones fast.
Can forensic findings be used in court?
Tools like these are designed for courtroom admissibility, with hashing, audit logs, and chain-of-custody features. But admissibility depends in the end on the examiner's methods and documentation, not the logo on the software. Training and validated workflows matter as much as the tool.
How we chose
We verified each vendor's current homepage and product lineup, then evaluated on device and artifact coverage, lab reputation (practitioner forums, conference talks, and published reviews), pricing model transparency, and fit for different buyers: large agencies, small departments, corporate DFIR teams, and students. We did not perform hands-on examinations. Note that this category moves with OS releases, so confirm current device support with the vendor before buying.
Sources we checked (10)
- https://magnetforensics.com/
- https://cellebrite.com/
- https://exterro.com/
- https://oxygenforensics.com/
- https://www.x-ways.net
- https://sleuthkit.org/
- https://belkasoft.com
- https://www.elcomsoft.com
- https://passware.com/
- https://paraben.com/
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has spent more than a decade helping SaaS and e-commerce brands grow through search. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.