How we make this list: we compare pricing pages, product documentation and public user reviews. Ratings come from G2, Capterra or Trustpilot, with the date we checked them.
Key takeaways
- Invicti and Acunetix, from the same company, are the proof based scanning leaders: they confirm most findings by safely exploiting them, which ends the false positive argument with developers.
- Burp Suite Enterprise brings the tool penetration testers trust to scheduled, organisation wide DAST, and OWASP ZAP remains the free open source scanner every programme should know.
- Rapid7 InsightAppSec, Qualys WAS, and Veracode DAST serve platform estates: scanning inside the vulnerability or application security programme you already run.
- StackHawk is the developer first option, DAST wired into CI so findings arrive where engineers work.
- Only scan systems you own or have written permission to test. DAST is active attack simulation; pointing it at someone else's application is a crime in most jurisdictions, not research.
Quick comparison
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
#1Invicti
Best for: Proof based enterprise DAST4.5/5 on
G2 (72 reviews, checked Oct 2026)
Visit invicti.com
Starting priceSee website
Free planNo
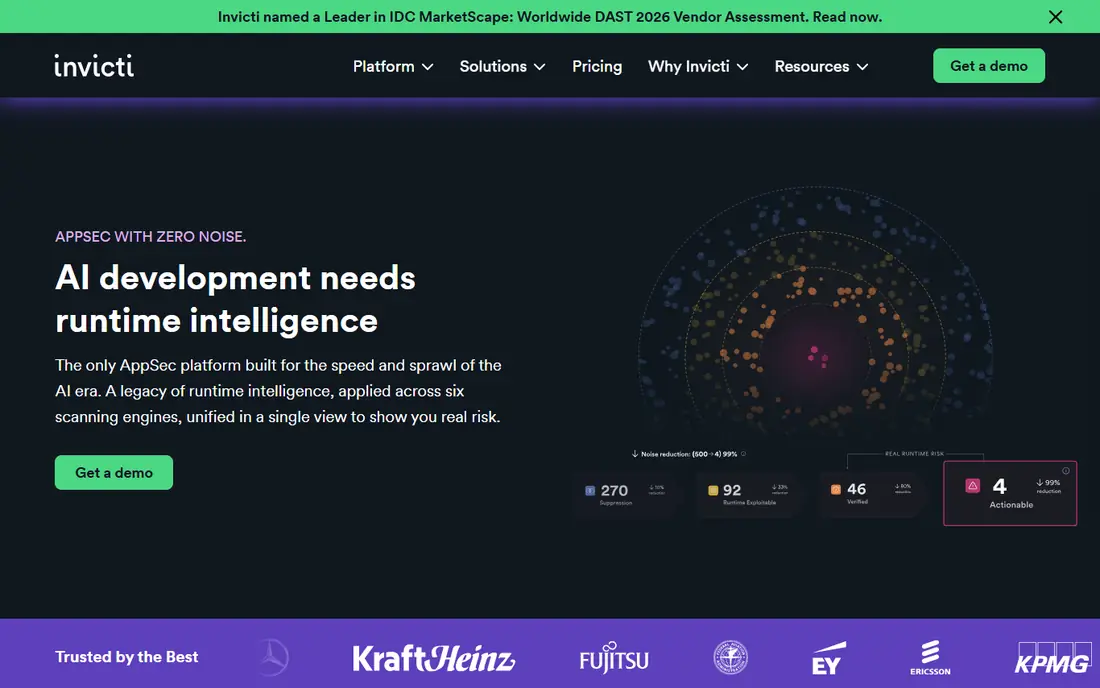
Invicti's claim on the top spot is its proof based approach: for most vulnerability classes it confirms exploitability with safe test attacks, so a finding arrives with evidence attached. Developer teams stop arguing about scanner noise, which is the political problem that kills DAST programmes.
The trade off is enterprise weight and price. Invicti fits organisations scanning many applications and APIs continuously, where confirmed findings and programme reporting justify the contract.
What we like- Proof based scanning safely confirms exploitable findings, cutting false positives sharply
- Scans web apps and APIs at enterprise scale and speed
- The former Netsparker engine, mature and well supported
- Strong compliance reporting
Watch out for- Enterprise pricing by quote
- Depth assumes a security team to run the programme
- Interface serves professionals more than occasional users
#2Acunetix
Best for: Fast, accurate web scanning4.1/5 on
G2 (105 reviews, checked Oct 2026)
Visit acunetix.com
Starting priceSee website
Free planNo
Acunetix is Invicti's sibling product, tuned for speed and for teams that want the same confirmed accuracy without the full enterprise platform around it. Its crawler handles the JavaScript heavy applications that defeat simpler scanners.
The trade off against Invicti is platform against agility, and buyers should trial both since the vendor sells both. Acunetix fits mid size companies and smaller security teams that want serious scanning running this month.
What we like- Shares Invicti's proof based technology with a faster, simpler product feel
- Strong crawl of complex modern web apps
- Multi engine scanning combines DAST with software composition checks
- Good for smaller security teams
Watch out for- Also quote priced
- Overlapping ownership with Invicti confuses buyers comparing the two
- Advanced programme features sit higher in the Invicti line
Starting priceSee website
Free planNo
Burp Suite Enterprise automates the scanner inside the tool your penetration testers already trust, which settles the credibility argument in both directions: developers respect the findings, testers respect the engine. It schedules recurring scans across the estate and feeds results into development workflows.
The trade off is depth of scanning against breadth of programme features. Burp Enterprise fits organisations with in house testing culture that want continuous DAST aligned with their manual testing standard.
What we like- Built on the Burp engine penetration testers use daily, so findings carry credibility with both testers and developers
- Scheduled and CI triggered scanning across many sites
- Central console for the estate
- PortSwigger's research keeps checks current
Watch out for- Quote based pricing per scanned site
- Less programme management gloss than Invicti
- Assumes familiarity with Burp concepts
#4OWASP ZAP
Best for: Free open source scanning4.7/5 on
G2 (14 reviews, checked Oct 2026)
Visit zaproxy.org
Starting priceFree
Free planYes
ZAP is the people's scanner: a full featured intercepting proxy and automated scanner that any team can run tonight for nothing, scriptable through its automation framework for pipelines. Its findings need more human triage than Invicti's, and its price is zero, which is the correct trade for most small programmes.
The trade off is money against time. ZAP fits startups, small teams, and learners, and sits inside many commercial programmes as the always on baseline between premium scans.
What we like- Completely free and open source, maintained under OWASP
- Automation framework and APIs make it a CI scanning workhorse
- Huge community, add ons, and documentation
- The standard learning tool for web security testing
Watch out for- More false positives and tuning burden than the proof based commercials
- Support is community only
- Reporting needs work before an auditor sees it
#5Rapid7 InsightAppSec
Best for: Cloud DAST in the Rapid7 stack3.9/5 on
G2 (10 reviews, checked Oct 2026)
Visit rapid7.com
Starting priceSee website
Free planNo
InsightAppSec is the DAST for Rapid7 shops: scans scheduled from the cloud, findings flowing into the same console as the rest of the vulnerability programme, and attack replay that shows a developer exactly what the scanner did. Its crawler is notably good with modern JavaScript applications.
The trade off is ecosystem value against standalone depth. InsightAppSec fits mid size and large companies standardised on Rapid7 that want DAST reporting beside their infrastructure risk.
What we like- Cloud delivered DAST with strong handling of modern single page apps and APIs
- Integrates with InsightVM so application and infrastructure findings share one risk picture
- Attack replay helps developers reproduce findings
- Clear per application pricing model
Watch out for- Pricing by application count adds up across big estates
- Best value inside the Rapid7 platform
- Scan depth on exotic stacks trails the specialists slightly
#6Qualys WAS
Best for: Scanning inside Qualys estates4.5/5 on
G2 (21 reviews, checked Oct 2026)
Visit qualys.com
Starting priceSee website
Free planNo
Qualys WAS makes web scanning one more sense in a platform the security team already runs: findings join the same asset and risk record as network vulnerabilities, and API testing driven by your actual specifications keeps coverage honest.
The trade off mirrors other platform entries: convenience for the installed base, less reason to buy standalone. Qualys WAS fits Qualys estates that want web and API coverage without a second vendor and console.
What we like- Web application scanning inside the Qualys platform, beside VMDR and patch data
- Covers web apps and APIs with Swagger and Postman driven testing
- Strong compliance and certificate reporting
- Sensor options for internal applications
Watch out for- Interface and workflow serve Qualys platform users
- Proof style confirmation is thinner than Invicti's
- Pricing by module and quote
Starting priceSee website
Free planNo
Veracode sells the programme, not the scan: its DAST runs alongside static and composition analysis under one policy and reporting roof, so an enterprise can state its application security posture in a single number set. Regulated buyers have trusted that structure for years.
The trade off is programme breadth against agility and price. Veracode fits enterprises that report application risk to boards and regulators and need every testing type governed together.
What we like- DAST inside a full application security platform with SAST and software composition analysis
- Programme level reporting executives and auditors accept
- Scans authenticated applications and APIs at scale
- Strong in regulated industries
Watch out for- Platform pricing by quote
- Scan tuning takes services and time
- Developer experience trails the developer first tools
#8StackHawk
Best for: Developer first CI scanning4.6/5 on
G2 (68 reviews, checked Oct 2026)
Visit stackhawk.com
Starting priceSee website
Free planYes
StackHawk starts from a different premise: DAST belongs in the pipeline, run by developers, on the application as built today. Its scanner is configured in code, runs in minutes, and files findings where engineers already work, which gives it adoption rates security run tools envy.
The trade off is shift left speed against estate scanning depth. StackHawk fits product engineering organisations that want continuous DAST in CI, usually beside a periodic deep scan from one of the platforms above.
What we like- Built to run in CI on every pull request and release, testing running apps and APIs with the build
- Findings land in the developer's workflow with reproduction detail
- Fast scans tuned for pipelines
- A free tier starts small teams
Watch out for- Pipeline speed trades away the depth of a long enterprise scan
- Enterprise estate management is younger
- Pricing tiers by application and usage need checking
How we chose
We compared the DAST tools security teams shortlist, requiring modern web and API coverage, authenticated scanning, and automation support from every entry. Pricing in enterprise DAST is quoted per application or estate almost everywhere, so we marked it See website and published only the structurally free facts: ZAP costs nothing, and StackHawk offers a free entry tier. Proof based confirmation was weighted heavily in ranking because false positive burden is the main reason DAST programmes lose developer trust and die.
Fix the scope first: list the applications and APIs that matter, their authentication patterns, and where they run, because a scanner that cannot log into your application tests only the lobby. Trial on your hardest application, not the marketing site: the single page app behind SSO with an API behind that is the real exam, and crawl coverage there predicts programme value. Judge the findings, not the dashboard: run two finalists against the same application and compare confirmed, actionable issues against noise, then show both reports to the developers who must fix them and ask which they would act on. Wire the winner into the pipeline and the tracker, with severity based service levels and an exception process, because findings in a console nobody opens are an audit artefact, not security. Keep manual penetration testing in the programme: DAST finds the known patterns tirelessly, and humans find the business logic flaws no scanner sees. Finally, keep written authorisation and scan windows documented, especially for production scanning, so the security programme itself never becomes the incident.
Frequently asked questions
What is the difference between DAST and SAST?
SAST reads source code for flaws before the application runs. DAST attacks the running application from outside, finding what is actually exploitable in the deployed system, including configuration and authentication problems code reading cannot see. Mature programmes run both, plus composition analysis for libraries.
Is OWASP ZAP good enough for a small company?
For many, yes. ZAP scans competently, automates well in CI, and costs nothing; the price is human triage time on noisier findings. A small team that runs ZAP weekly and fixes what it finds is ahead of a company that bought an enterprise platform and scans at Christmas.
Can DAST break my production site?
Scanners send attack traffic, and fragile applications can suffer, which is why tools offer safe modes, throttling, and scan windows, and why serious programmes scan staging continuously and production carefully under authorisation. Test the scanner against staging first and agree exclusions for destructive actions such as form submissions that create real records.
Does DAST cover APIs?
Yes, modern DAST tests APIs directly, importing OpenAPI or Postman definitions to reach endpoints a crawler would never find. Invicti, Acunetix, InsightAppSec, Qualys, and StackHawk all treat API testing as core, because the API is now the application.
How much do DAST tools cost?
Enterprise platforms price by applications scanned on annual contracts, typically five figures for a real estate, with Acunetix and Burp Enterprise also quote led. ZAP is free, and StackHawk publishes developer friendly tiers with a free start. Get the per application maths for your full estate before comparing headline quotes.
How often should we run DAST scans?
Continuously in the pipeline for changes, StackHawk style, plus scheduled deep scans of production facing applications weekly to monthly, and always after major releases or infrastructure changes. The right rhythm is the one your fix capacity can honour; findings ageing in a queue help no one.
Sources we checked (0)
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has 5+ years in B2B and SaaS SEO. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.
 Burp Suite Enterprise
 Veracode DAST