How we make this list: we compare pricing pages, product documentation and public user reviews. Rankite is independent; if a vendor ever pays for a featured spot, that listing is clearly labeled Partner.
Key takeaways
- GRC splits into two tiers: compliance automation for SOC 2 and ISO 27001, and enterprise GRC suites for full risk programs.
- Vanta and Drata lead compliance automation; AuditBoard and OneTrust lead enterprise GRC.
- Pricing is almost always quote-based: expect ~$8K to $15K/year for automation and $30K+ for enterprise suites.
- Thoropass is the only platform here that bundles the actual audit, with its in-house CPA firm signing the report.
GRC stands for governance, risk and compliance, and the software splits into two camps. Compliance-automation platforms get cloud companies SOC 2 or ISO 27001 ready by collecting evidence and monitoring controls continuously. Full GRC suites add enterprise governance, risk registers and audit workflows for companies with dedicated risk teams. Buy the wrong tier and you either overpay or outgrow the tool in a year. These eight cover both tiers, from startup automation to enterprise suites.
#1
Vanta
Best for: startups and growth companies automating SOC 2
Visit vanta.com
Starting priceFrom ~$10,000/year
Free planNo
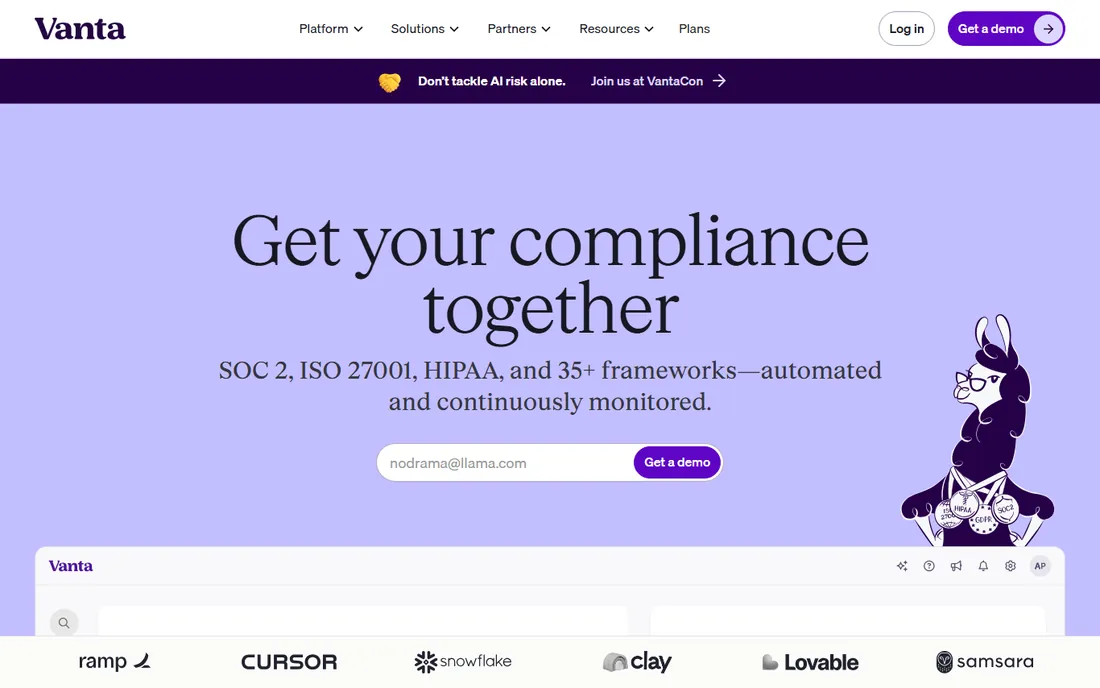
Vanta is the most widely adopted compliance-automation platform, with the broadest integration library in the category: connect your cloud stack and it collects evidence and monitors controls continuously for SOC 2, ISO 27001, HIPAA and more. The trust center lets you share security posture with prospects.
Pricing starts around $10K a year and climbs with company size; the audit itself is billed separately by a licensed CPA firm. For tech-heavy startups that need a SOC 2 report to close deals, Vanta is the default choice. The network effect matters here too: auditors and prospects already know the platform, which smooths the audit and the sales conversations that follow it.
What we like- Largest integration library (375+)
- Continuous monitoring
- Trust center included
Watch out for- Pricing behind a sales call
- Audit fees separate
- Can be overkill for tiny teams
#2
Drata
Best for: engineering-led teams wanting deep automation
Visit drata.com
Starting priceFrom ~$10,000/year
Free planNo
Drata competes head-on with Vanta on automated evidence collection, with a design-forward interface and multi-framework roadmaps that let teams work toward SOC 2, ISO 27001, HIPAA and PCI DSS together. The Drata Agent checks endpoint posture across company devices.
Pricing is comparable to Vanta, from around $10K a year. Teams that prefer Drata's monitoring UX and autopilot evidence collection tend to stay. Evaluate both on a demo before committing, since switching costs are real.
What we like- Strong continuous monitoring UX
- Multi-framework programs
- Endpoint posture via Drata Agent
Watch out for- Pricing behind a sales call
- Audit fees separate
- Some features need higher tiers
Starting priceFrom ~$8,000/year
Free planNo
Secureframe positions itself on speed: guided onboarding, training bundled in, and AI-assisted security questionnaires that cut the time to audit readiness. It covers the standard frameworks, SOC 2, ISO 27001, HIPAA, PCI DSS and GDPR.
Entry pricing runs around $8K a year, with quotes scaling up. For teams without internal security expertise that need hand-holding to the first audit, the guided approach justifies itself. Self-sufficient teams may prefer Vanta or Drata's deeper automation.
What we like- Guided setup with training
- AI-assisted questionnaires
- Fast time-to-audit
Watch out for- Pricing custom
- Audit fees separate
- Smaller integration library than Vanta
Starting priceEnterprise pricing (quote)
Free planNo
AuditBoard is the enterprise GRC standard: a connected risk platform for internal audit, SOX compliance and enterprise risk workflows, not just SOC 2 automation. It serves companies with dedicated audit and risk teams managing controls across departments.
Pricing is enterprise quote-based, commonly cited in the tens of thousands per year. If your trigger is "the board wants an enterprise-wide control inventory," this is the tier you buy. If your trigger is "we need a SOC 2 report," buy Vanta or Drata instead.
What we like- Purpose-built audit management
- Connected risk platform
- SOX compliance strength
Watch out for- Enterprise pricing only
- Not a startup tool
- Implementation takes time
Starting priceFrom ~$20,000/year (quote)
Free planNo
OneTrust combines GRC with privacy compliance, GDPR, CCPA, consent management, and AI governance in one enterprise stack. With 50+ supported frameworks, it covers programs that span privacy, risk and compliance teams.
Pricing starts around $20K a year and climbs fast; implementation is a project, not a signup. For large organizations that need privacy and GRC under one roof, the consolidation is worth it. Smaller companies should look elsewhere.
What we like- Privacy plus GRC plus AI governance in one stack
- 50+ frameworks
- Mature enterprise platform
Watch out for- Expensive
- Complex to implement
- Overkill below enterprise scale
#6
Sprinto
Best for: global startups automating compliance on a budget
Visit sprinto.com
Starting priceFrom ~$8,000/year
Free planNo
Sprinto targets early-stage and global startups with compliance automation at a lower entry price than the category leaders. AI-driven evidence collection and monitoring cover SOC 2, ISO 27001, HIPAA and GDPR.
Pricing from around $8K a year makes it the value pick for startups that cannot justify five-figure contracts. The trade is a smaller integration ecosystem and fewer enterprise features. For first-time certification on a budget, it is worth a demo.
What we like- Budget-friendly entry pricing
- Strong for startups
- AI evidence collection
Watch out for- Smaller ecosystem than Vanta or Drata
- Audit fees separate
- Fewer enterprise features
Starting priceFrom ~$12,000/year
Free planNo
Hyperproof serves mid-market teams with broad framework needs, including FedRAMP alongside the usual SOC 2, ISO 27001, HIPAA and PCI DSS. Hypersync automates evidence collection, and cross-framework mapping means one control satisfies multiple audits.
Pricing from around $12K a year puts it between startup tools and enterprise suites. For regulated mid-market companies juggling multiple frameworks, the mapping alone can justify the cost. Teams facing their first FedRAMP or multi-framework audit get particular value from the cross-framework automation.
What we like- Wide framework coverage including FedRAMP
- Hypersync evidence collection
- Cross-framework mapping
Watch out for- Pricing custom
- Mid-market focus
- Audit fees separate
#8
Thoropass
Best for: teams that want one vendor for software plus the audit
Visit thoropass.com
Starting priceCustom (audit bundled)
Free planNo
Thoropass is the only platform here that sells you the actual audit: its in-house AICPA-licensed firm signs the SOC 2 report, so software and attestation come from one vendor. That changes the math, since everyone else bills the audit separately.
Pricing is custom with the audit bundled; the Launch package is cited around $9,995 a year. The trade is auditor flexibility: you use their firm. For teams that want one throat to choke from kickoff to signed report, it is the simplest path.
What we like- In-house AICPA firm signs the report
- Single vendor for platform and audit
- AI automation included
Watch out for- Pricing custom
- Audit tied to their firm
- Less flexibility in auditor choice
Start with your trigger. If it is "we need a SOC 2 report to close deals," you want compliance automation: Vanta, Drata, Secureframe, Sprinto or Thoropass. If it is "the board wants enterprise-wide risk governance," you want a GRC suite: AuditBoard, OneTrust or Hyperproof. Buying a suite for a SOC 2 need wastes money; buying automation for an enterprise risk program wastes a year.
Budget for the audit separately. Every platform here except Thoropass bills the audit through a licensed CPA firm on top of the license. First-time SOC 2 audits commonly add five figures to the year-one cost. Ask each vendor for their auditor partner list and typical audit fees before signing.
Watch the renewal. Several buyers report year-two price increases as headcount grows, since most platforms price partly on employee count. Get the renewal terms in writing, and ask what happens to pricing if you add frameworks mid-contract. The demo price is rarely the year-two price.
Pilot before you commit. Most vendors offer a trial or demo environment: connect a handful of integrations, run one framework's controls, and see how much evidence collection is truly automated versus manual. The quality of the automation is the whole product, and it varies more between vendors than the marketing suggests. A two-week pilot reveals more than ten sales calls.
Frequently asked questions
What is GRC compliance software?
GRC stands for governance, risk and compliance. The software manages controls, evidence, audits, risks and policies across frameworks like SOC 2, ISO 27001, HIPAA, GDPR and SOX. It splits into compliance-automation platforms for certifications and enterprise GRC suites for full risk programs.
What is the best GRC platform for startups?
Vanta and Drata are the most adopted for startups pursuing SOC 2, with Sprinto as the budget alternative. Thoropass suits startups that want the audit bundled with the software. All price from around $8K to $10K a year plus separate audit fees, except Thoropass.
What is the difference between Vanta and AuditBoard?
Vanta automates compliance evidence for certifications like SOC 2, targeting startups and growth companies. AuditBoard is an enterprise GRC suite for internal audit, SOX and risk management across large organizations. They serve different company sizes and different problems.
How much does GRC compliance software cost?
Compliance-automation platforms typically run ~$8K to $15K a year for startups and mid-market, with audit fees separate. Enterprise GRC suites run $30K to $150K+ a year. Almost every vendor hides exact pricing behind a sales call, so treat published figures as starting points.
Do these platforms perform the audit themselves?
No, except Thoropass, whose in-house AICPA firm signs the report. Vanta, Drata, Secureframe, Sprinto and Hyperproof prepare you for the audit; a licensed CPA firm you hire separately performs it and bills separately. Factor audit fees into the total budget.
Which GRC platform covers the most frameworks?
OneTrust supports 50+ frameworks across privacy, GRC and AI governance. Among automation platforms, Vanta, Drata and Hyperproof cover the standard set, SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, with Hyperproof adding FedRAMP. Match the framework list to the ones you actually need.
Quick comparison
| Tool | Best for | Starting price | Free plan |
|---|
| Vanta | startups and growth companies automating SOC 2 | From ~$10,000/year | No |
| Drata | engineering-led teams wanting deep automation | From ~$10,000/year | No |
 Secureframe | teams wanting guided onboarding and fast audit prep | From ~$8,000/year | No |
 AuditBoard | enterprise internal audit, SOX and risk teams | Enterprise pricing (quote) | No |
 OneTrust | enterprises running full GRC and privacy programs | From ~$20,000/year (quote) | No |
| Sprinto | global startups automating compliance on a budget | From ~$8,000/year | No |
 Hyperproof | framework breadth for mid-market compliance teams | From ~$12,000/year | No |
| Thoropass | teams that want one vendor for software plus the audit | Custom (audit bundled) | No |
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.
Sources we checked (10)
- https://aitoolgiant.com/reviews/best-ai-soc2-compliance-automation-tools-2026.html
- https://kurums.com/best-grc-compliance-software-2026-comparison/
- https://github.com/traztech-inc/awesome-compliance-automation
- https://github.com/ishandutta2007/awesome-governance-risk-n-compliance
- https://www.sitepoint.com/best-soc-2-software/
- https://vanta.com
- https://drata.com
- https://secureframe.com
- https://auditboard.com
- https://www.onetrust.com/
Is your product missing or out of date?
We review this list regularly. Vendors can request a listing, send updated pricing or ask about featured placement.

Shihab Mia · Founder, Rankite
Shihab has spent more than a decade helping SaaS and e-commerce brands grow through search. He writes Rankite's software buying guides from pricing pages, documentation and public user reviews. More about Shihab.